PCI DSS network segmentation testing cost depends on the boundaries you need to validate, the access needed to test them, and how often testing must be repeated. A useful quote separates segmentation testing from broader penetration testing, remediation, and assessment work. Otherwise, two apparently similar prices may cover very different jobs.
Table of Contents
Copy the boundary-test scope record before requesting comparable quotes.
Public pricing provides a reference point, but not a reliable standalone market average. In its September 2026 pricing article, checked on 23 October 2026, Invadel advertises an internal network penetration test that includes segmentation testing from $6,000, with a retest included. That is a bundled starting price from one supplier—not the standard price for testing a single segmentation boundary.
For a usable budget, request a written scope and calculate the annual cost, including scheduled tests, testing after segmentation changes, internal preparation, and follow-up work. This guide covers procurement for US and UK organizations; obtain local quotes rather than converting a dollar example into a supposed UK market rate.
What are you actually paying to test?
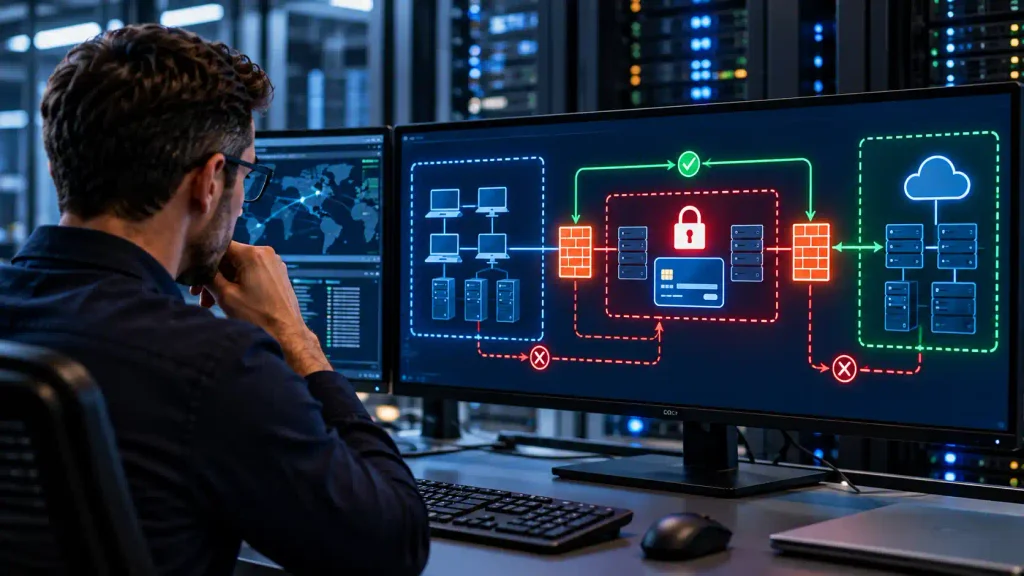
Segmentation testing checks whether the controls separating the cardholder data environment, or CDE, from out-of-scope systems work in practice. The commercial scope should explain where testers will start, which boundaries they will examine, and how they will document the result.
A network diagram showing separate VLANs does not establish that isolation is effective. The PCI Security Standards Council’s guidance on VLANs and segmentation explains that adequacy depends on the controls and configuration in the particular environment. Naming a network “payment VLAN” is a useful label, not evidence.
Before requesting prices, distinguish a segmentation-only engagement from an internal penetration test that also examines other attack paths. For help comparing broader engagements, use this guide to small-business penetration testing costs and quote scope.
How to interpret published prices
The published Invadel pricing breakdown lists its $6,000 starting package as internal network testing including segmentation. A buyer cannot infer the segmentation-only fee by subtracting an assumed value for the other work. Shared preparation, access, and reporting can affect the combined price.
The reviewed sources do not establish a representative standalone US or UK price range. Treat a supplier’s advertised starting figure as an invitation to scope the work. Confirm currency, tax or VAT treatment, travel, report delivery, and retest conditions in the proposal.
| Quote type | What to clarify |
|---|---|
| Segmentation-only test | Which boundaries, starting locations, and controls are covered? |
| Internal penetration test with segmentation | Is segmentation explicitly included in the methodology and report? |
| Recurring testing agreement | How many scheduled rounds and change-triggered tests are included? |
| Assessment or compliance package | Is technical testing performed, subcontracted, or excluded? |
Keep the testing budget within the wider program budget. The guide to PCI DSS compliance costs for small businesses separates professional services from security tooling, internal labor, and remediation—items that can otherwise disappear behind one headline fee.
Testing frequency changes the annual cost
Under the defined approach in PCI DSS v4.0.1, Requirements 11.4.5 and 11.4.6, segmentation testing applies when segmentation isolates the CDE from other networks. The baseline interval is at least every 12 months; service providers must test at least every six months. Both also require testing after changes to segmentation controls or methods.
Coverage must include all segmentation controls and methods in use, follow the entity’s methodology, and establish effective isolation. Testing must be performed by a qualified, organizationally independent internal or external resource; QSA or ASV status is not required.
For budgeting, distinguish a scheduled round, a test following a segmentation change, and a retest of a corrected finding. A contract including one remediation retest does not necessarily include testing a newly introduced network design. Ask the supplier to define those commercial boundaries.
What changes the scope and the quote?
Use the following questions to compare proposals. They are procurement prompts, not a formula that assigns a fixed price to each firewall or subnet.
| Scope question | Budget implication |
|---|---|
| How many distinct starting networks need coverage? | Confirm access setup and execution time for each. |
| Are there multiple sites, cloud accounts, or CDEs? | Request an explicit breakdown of environments and ownership. |
| Which isolation technologies are used? | Ask how the proposal covers each method. |
| Are diagrams and rule inventories current? | Separate discovery work from testing a documented scope. |
| Are testing windows restricted? | Check out-of-hours charges and scheduling assumptions. |
| What report and follow-up support are included? | Price evidence delivery and assessor questions upfront. |
For example, a corporate network, guest wireless network, and development environment may require different test access arrangements. A proposal that assumes one remote connection should explain how that access supports the intended coverage. Resolve the mismatch before booking the engagement.
Also identify systems that administer or support the payment environment. Do not classify a system as out of scope solely because it does not store card numbers. The Council’s explanation of scoping and segmentation principles emphasizes reducing exposure while correctly identifying the systems that still need protection.
Build a budget that includes the second invoice
Annual budget = scheduled testing + change-triggered testing + chargeable retests + internal labor + remediation + expenses and applicable taxes.
The following is a hypothetical US planning example, not a vendor quotation or market benchmark. Assume a merchant obtains a USD 4,000 segmentation-only quote, expects no segmentation changes during the budget year, and reserves USD 1,000 for follow-up testing if needed.
Scroll the table horizontally on small screens. Keyboard users can focus the table region and use the arrow keys.
| Same hypothetical plan | Budget treatment | USD |
|---|---|---|
| One scheduled supplier-performed segmentation test | Expected external cash | 4,000 |
| Preparation: 12 hours × $75 | Allocated existing internal capacity | 900 |
| Remediation: 16 hours × $75 | Allocated existing internal capacity | 1,200 |
| Resource estimate before reserve | $4,000 cash + $2,100 allocated capacity | 6,100 |
| Follow-up testing reserve | Contingency; not an incurred charge | 1,000 |
| Cash funding envelope including reserve | $4,000 expected cash + $1,000 reserve | 5,000 |
| Resource envelope including reserve | $6,100 resource estimate + $1,000 reserve | 7,100 |
The subtotal and envelope rows are alternative views, not additional charges to add together. Existing staff time does not automatically increase payroll cash; if that work is outsourced, record the invoice as external cash instead. Unused reserve is not an expense.
This example excludes taxes, travel, new equipment, and broader PCI assessment work. It also assumes the remediation stays within the stated hours. If the test exposes a design problem requiring new infrastructure, replace that allowance with an engineering estimate.
For a hypothetical service provider buying two scheduled rounds at the same assumed USD 4,000 price, scheduled testing alone becomes USD 8,000. Preparation and follow-up effort must then be estimated for both rounds. Any changes during the year need their own allowance.
A UK team can use the same calculation with actual GBP quotations and its own labor costs. Record whether each quote includes VAT and whether the budget tracks gross cash expenditure or net cost.
What the written proposal should include
- A coverage schedule: CDEs, source networks, locations, and segmentation methods covered, with explicit exclusions.
- Access and authorization: approved targets, third-party permissions where needed, testing windows, emergency contacts, and stop conditions.
- A reporting commitment: methodology, test locations, results, limitations, supporting evidence, and clear findings.
- Tester information: relevant experience and an explanation of organizational independence.
- Retest terms: included rounds, deadlines, scope limits, and the charge for additional work.
- Commercial terms: currency, taxes, expenses, cancellation fees, report turnaround, and follow-up support.
Request a redacted example report before choosing a supplier. You should be able to understand what was tested and what could not be tested without reconstructing the engagement from a short pass/fail statement.
Requirement 11.4.4 calls for correction of exploitable weaknesses and repeat testing to verify the corrections. A report delivered before that work is complete should not be mistaken for evidence that the issue has been resolved.
Copy one boundary-test scope record
Repeat this entry for each distinct starting environment and boundary in the agreed methodology. Keep operational details in your controlled project record; do not publish real network addresses or credentials in a public worksheet.
Proposal / scope version / boundary ID:
Starting environment and authorized access arrangement:
CDE destination and control methods to validate:
Expected isolation / permitted communication:
Shared identity, administration and supporting dependencies:
Included test coverage / exclusions / unresolved access:
Approved window / stop and escalation contacts:
Scheduled round, post-change test or remediation retest:
Initial fee / recurring rounds / extra-change pricing:
Retest conditions / included attempts / expiry:
Required evidence and report / actual tested limits:
Finding, correction and verification references:
Confirmation owner / outstanding question / due date:
A starting connection that cannot exercise the intended boundary leaves a coverage question. Resolve and price that gap before accepting the proposal; an included remediation retest is not automatically a test of a later network redesign.
Reduce cost by removing uncertainty from the scope
Prepare current network and payment-flow diagrams, identify the owners of relevant controls, and arrange approved test access before fieldwork. Ask the supplier to identify missing inputs during scoping, when they can still be addressed without losing a booked testing window.
If your internal penetration test is already scheduled, request a combined proposal with segmentation coverage shown explicitly. Compare the total against separate engagements. Shared preparation may help, but the proposal should demonstrate the saving rather than simply promise a discount.
For online stores, review the payment architecture before pricing a large testing project. This guide to PCI DSS costs for ecommerce stores explains how checkout design affects the broader compliance workload. Any proposed scope reduction still needs to match the actual environment.
Finally, send the same scope brief to competing suppliers. Ask each to price the initial engagement, the annual schedule, a remediation retest, and a future segmentation change separately. You will then have a cost comparison you can use—and a clearer answer to what the money actually buys.
Cost example and scope worksheet reviewed: 2026-10-23. Rechecked the linked Invadel bundled starting price, separated cash, internal capacity and reserve in the hypothetical budget, and added a boundary-test record. The standard reference now points to the PCI SSC Document Library. No test was performed or supplier quote obtained.