What Is Kioptrix? A Safe Beginner Lab Guide

Kioptrix is a vulnerable-VM practice series. Start learning: Level 1 setup → seven-session roadmap. Business security: compliance guides.
Practical cybersecurity guides, labs & compliance
Kioptrix is a vulnerable-VM practice series. Start learning: Level 1 setup → seven-session roadmap. Business security: compliance guides.
If you failed a CMMC Level 2 assessment, the remediation cost is not a single consulting fee. Your real budget may include internal engineering time, control changes, evidence and System Security Plan updates, new security tooling, remediation support, and either a POA&M closeout assessment or an entirely new CMMC assessment. Key remediation rules checked: October … Read more
There is no single defensible price for FedRAMP authorization. Start with the pathway your agency customer accepts, the cloud service boundary, and the work needed to demonstrate and maintain the required security. For a provider choosing the 2026 Consolidated Rules and FedRAMP 20x, the Certification Class is a major budget input. An existing Rev5 engagement … Read more
An ISO 27001 audit does not have one universal price. The certification-body fee is driven first by the number of auditor-days required for your ISMS scope, then by complexity, locations, technology, outsourcing, travel, administration, and any extra work created by findings or scope changes. Audit-method update: October 19, 2026. ISO/IEC 27006-1:2024 is the certification-body standard; … Read more
If you need a Qualified Security Assessor for PCI DSS, do not budget from transaction volume alone. The larger cost driver is the environment the assessor must actually test: payment channels, systems touching the cardholder data environment, locations, segmentation, third parties, evidence quality, and whether penetration testing or readiness work sits inside the quote. Key … Read more
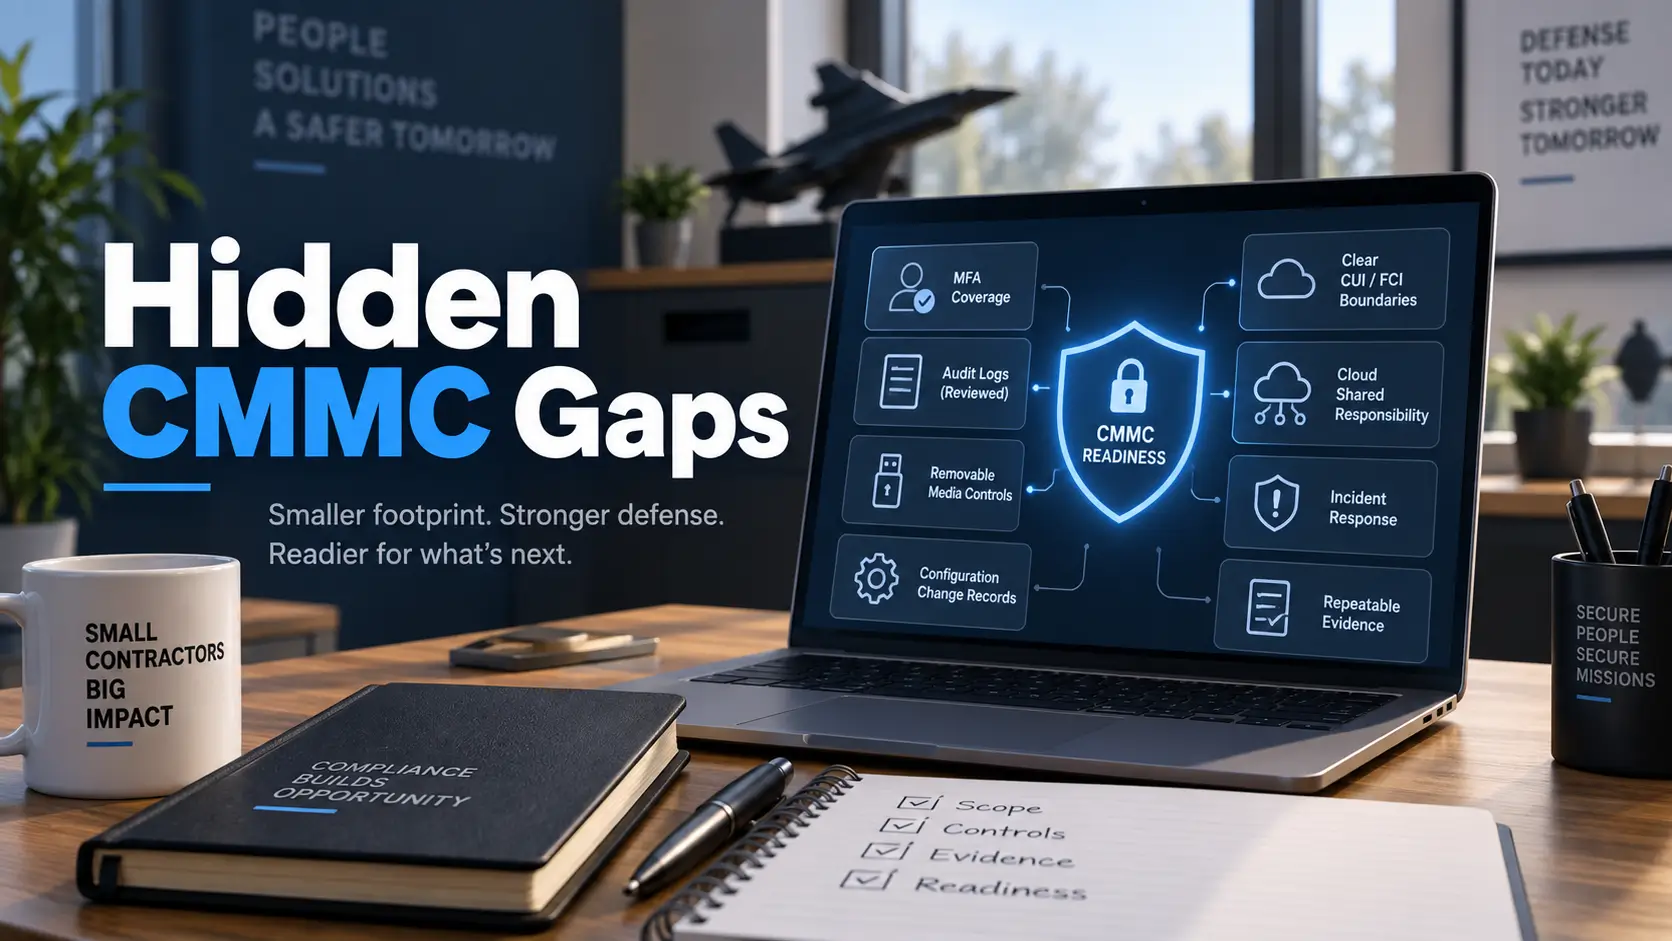
Small defense contractors rarely need a giant security stack to improve CMMC readiness. They need a tightly scoped environment, controls that actually work, and evidence showing those controls work repeatedly. The gaps that create trouble are often quieter than an unpatched server: incomplete MFA coverage, logs nobody reviews, undocumented configuration changes, unmanaged removable media, unclear … Read more
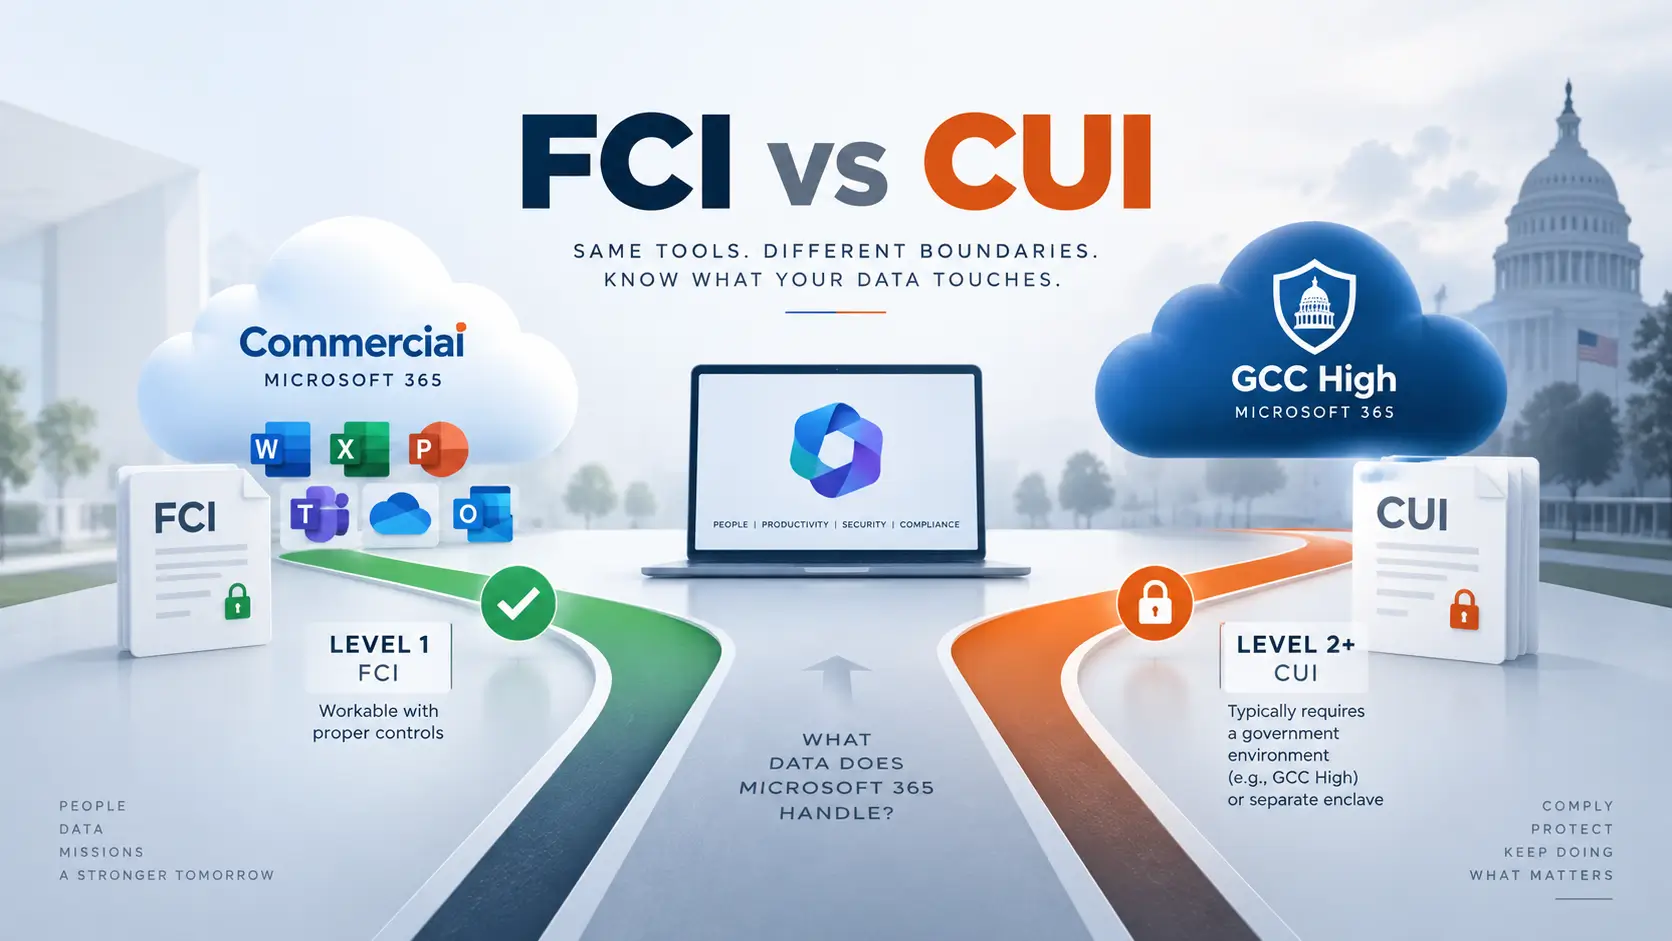
If your organization uses Microsoft 365 Commercial and CMMC suddenly appears in a DoD contract or prime-contractor flowdown, the first question is not “Do we need GCC High?” It is “Will Federal Contract Information or Controlled Unclassified Information enter Microsoft 365?” Microsoft guidance checked: October 19, 2026. Microsoft’s CMMC guidance and May 2026 cloud comparison … Read more
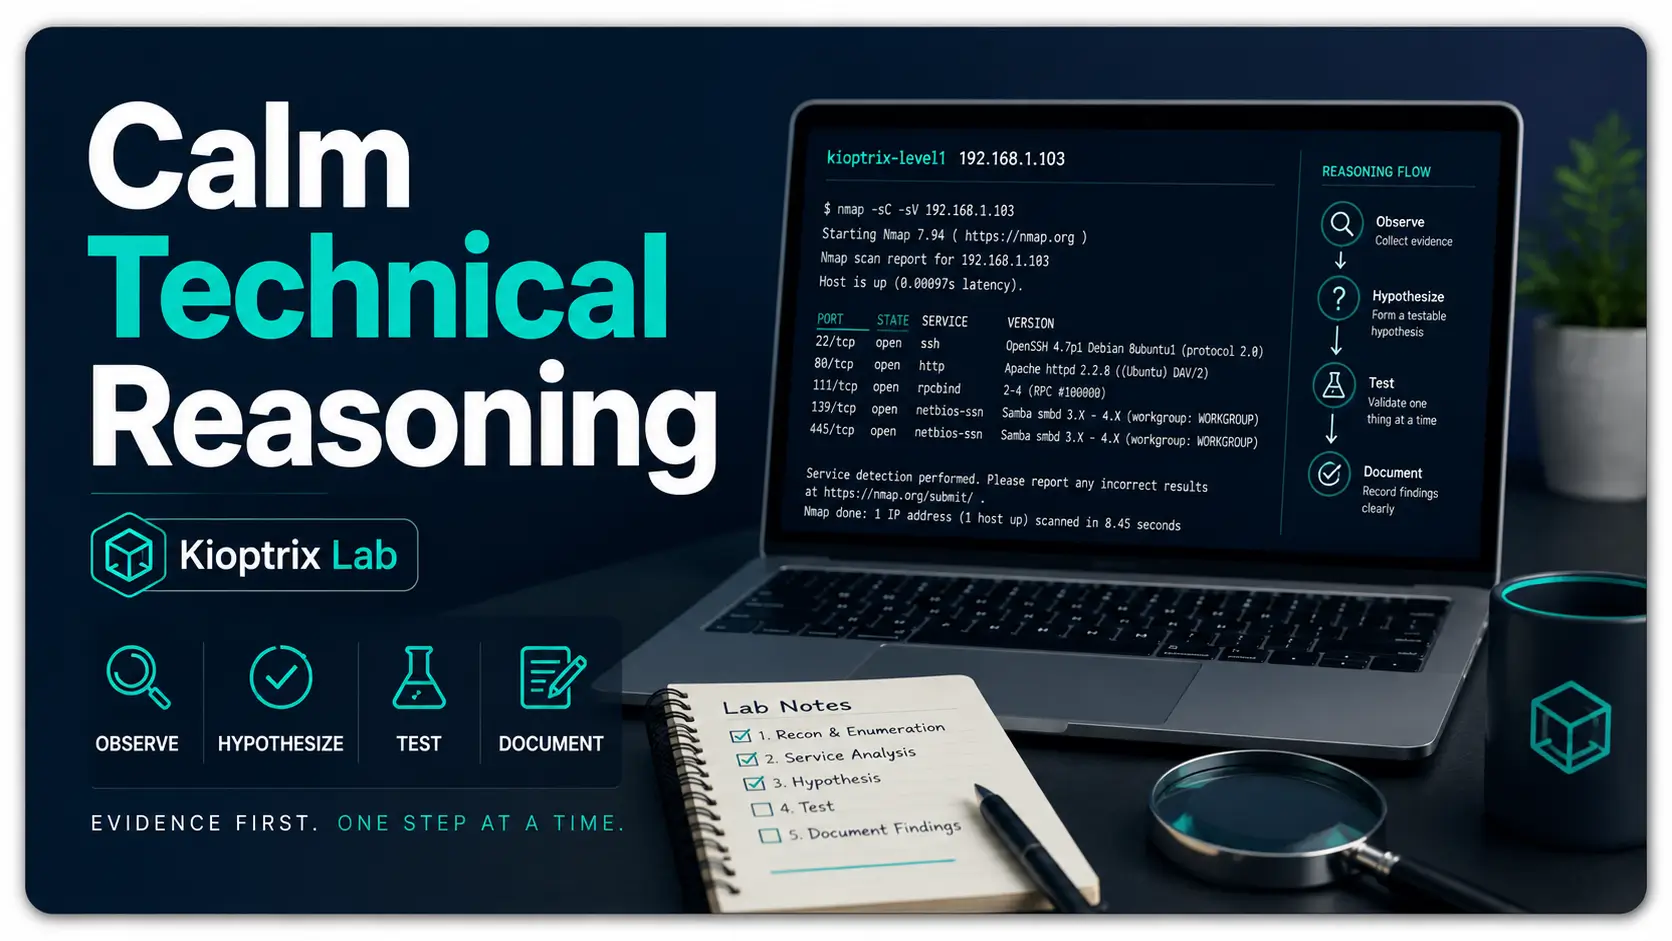
Evidence-first cybersecurity practice Why Kioptrix Level Is Goodfor Practicing Calm Technical Reasoning A vulnerable virtual machine can make a beginner feel as though twenty alarms are ringing at once. Ports appear, banners offer cryptic clues, scanners disagree, and every search result seems to shout, “Run this next.” Kioptrix Level is valuable because it gives you … Read more
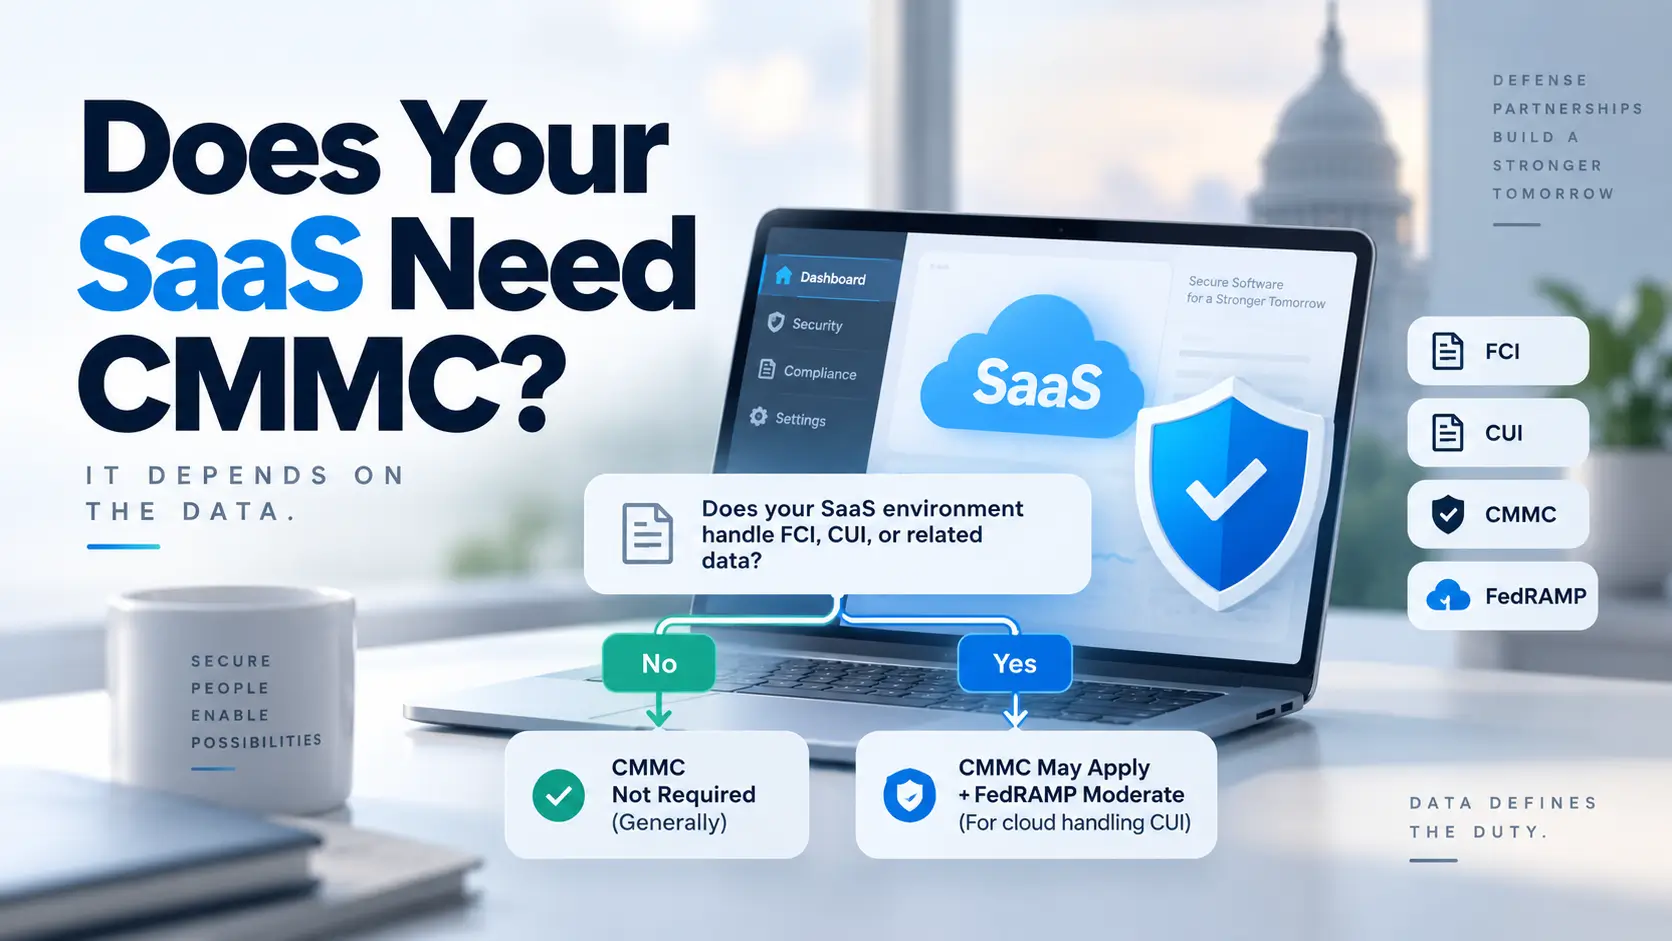
Short answer: a SaaS vendor does not need CMMC simply because it sells software to a defense contractor. The requirement turns on what information the SaaS environment will process, store, or transmit, how the vendor participates in the DoD contract, and what CMMC level the contract or subcontract requires. Key SaaS distinctions reviewed: October 19, … Read more
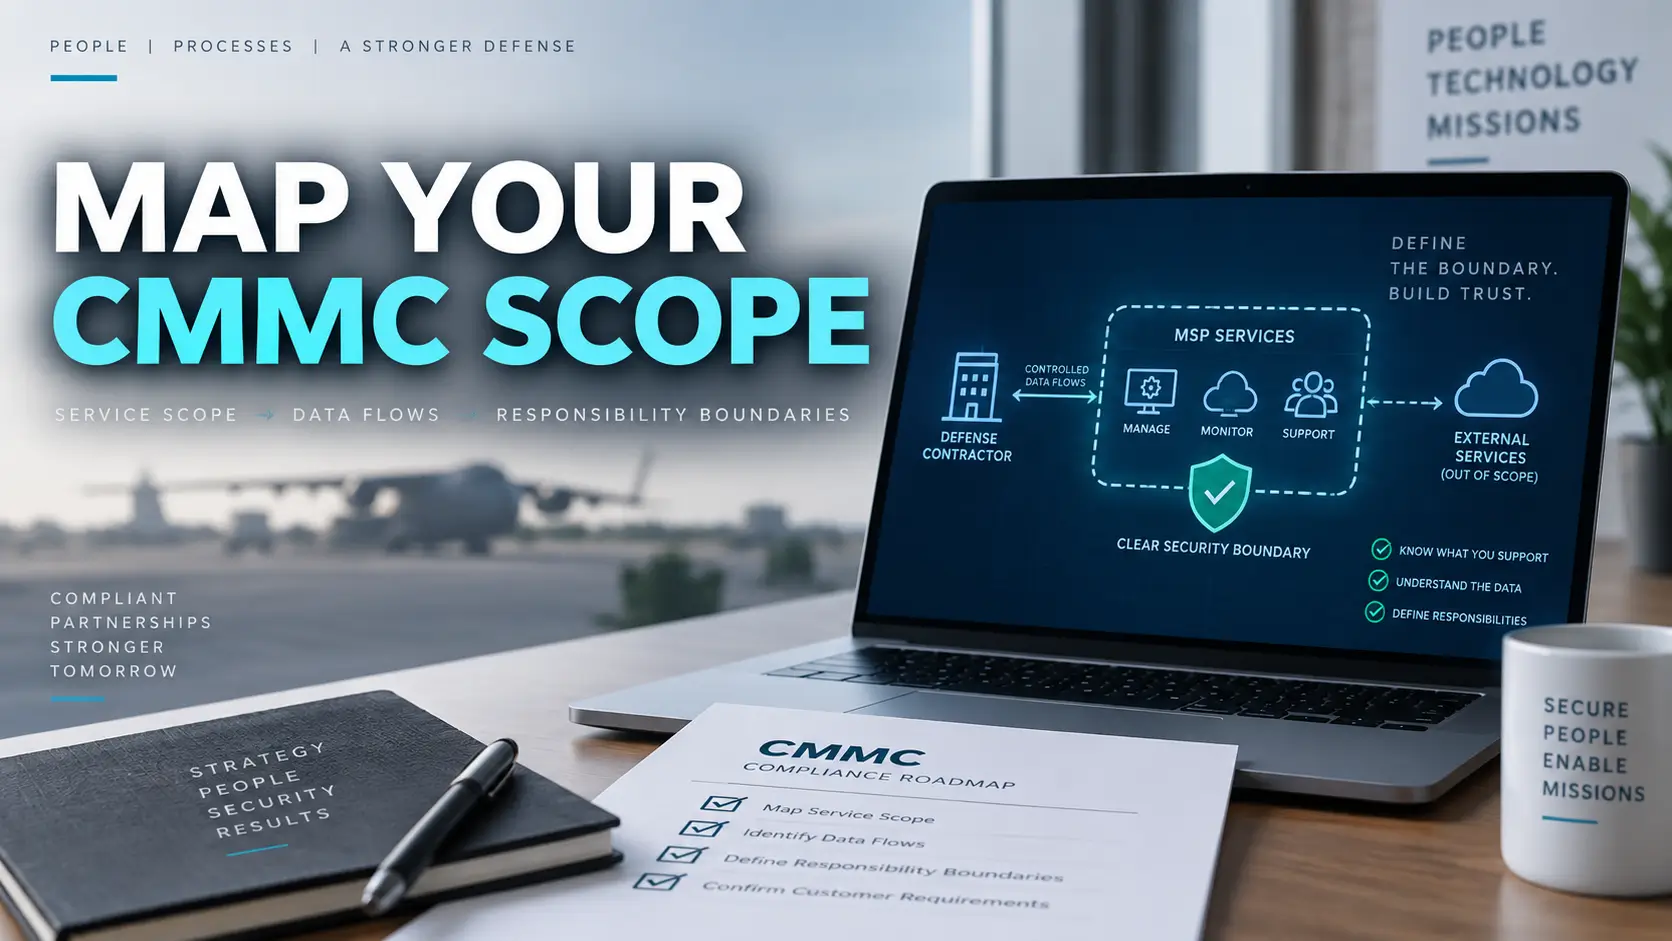
An MSP serving defense contractors does not automatically need its own CMMC certification. The decisive question is what the MSP actually does with Federal Contract Information (FCI), Controlled Unclassified Information (CUI), and Security Protection Data (SPD), and whether the provider is functioning as an MSP, another type of External Service Provider (ESP), or a Cloud … Read more
Run a 30-minute ransomware tabletop exercise with five scenario cards, a cooperative scorecard, and a practical action log for your small team.