A PCI DSS Self-Assessment Questionnaire, usually shortened to SAQ, is not a generic security checklist that every business completes in the same way. It is a PCI DSS validation tool designed for eligible merchants and service providers, and the correct questionnaire depends on how your organization accepts payments, where account data travels, what systems can affect payment security, and what your acquiring bank or other compliance-accepting entity requires.
Table of Contents
Useful starting points: compare SAQ environments, review evidence quality, and copy the validation-path confirmation brief before selecting or submitting a questionnaire.
The safest starting point is therefore not “Which SAQ is shortest?” It is “What does our payment environment actually look like?” Choosing the wrong questionnaire can leave important PCI DSS requirements outside the assessment even if every box on the form is checked.
As checked on November 16, 2026, PCI DSS v4.0.1 is the operative PCI DSS revision, and organizations using an SAQ should use the current questionnaire and instructions available through the PCI Security Standards Council Document Library. PCI SSC advises merchants to confirm that they satisfy every eligibility criterion for the selected SAQ and to check their validation requirements with the organization that will accept the assessment.
What Is a PCI DSS Self-Assessment Questionnaire?
A PCI DSS SAQ is a structured method for an eligible organization to assess and report its own compliance with the PCI Data Security Standard. Different SAQs exist because a small shop using isolated payment terminals does not present the same payment-security environment as an ecommerce company running its own checkout application.
PCI SSC explains that SAQs are intended for SAQ-eligible merchants and service providers and that each questionnaire includes eligibility criteria describing the environment for which it was designed. You must satisfy all applicable criteria, not merely most of them. The Council’s official explanation of PCI DSS SAQs is worth reading before choosing a form.
There is another distinction that saves a surprising amount of confusion: completing an SAQ is not the same thing as obtaining a generic “PCI certificate.” PCI SSC recognizes its formal validation documents, including SAQs, Attestations of Compliance, and Reports on Compliance. A vendor-generated badge or certificate does not replace the required PCI SSC reporting forms.
If you are still deciding whether you can self-assess or need a more formal assessment route, see the related Kioptrix guide to PCI DSS assessment cost and the difference between an SAQ and a ROC. The validation route can materially change both the work involved and the budget.
The First Question Is Not the SAQ Type
Before opening any questionnaire, identify the organization that expects your PCI DSS validation. This may be your acquiring bank, payment processor acting under an acquiring program, payment brand, or another compliance-accepting entity.
Ask that organization what it expects you to submit. Depending on the program and your environment, the answer might include an SAQ, an Attestation of Compliance (AOC), Approved Scanning Vendor results, or another form of validation.
PCI SSC’s official self-assessment workflow specifically directs merchants to identify the applicable SAQ, confirm scope and eligibility, perform the required assessment activities, complete the SAQ and AOC, obtain applicable ASV scans, and submit the required documents to the appropriate compliance-accepting entity.
This distinction matters because PCI SSC publishes the security standard and validation tools, while payment brands and acquiring organizations operate their own compliance programs. A blog article, consultant, software portal, or payment gateway should not be treated as the final authority on which validation document your business is required to submit.
Map Your Payment Flow Before Choosing an SAQ
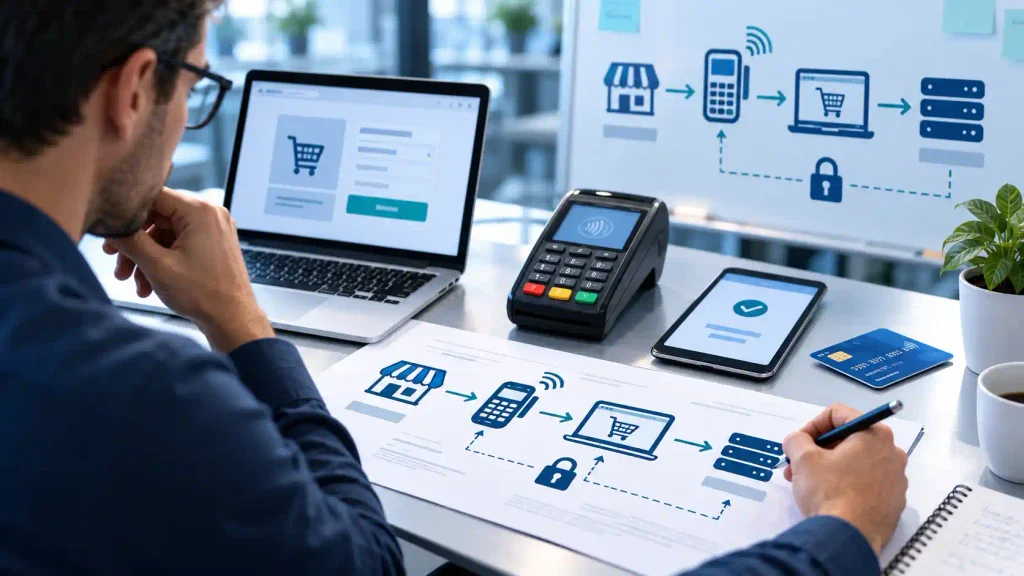
Your SAQ is largely a consequence of your payment architecture. Draw the path a payment takes before trying to classify the environment.
- Where does the customer enter the card number?
- Does the payment page run on a website you control?
- Does your website redirect the customer to a payment provider?
- Does a payment provider supply an embedded iframe or hosted payment form?
- Does your server receive account data before passing it to a processor?
- Do employees manually enter card information into a virtual terminal?
- Do you use standalone payment terminals connected by telephone or IP networks?
- Do any databases, logs, recordings, emails, spreadsheets, support tools, or backups contain payment account data?
- Which third parties store, process, transmit, or otherwise support the security of payment account data?
Do not rely only on what the checkout page looks like to the customer. Two stores can display nearly identical “Pay Now” screens while sending payment data through very different technical paths.
If you are estimating the staffing, scanning, remediation, and tooling costs that follow from this scope, the Kioptrix PCI DSS compliance cost guide for small businesses explains why payment architecture often matters more than company size.
PCI DSS SAQ Types at a Glance
The following table is a navigation aid, not an eligibility determination. Always compare your actual environment with every eligibility criterion in the current PCI SSC questionnaire before using a particular SAQ.
| SAQ | Typical environment | Important limitation |
|---|---|---|
| SAQ A | Eligible card-not-present merchants outsourcing account-data functions to compliant third parties | The merchant must satisfy the current SAQ A eligibility criteria; outsourcing does not eliminate all merchant responsibilities |
| SAQ A-EP | Eligible ecommerce merchants whose websites can affect payment security but do not directly receive account data | Broader website security responsibilities generally apply than under SAQ A |
| SAQ B | Certain merchants using imprint machines or eligible standalone dial-out terminals | Only specific payment environments qualify |
| SAQ B-IP | Certain merchants using eligible standalone IP-connected payment terminals | Terminal and network architecture must meet the stated eligibility conditions |
| SAQ C-VT | Eligible merchants manually entering transactions into an Internet-based virtual terminal | Designed for a narrowly defined virtual-terminal environment |
| SAQ C | Eligible merchants with payment applications connected to the Internet | Environment must satisfy the complete SAQ C eligibility criteria |
| SAQ P2PE | Eligible merchants using a validated PCI-listed Point-to-Point Encryption solution | Using encryption alone does not automatically create SAQ P2PE eligibility |
| SAQ SPoC | Eligible merchants using a PCI SSC-listed Software-based PIN Entry on COTS solution | Verify the specific solution listing and lifecycle; see the October 2026 sunset note below |
| SAQ D for Merchants | SAQ-eligible merchants that do not qualify for another merchant SAQ or have broader applicable requirements | Much broader assessment scope |
| SAQ D for Service Providers | SAQ-eligible service providers | This is the only SAQ available to SAQ-eligible service providers |
The table deliberately says “typical” rather than “automatically eligible.” PCI SSC maintains detailed criteria within the actual questionnaires, and a single architectural detail can change the correct path.
SAQ A: Fully Outsourced Does Not Mean Zero Responsibility
SAQ A is frequently associated with small ecommerce businesses because it can apply to card-not-present merchants that outsource applicable account-data functions to PCI DSS-compliant third parties and do not electronically store, process, or transmit account data on their own systems or premises, subject to the complete eligibility criteria.
The dangerous shortcut is to translate that into “Stripe, PayPal, or another provider handles payment, so our website is outside PCI.” That conclusion is too broad.
For ecommerce implementations, the mechanics of the integration matter. PCI SSC distinguishes between arrangements such as hosted redirects, embedded payment forms, and merchant-controlled payment-page elements. The correct questionnaire depends on the complete payment implementation rather than the logo printed on the checkout button.
The current SAQ A framework also contains an ecommerce eligibility consideration relating to attacks from scripts that could affect the merchant’s ecommerce systems. PCI SSC’s SAQ A script-security FAQ explains that this particular eligibility criterion applies to certain embedded payment-page or iframe scenarios and distinguishes them from redirects and fully outsourced payment methods.
The 2026 ASV scanning clarification
A particularly important 2026 clarification concerns external vulnerability scanning. PCI SSC states that SAQ A for PCI DSS v4.x includes applicable Approved Scanning Vendor requirements for merchant ecommerce webpages even when payment processing is outsourced and the merchant webpage redirects transactions to a third-party service provider or includes the provider’s embedded iframe.
In other words, “card data never reaches our server” and “we have no PCI scanning responsibility” are not equivalent statements. The Council’s June 2026 SAQ A ASV guidance should be reviewed by ecommerce merchants using SAQ A.
For a deeper look at how redirect, iframe, custom checkout, scanning, monitoring, and remediation can affect the budget, see the Kioptrix guide to PCI DSS compliance cost for ecommerce stores.
SAQ A-EP: When Your Website Can Affect Payment Security
SAQ A-EP addresses eligible ecommerce environments in which the merchant website does not directly receive account data but can affect the security of the payment transaction or payment page.
This distinction can be subtle. A website does not need to store card numbers in a database to influence payment security. Merchant-controlled code, server configuration, payment-page behavior, scripts, redirects, and other components can create a path through which an attacker changes what the customer sees or where payment information is sent.
That is why choosing between SAQ A and SAQ A-EP should be an architectural exercise, not a branding exercise. Document where each payment-page element originates, what code the merchant controls, and whether account data ever passes through merchant-controlled infrastructure.
A website’s ability to affect a payment is not by itself sufficient to distinguish A from A-EP. For example, SAQ A redirect environments can still affect the journey. If the relevant field origins and data path are unclear, stop before completing the questionnaire and verify the integration with your payment provider, acquirer, or a PCI-qualified professional. Resolve the uncertainty against the implemented payment flow; the time spent is not a measure of readiness.
SAQ B and B-IP: Terminal Environments Are Not Interchangeable
SAQ B and SAQ B-IP are associated with particular payment-terminal environments, but the presence of a countertop card terminal does not by itself tell you which questionnaire applies.
Traditional standalone dial-out terminals and IP-connected payment terminals create different technical exposure. An Internet Protocol connection brings network architecture into the picture, which is reflected in the existence of SAQ B-IP as a separate validation tool.
Inventory the exact payment devices, connectivity method, payment applications, network connections, storage behavior, and any other payment channels before deciding that a retail environment belongs in one of these categories.
SAQ C-VT: For Narrow Virtual-Terminal Environments
A virtual terminal is typically a browser-based interface provided by a payment processor or service provider into which an authorized employee manually enters payment information. SAQ C-VT exists for eligible merchants operating a narrowly defined virtual-terminal model.
Do not assume that every business that occasionally types a card number into a browser qualifies. Eligibility depends on the complete environment, including how the computer is used and connected and whether other payment processes or systems introduce additional scope.
A workstation used for general email, downloads, remote administration, accounting, and assorted office tasks presents a different security picture from a tightly controlled system dedicated to the qualifying payment workflow. Use the current SAQ C-VT eligibility language rather than a generic description from a compliance vendor.
SAQ C: Internet-Connected Payment Applications
SAQ C covers particular merchant environments involving payment applications connected to the Internet where the complete SAQ C eligibility criteria are satisfied.
Because this environment can include merchant-controlled payment systems, it generally requires more security work than a heavily outsourced card-not-present configuration. Network security, system hardening, access control, vulnerability management, logging, and other controls may become materially more important.
This is also where the cost of “doing PCI” can begin diverging sharply from the price of a compliance portal. The questionnaire may cost little to download, but securing and maintaining the systems represented by its answers is real operational work.
SAQ P2PE: A Validated P2PE Solution Can Reduce Scope
SAQ P2PE is intended for qualifying merchants using a PCI-listed Point-to-Point Encryption solution and satisfying the questionnaire’s eligibility criteria.
The word “listed” matters. Buying a terminal that advertises encryption is not the same thing as implementing a validated PCI P2PE solution in the manner required for SAQ P2PE eligibility.
If a vendor proposes P2PE as a scope-reduction strategy, verify the solution against PCI SSC’s official listings and document exactly which devices, applications, decryption environment, and operational procedures form part of the validated solution.
SAQ SPoC: Software-Based PIN Entry on Commercial Devices
SAQ SPoC supports eligible merchants using a PCI SSC-listed Software-based PIN Entry on COTS solution. COTS means commercial off-the-shelf devices such as smartphones or tablets.
This SAQ exists because accepting a PIN through an approved SPoC architecture differs from both a traditional payment terminal and a generic mobile card-reading setup. Eligibility is tied to the specific solution model and should be confirmed against the current SAQ and PCI SSC listings.
Lifecycle update: PCI SSC’s May 2026 SPoC/CPoC bulletin ended new solution submissions after October 31, 2026. Existing listings continue through their normal lifecycle, including applicable maintenance and expiration rules. This is not an announcement that every existing solution—or the SAQ SPoC form—became invalid overnight. Verify the exact solution’s current listing, implementation guidance and accepted validation route; do not choose an SAQ solely because the device is a smartphone.
SAQ D for Merchants: The Broad Catch-All SAQ
SAQ D for Merchants generally becomes relevant when an SAQ-eligible merchant does not meet the eligibility criteria for another merchant SAQ, or when its environment has additional applicable PCI DSS requirements beyond those represented by a narrower questionnaire.
Examples can include merchants that electronically store account data, ecommerce businesses whose own systems receive account data, and environments whose payment architecture does not fit one of the more restricted SAQs.
SAQ D should not be treated as punishment for failing to find a smaller form. It reflects a broader payment environment. If your systems have more influence over account data, the assessment naturally has more ground to cover.
Service Providers Have a Different SAQ Rule
Businesses sometimes browse the merchant questionnaires and choose the one that appears closest to their technology. Service providers should not do that.
PCI SSC states that SAQ D for Service Providers is the only SAQ available to SAQ-eligible service providers. Other SAQs are merchant questionnaires.
If your organization provides services that store, process, transmit, or otherwise affect the security of payment account data on behalf of customers, establish whether PCI DSS considers you a service provider before selecting a validation document.
How to Complete a PCI DSS SAQ Step by Step
Step 1: Confirm the validation route
Ask the organization accepting your PCI validation whether you may use an SAQ and what documentation it expects. Record the answer rather than relying on institutional memory such as “I think our old processor told us SAQ A three years ago.”
Step 2: Define the assessment scope
Identify people, processes, technologies, systems, networks, payment channels, service providers, and locations relevant to the cardholder data environment and the security of payment processing.
Create or update the payment-data-flow diagram before answering detailed controls. If you cannot show where account data enters, travels, is stored, and exits, you are not ready to make confident statements about scope.
Step 3: Test every eligibility criterion
Open the current version of the candidate SAQ and work through the eligibility criteria one by one. Do not paraphrase them into easier rules before deciding that you qualify.
- Record the criterion.
- Identify the system, configuration, contract, or evidence supporting it.
- Assign an owner who can confirm the statement.
- Flag anything uncertain.
- Resolve uncertainty before beginning the full questionnaire.
One failed eligibility condition can be more important than 100 compliant security controls because it can change which validation tool is appropriate.
Step 4: Perform the required testing instead of merely reading the controls
An SAQ is a self-assessment, not a self-opinion questionnaire. Read the expected testing associated with the requirements and gather evidence showing whether each applicable control is actually implemented.
Depending on the requirement and SAQ, evidence might include configuration settings, policies, access lists, vulnerability scan results, system inventories, service-provider documentation, training records, logging configurations, change records, or interviews with responsible personnel.
The evidence should match the claim. A policy saying administrators must use MFA does not prove that every relevant administrator account has MFA enabled. A vulnerability-management procedure does not prove that the latest required scan passed.
Step 5: Answer each requirement using the form’s actual response options
Use the response choices and instructions printed in the current questionnaire. Do not create informal alternatives such as “mostly compliant,” “planned,” or “the vendor probably handles it.”
Where a requirement is marked not applicable, document the basis required by the questionnaire. Where a control is not in place, treat that as a remediation issue rather than polishing the wording until it sounds compliant.
Step 6: Complete required technical validation
Some environments require technical testing in addition to questionnaire responses. External vulnerability scanning is a common example. Where PCI DSS requires an ASV scan, it must be performed using an Approved Scanning Vendor and the applicable PCI scanning process.
Do not substitute an ordinary vulnerability scanner, web-hosting scan, WordPress security plugin, or penetration-test report for an ASV scan when the applicable requirement specifically calls for ASV scanning.
Likewise, ASV scanning does not prove complete PCI DSS compliance. It validates a specific part of the security program. A beautiful passing scan cannot answer access-control, policy, training, logging, vendor-management, or other requirements that fall elsewhere in the assessment.
Step 7: Complete the Attestation of Compliance
The Attestation of Compliance is the formal attestation associated with the assessment. PCI SSC’s standard self-assessment process includes completion of the SAQ and AOC.
Read the attestation carefully before signing it. The signature is not merely an administrative finish line. It represents statements about the scope and results of the assessment.
Step 8: Submit exactly what the accepting entity requests
Your acquirer or other compliance-accepting organization may request the AOC, full SAQ, ASV results, or additional documentation. Follow its submission instructions rather than assuming every merchant submits the same package.
Build an Evidence Folder Before You Start Answering
The slowest SAQ is often not the longest one. It is the one completed by a business that has to rediscover every control while answering it.
Create a controlled evidence repository and organize it around the current assessment period. Useful categories can include:
- Payment-data-flow diagrams
- Cardholder data environment scope
- Asset and system inventories
- Network diagrams
- Payment-terminal inventories
- Third-party service-provider lists
- Provider AOCs or other appropriate PCI validation evidence
- Security policies and operating procedures
- User and administrator access records
- MFA configurations
- Patch and vulnerability-management records
- ASV scan reports where applicable
- Security logging and monitoring evidence
- Security-awareness records
- Incident-response documentation
- Change-management records
- Evidence supporting any not-applicable determinations
Use dates and owners. A screenshot named final-final-PCI.png is not an evidence-management strategy. A record showing the system, control, owner, collection date, assessment period, and purpose is much easier to defend and refresh next year.
Match Each SAQ Answer to Evidence You Can Review
A folder full of documents is not the same thing as a tested answer. Build a short index that links each applicable requirement to the testing performed, the systems covered, the evidence date and the person responsible. The examples below illustrate evidence quality; they do not define which controls apply to your SAQ or replace its expected testing.
| Proposed answer | What is still missing? | More useful evidence |
|---|---|---|
| “MFA is required by policy.” | Whether the relevant accounts actually enforce it. | In-scope account inventory, settings review and documented test results. |
| “Our provider is PCI compliant.” | Whether its assessed service matches the integration and responsibility allocation. | Applicable provider evidence, service mapping and customer responsibilities. |
| “The scan passed.” | Which assets, scan type, dates and findings the result covers. | Applicable passing report, scope record and remediation/rescan history. |
| “No card data is stored here.” | Whether support tools, logs, exports, backups and other channels were reviewed. | Data-flow record and documented review of relevant collection and storage paths. |
| “The control was fixed.” | Whether the fix was verified and the reason for failure addressed. | Change reference, retest result, reviewer and ongoing owner. |
Prefer a reference to a controlled evidence location over duplicating sensitive material into every working document. A reviewer should be able to identify what was checked without receiving card data, credentials or unrestricted exports. Define who may access the evidence and use the accepting entity’s approved submission channel when documents are requested.
Freshness is contextual. A screenshot taken today may still omit the relevant system, while an earlier report may describe the required assessment period correctly. Record the scope and period rather than judging evidence only by its filename or collection date.
Not Applicable Is Different from Unknown or Untested
PCI SSC FAQ 1473 distinguishes a tested conclusion that a requirement does not apply from a requirement excluded without testing. Do not translate “we do not know” into “Not Applicable.” Use the response choices and supporting explanations required by the specific current form; not every SAQ provides the same options.
If the expected testing is incomplete, keep an internal evidence gap open and follow the questionnaire’s instructions for reporting the result. A planned implementation, missing record or unanswered provider question is not proof that a requirement is satisfied. Likewise, “Not Tested,” where available, is not a convenient way to skip difficult work or a synonym for “Not Applicable.”
Example: the owner says a requirement is irrelevant, but nobody checked the environment.
Record the proposed applicability decision as unconfirmed. Identify which facts and testing would support it, assign an owner and resolve the issue before relying on a not-applicable answer. The owner’s opinion alone is not the supporting explanation.
Example: a control was enabled yesterday, but the team has not retested it.
Keep the change and verification tasks separate. Record what was changed, what remains to be tested and who reviews the result. Then use the response and documentation instructions in your actual SAQ; do not mark the control complete merely because a change ticket is closed.
Example: a provider handles the service, but the supporting evidence is missing.
Request evidence for the exact service and responsibility boundary. Outsourcing may change who performs a control; it does not establish that the control was examined or that your own configuration is correct.
Copy an Evidence-Gap and Remediation Record
Keep this working record beside the official questionnaire. It helps coordinate unresolved work without inventing new SAQ response options. Do not include cardholder data or secrets in it.
Assessment period / SAQ edition:
Requirement reference / affected system or process:
Expected testing and evidence needed:
Testing performed / date / tester:
Observation / evidence reference:
Applicability decision and supporting facts:
Unresolved question or control gap:
Responsible owner / due date / dependency:
Remediation action / change reference:
Retest method / result / date / reviewer:
Required explanation or worksheet reference:
Final response selected in the official form:
Ongoing control owner / next review trigger:
For example, a fictional store might have a current provider AOC but no evidence that the deployed checkout matches the provider’s supported integration. The provider document stays in the file; the integration gap stays open. Engineering supplies the implementation reference, the relevant eligibility conditions are reviewed, and the assessment record is updated from the actual finding. A strong document in one category does not close an unrelated gap.
For an online implementation, use the SAQ A versus SAQ A-EP checkout evidence checklist to organize field origins and submission paths. Keep this technical question separate from the merchant-level classification that influences reporting expectations.
How to Review Third-Party Payment Providers
Outsourcing payment functions can reduce your PCI DSS scope, but “our provider is PCI compliant” should be verified rather than treated as a permanent fact.
For each relevant third-party service provider, determine:
- Exactly which service the provider supplies.
- Which PCI DSS responsibilities the provider performs.
- Which responsibilities remain with your organization.
- The scope and date of the provider’s current PCI validation.
- Whether the service you actually use is covered by that validation.
- How you will monitor the provider’s status over time.
A provider’s compliance does not automatically make every customer implementation compliant. Configuration matters. A secure hosted payment product can still be integrated incorrectly, surrounded by insecure merchant systems, or combined with another payment channel that changes the assessment scope.
Five SAQ Mistakes That Create Expensive Rework
1. Choosing the shortest SAQ
Questionnaire length is a consequence of the eligible environment, not a menu of convenience. Reducing PCI scope through sound payment architecture can legitimately reduce assessment requirements. Selecting a narrow questionnaire without meeting its eligibility criteria cannot.
2. Treating outsourcing as complete scope elimination
Third-party payment processing can dramatically reduce merchant exposure, but website security, vendor management, applicable scanning, access controls, policies, and other responsibilities may remain.
3. Answering from policy instead of operational evidence
A requirement saying “we review access” should be supported by evidence that the review actually occurred. Compliance paperwork that describes a parallel universe where every process runs perfectly is not useful security evidence.
4. Discovering extra payment channels halfway through
The ecommerce team may use hosted checkout while the sales team takes card details by telephone and the finance team uses a virtual terminal. Those channels must be considered when determining the organization’s actual PCI environment.
5. Treating the SAQ as an annual paperwork event
A payment environment can change between assessments. New plugins, scripts, terminals, offices, cloud services, remote-access tools, processors, or workflows can change scope and control requirements. Build PCI considerations into change management rather than rediscovering the architecture at renewal time.
Review These Four Items Before Submitting Your SAQ
Use the following as an internal review sequence, alongside the current form and the accepting entity’s instructions. It is an editorial work aid, not an alternative attestation or an independent compliance approval.
- Scope and eligibility: the described organization, payment channels, systems and providers match the assessed environment. Unknown or unmet eligibility criteria have been resolved rather than hidden in assumptions.
- Answers and evidence: each response follows the actual form instructions. Evidence supports the relevant systems and period; required explanations, worksheets and technical testing are included where applicable.
- Attestation consistency: the SAQ and AOC describe the same scope and results. The appropriate signatory understands the statements being made, including any unresolved issue that affects the reported status.
- Submission and receipt: the correct document package is sent to the requested recipient through the approved channel. Keep the submission reference and any acceptance, rejection or follow-up request.
A successful upload is evidence that a file was transmitted, not necessarily that the accepting entity approved its contents. Track the actual response and assign any follow-up. Keep ongoing security work active while the submission is being reviewed.
A Practical Pre-SAQ Checklist
- Validation: Confirm whether the accepting entity permits an SAQ and what it expects you to submit.
- Current documents: Download the latest applicable SAQ from PCI SSC rather than recycling last year’s local copy.
- Payment channels: Inventory ecommerce, retail, telephone, mail-order, mobile, and virtual-terminal workflows.
- Data flow: Document where payment account data enters, travels, and is stored.
- Scope: Identify systems and people within or connected to the payment environment.
- Eligibility: Test every criterion for the candidate SAQ.
- Third parties: Obtain appropriate current evidence and document responsibility boundaries.
- Evidence: Collect records showing that applicable controls actually operate.
- Scanning: Determine whether ASV scanning or other technical validation applies.
- Remediation: Fix identified failures before making unsupported compliance statements.
- AOC: Complete the applicable Attestation of Compliance.
- Submission: Send the requested documents through the process specified by the accepting entity.
- Maintenance: Preserve evidence and monitor changes that could alter PCI scope before the next assessment.
When to Get Professional PCI DSS Help
A straightforward merchant using a well-understood, tightly scoped payment architecture may be able to complete an SAQ internally. Professional assistance becomes more valuable when the environment contains ambiguity rather than merely paperwork.
Consider qualified PCI support when:
- You cannot confidently identify the correct SAQ.
- Your website receives or can materially affect payment account data.
- You electronically store account data.
- You operate several different payment channels.
- You have multiple offices, cloud environments, networks, or payment applications.
- Network segmentation is being relied upon to reduce PCI scope.
- Required vulnerability scans repeatedly fail.
- Your payment architecture has changed substantially.
- Your acquirer requires independent validation or a Report on Compliance.
- Your team cannot produce evidence supporting important questionnaire responses.
If outside help is required, define whether you are buying scoping advice, remediation assistance, SAQ readiness work, ASV scanning, penetration testing, or formal assessment services. These are different jobs and should not disappear into one foggy “PCI compliance package.”
Copy a validation-path confirmation brief
Use this summary when confirming required documents with the entity accepting your compliance submission. Keep actual account identifiers and architecture details in an appropriate private channel. This brief is not an SAQ or an attestation.
Entity and payment channel(s) under review:
Merchant and any separate service-provider activities:
Payment provider / exact service and integration version:
Card-entry field origin / submission path / hosting owner:
Account-data handling by business systems, staff and logs:
Other channels, POS devices, virtual terminals or custom flows:
Current payment-flow and provider-evidence references:
Requested submission documents / form edition:
Eligibility conditions needing confirmation:
ASV scanning or other supporting evidence requested:
Recipient organization and authorized confirmation contact:
Written confirmation / date / reference:
Unresolved question / owner / next step:
Change that would require reassessing the decision:
Record confirmation as received, including its scope and conditions. If a proposed SAQ has an unmet or unknown eligibility criterion, keep the question open; do not turn an assumption into a checked answer.
PCI DSS SAQ FAQ
Do all businesses that accept credit cards complete the same SAQ?
No. PCI SSC provides multiple SAQs for different payment environments. Eligibility depends on the conditions stated in the individual questionnaire, and your compliance-accepting entity should confirm the validation method it expects.
Can I choose SAQ A because all card payments use a third-party processor?
Not automatically. Outsourcing payment processing is only part of the analysis. Your payment channel and integration must satisfy all current SAQ A eligibility criteria. Ecommerce implementations deserve particular attention because the merchant website can still affect payment security.
Does SAQ A require an ASV scan?
For current PCI DSS v4.x ecommerce SAQ A environments, PCI SSC has clarified that applicable external vulnerability scanning requirements cover merchant ecommerce webpages, including webpages that redirect transactions to a third-party service provider or contain the provider’s embedded iframe. Review the current SAQ and PCI SSC FAQ 1604 for your environment.
Is an SAQ the same as a PCI DSS certification?
No. An SAQ is an official PCI DSS self-assessment validation tool. PCI SSC warns that generic compliance certificates are not substitutes for the official validation forms recognized under PCI programs.
Do I need a QSA to complete an SAQ?
PCI SSC does not make hiring a Qualified Security Assessor a universal prerequisite for every SAQ. However, the organization accepting your PCI validation may impose particular assessment or validation requirements. A QSA or other qualified PCI professional can also be useful when scope or eligibility is genuinely difficult to determine.
Which SAQ does a service provider use?
PCI SSC states that SAQ D for Service Providers is the only SAQ available to SAQ-eligible service providers. Merchant SAQs such as A, A-EP, B, and C are not alternative service-provider questionnaires.
How often should I reconsider which SAQ applies?
Do not wait for the next assessment if the payment architecture changes. Re-evaluate scope and eligibility when you add or replace a gateway, checkout method, payment application, terminal type, service provider, network connection, ecommerce platform, or other component that could affect payment security.
The Best SAQ Is the One Your Environment Actually Qualifies For
PCI DSS self-assessment becomes much easier once the order of operations is correct. First understand the payment flow. Then define scope. Confirm the required validation route. Test the eligibility criteria. Only then start answering the questionnaire.
That sequence avoids the most expensive PCI mistake: spending days completing a form whose assumptions do not match the systems taking payments.
Your immediate next step is simple. Open the current PCI SSC Document Library, obtain the latest SAQ Instructions and Guidelines and candidate questionnaire, and compare its eligibility criteria with a one-page diagram of your real payment flow. Then confirm the validation route with the organization that accepts your PCI documentation.
Do that before buying another compliance tool. The questionnaire is downstream of the architecture, and the architecture is where the answer usually lives.
Official Sources and Editorial Review
- PCI SSC FAQ 1215: SAQ purpose, eligibility and service-provider restrictions.
- PCI SSC FAQ 1134: self-assessment workflow.
- PCI SSC FAQ 1473: tested applicability and excluded requirements.
- May 2026 SPoC/CPoC bulletin: sunset timing and existing listing lifecycle.
- PCI SSC document library: current SAQs and completion instructions.
Editorial review: November 16, 2026. Rechecked the linked primary guidance, added the SPoC/CPoC lifecycle note and expanded evidence, response and submission review. The exercises and working templates are editorial aids. No merchant account, payment system, signed attestation or submitted assessment was accessed or evaluated.