PCI DSS Ecommerce Security Software Pricing in 2026
Separate PCI portal, firewall, hosted-platform and payment-page monitoring costs. Compare dated USD list prices and use a quote worksheet that separates external cash from internal operating time.
Practical cybersecurity guides, labs & compliance
Separate PCI portal, firewall, hosted-platform and payment-page monitoring costs. Compare dated USD list prices and use a quote worksheet that separates external cash from internal operating time.
Compare five payment-page script monitoring products using vendor documentation, deployment questions, plan limits and a copyable proof-of-fit record for your checkout flow.
Plan ISO 27001 certification around readiness, audit bookings, findings and the certification decision. Use the illustrative schedule and copyable dependency record to separate proposed dates from confirmed commitments before promising a deadline.
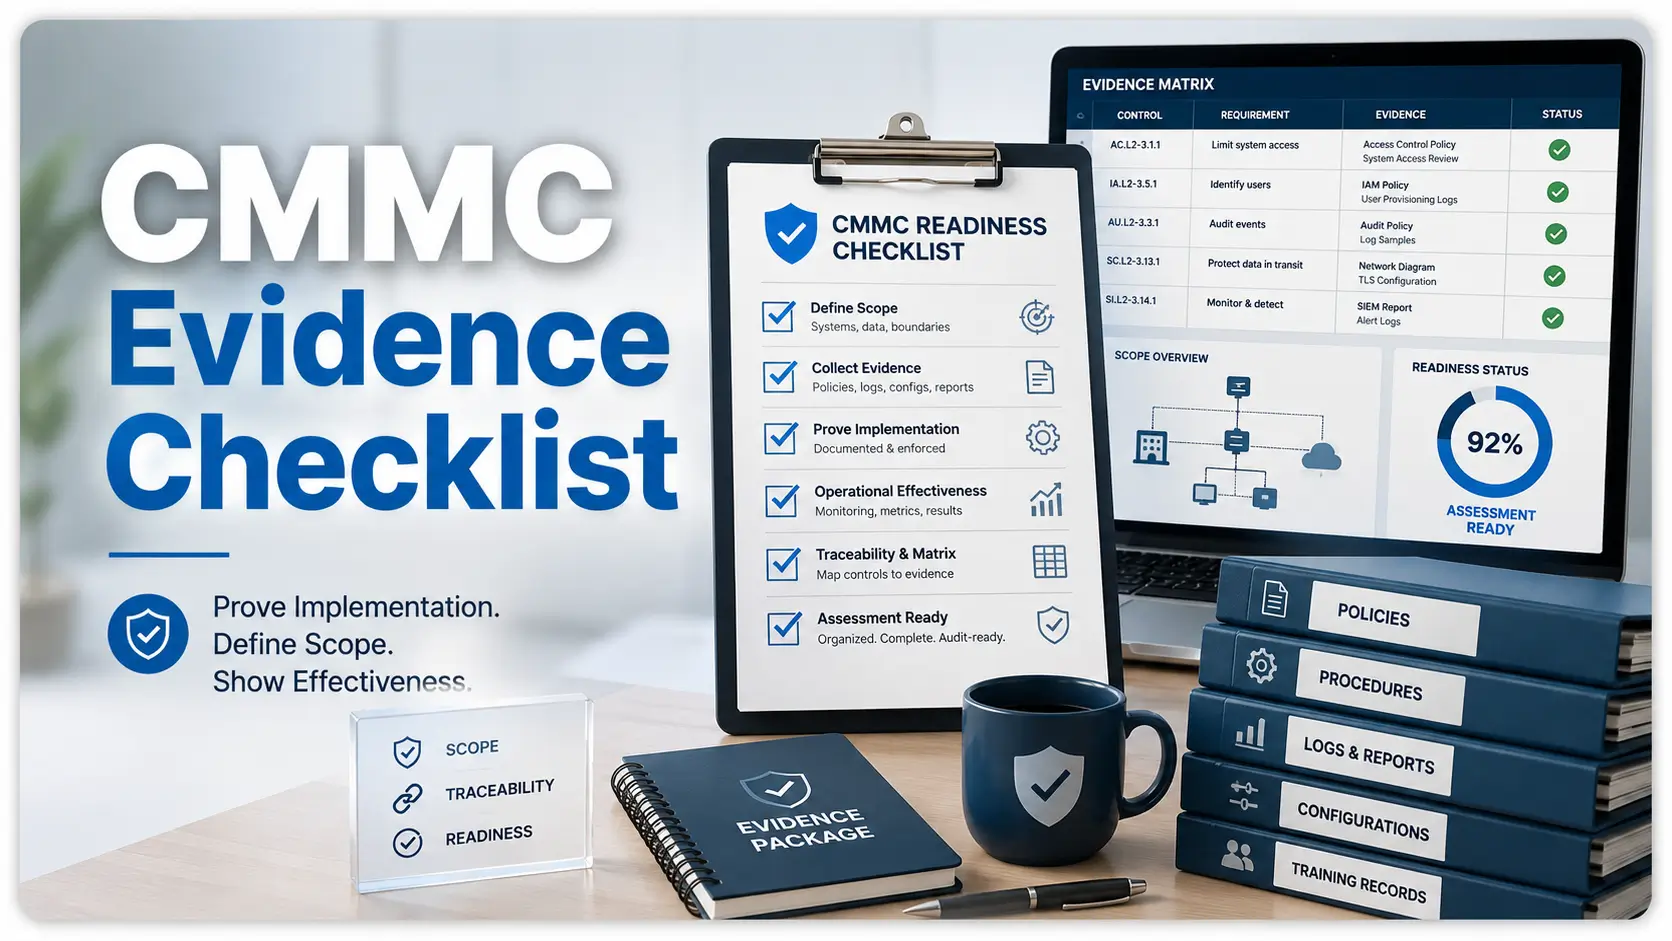
Keep CMMC assessment and annual affirmation dates separate. Review SPRS records, authority, scope changes and evidence with seven checks, practical examples and a copyable working record.
Understand payment-page change detection under PCI DSS 11.6.1, including browser-facing content, headers, alert routing and validation scope. Use the controlled drill record to separate planned changes, actual detections and untested coverage.
Review payment-page script authorization, integrity and business necessity where PCI DSS 6.4.3 applies. Distinguish embedded checkout from redirects under SAQ A, and use the copyable script record to connect decisions with evidence and owners.
Compare CMMC consulting, software and hybrid support for the same outcome and period. Separate external cash from staff capacity, test break-even assumptions, and use the copyable brief to record retained work, exclusions and unresolved scope.
Calculate first-year and three-year CMMC planning totals from your own USD inputs. Separate expected cash, reserves and internal labor, test the clearly hypothetical example, and keep scope, quote dates and unresolved assumptions with the result.
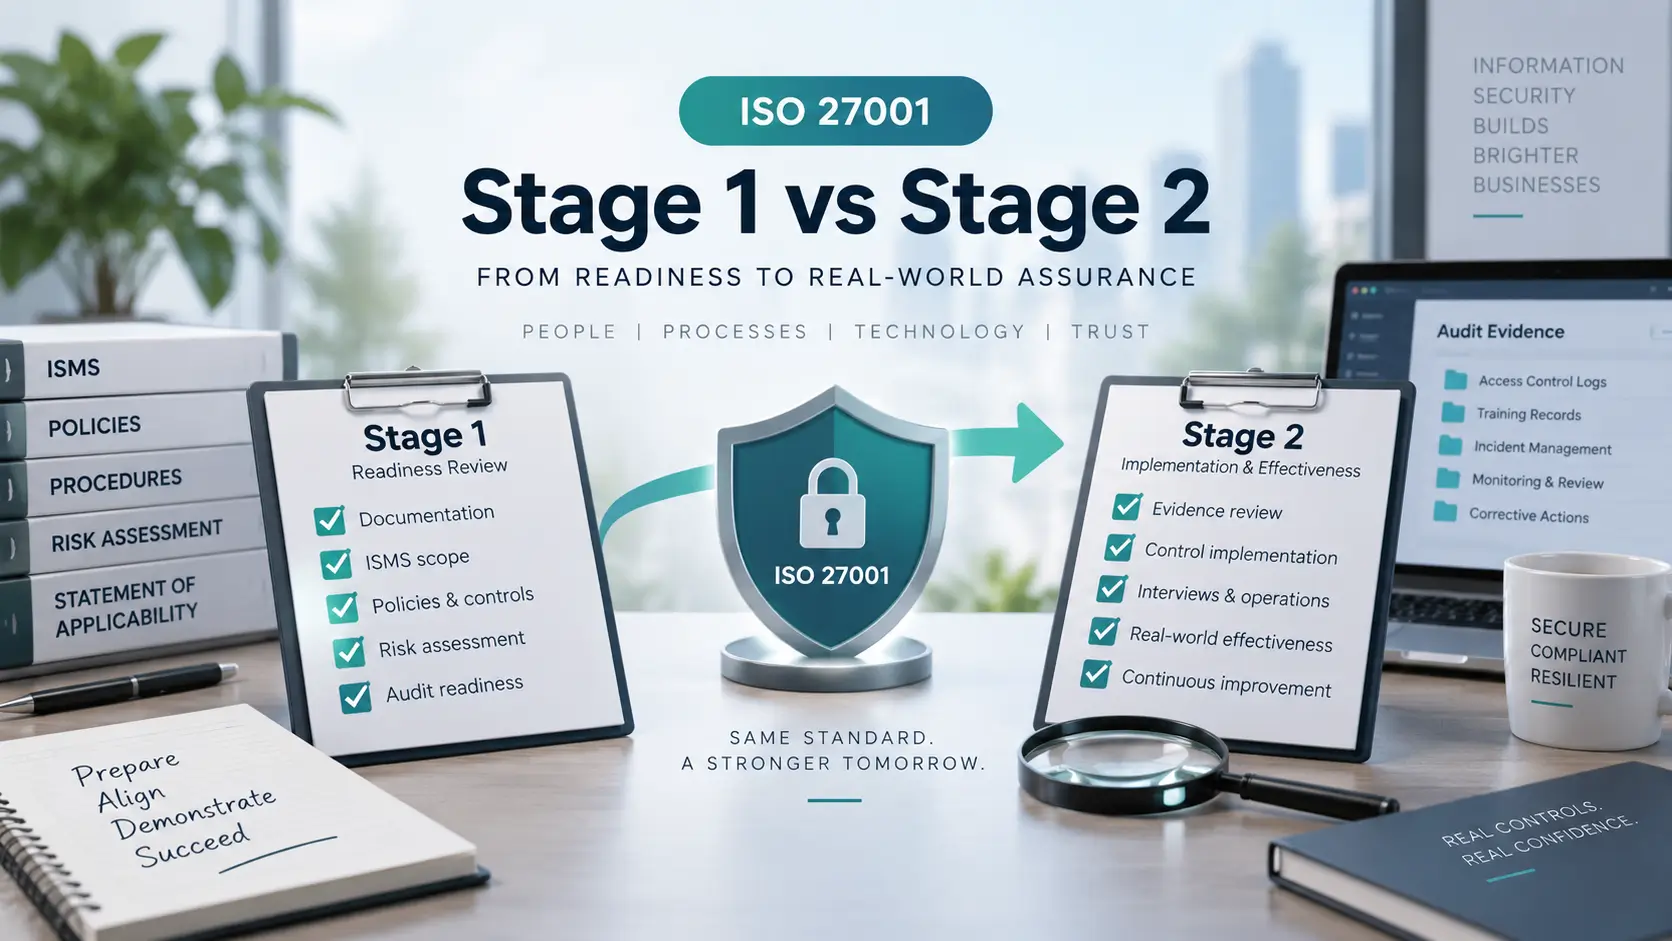
Compare ISO 27001 Stage 1 readiness work with Stage 2 implementation evidence. See what to prepare, how to plan the interval, and what you can accurately tell customers after each stage.
Map your ecommerce payment flow, confirm the validation route with your acquirer, and organize evidence for PCI DSS v4.0.1. Covers outsourced checkout, SAQ A script protection, scanning and shared responsibilities.