The most effective PCI DSS scope reduction strategy is to stop cardholder data from entering systems that do not genuinely need it. Network segmentation, tokenization, encryption, hosted payment pages, outsourcing, and point-to-point encryption can all help, but they work differently. Some remove systems from the card-data path. Others merely make data safer while the systems remain in scope.
Table of Contents
Copy the before-and-after scope-change record to document one proposed reduction and its remaining dependencies.
That distinction matters because a smaller PCI DSS scope can mean fewer systems to configure, patch, monitor, test, document, and assess. It can also reduce the amount of evidence teams must maintain year after year. As explained in this PCI DSS compliance cost guide for small businesses, the architecture of the payment flow often affects compliance workload more than company size alone.
PCI DSS v4.0.1 is the current version listed by the PCI Security Standards Council (PCI SSC), and the requirements that were originally future-dated became effective on 31 March 2025. Scope-reduction decisions therefore need to be evaluated against the current standard rather than an older SAQ checklist or a payment provider’s marketing shorthand. The PCI SSC Document Library should be the starting point when confirming the current standard and validation documents.
There is also an important limit to the entire idea of “reducing PCI scope”: scope reduction is not responsibility elimination. Outsourcing payment processing, using encryption, or qualifying for a shorter Self-Assessment Questionnaire can reduce the number of systems or requirements applicable to your environment, but it does not automatically eliminate your remaining PCI DSS obligations.
What PCI DSS Scope Reduction Actually Means
PCI DSS scope begins with the systems, people, and processes involved with payment account data and extends to systems that are connected to or can affect the security of the cardholder data environment, depending on the architecture.
The PCI SSC’s guidance on PCI DSS scoping and network segmentation recommends beginning with the assumption that everything is in scope until it has been verified otherwise. That is a useful discipline because beginning with the opposite assumption can create invisible dependencies: an administrator workstation, jump server, shared identity system, logging platform, development tool, or network pathway may affect the CDE even though it never intentionally stores a card number.
A good scope-reduction project therefore asks two different questions:
- Can this system be prevented from storing, processing, or transmitting payment account data?
- Can this system be prevented from connecting to, administering, or materially affecting systems that do?
The first question reduces the card-data footprint. The second prevents that footprint from quietly expanding again through connectivity and administrative dependencies.
Use the Eliminate, Outsource, Isolate, Prove Model
A practical way to think about PCI DSS scope reduction is a four-stage sequence:
- Eliminate: Remove cardholder data from systems and business processes that do not need it.
- Outsource: Move necessary payment-data handling to appropriately validated payment providers where doing so fits the business.
- Isolate: Separate the remaining cardholder data environment from systems that do not need to interact with it.
- Prove: Verify the architecture, segmentation, service-provider responsibilities, and data flows instead of assuming they work as designed.
This order matters. Trying to segment a sprawling environment containing unnecessary card numbers is usually harder than removing the unnecessary data first.
1. Stop Collecting Card Data Where You Do Not Need It
The cleanest PCI DSS scope reduction is not a firewall rule. It is the absence of cardholder data.
Trace every payment channel and ask where the primary account number (PAN) can appear. Do not limit the exercise to the checkout database. Card information can leak into systems that were never designed to become payment systems, including:
- application and web-server logs;
- customer-support tickets;
- email inboxes;
- CRM notes;
- analytics systems;
- call recordings;
- debugging tools;
- error-monitoring platforms;
- spreadsheets and exports;
- data warehouses;
- backups and snapshots;
- developer test environments.
If a business function only needs a transaction identifier, payment status, last four digits, token, or processor-generated customer reference, redesign the workflow so the full PAN never enters the application.
This can be dramatically more effective than building controls around unnecessary data. Every new copy of payment data potentially creates another storage location, access path, retention rule, backup copy, deletion process, and assessment question.
2. Move Payment Entry to a Properly Outsourced Checkout
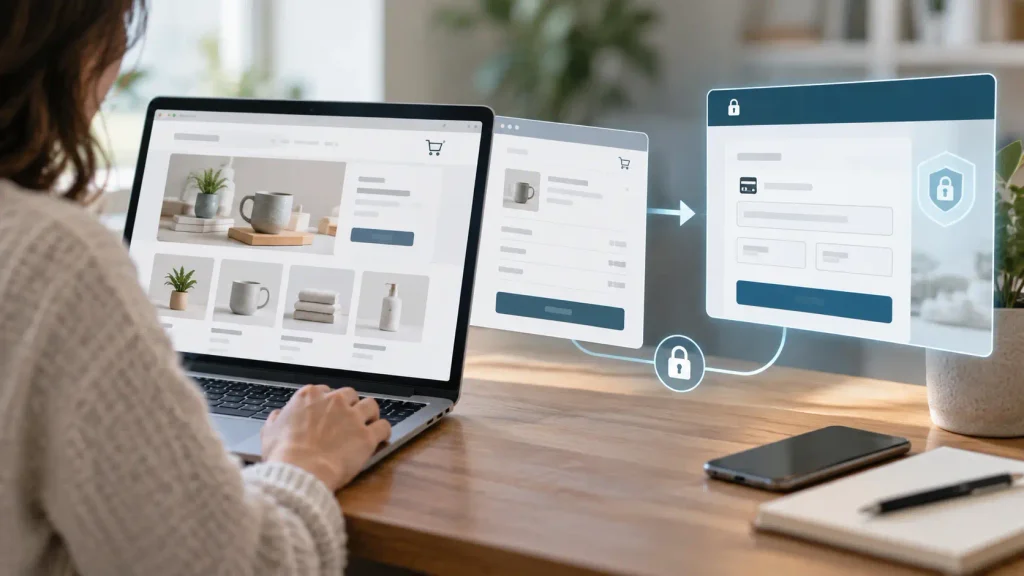
For many e-commerce merchants, changing where customers enter card details can produce one of the largest practical reductions in PCI DSS scope.
A hosted payment page or appropriately implemented payment-provider iframe can keep payment account data away from merchant-controlled applications. The PCI SSC explains that merchants eligible for SAQ A generally outsource payment processing and do not electronically store, process, or transmit account data on merchant systems or premises. Eligibility still depends on meeting every applicable criterion for that SAQ.
In particular, the PCI SSC states that for SAQ A eligibility, payment-page elements involved in payment-data capture must originate appropriately from PCI DSS-compliant third-party service providers. A direct-post architecture is different because the merchant website creates some or all of the page used to accept payment data, which can lead to a materially different validation path.
The official PCI SSC guidance on SAQ A and SAQ A-EP payment-page eligibility is worth reviewing before changing an integration solely to obtain a shorter questionnaire.
This distinction also explains why PCI costs can diverge sharply between apparently similar online stores. The PCI DSS compliance cost guide for ecommerce stores looks at how hosted checkout, custom payment flows, scanning, remediation, and assessment requirements can change the annual workload.
Outsourcing does not mean zero merchant responsibility
The PCI SSC explicitly states that outsourcing all payment processing does not remove the merchant’s responsibility for PCI DSS. Depending on the arrangement, merchants still need to confirm the provider’s appropriate PCI DSS status, understand shared responsibilities, maintain required agreements, monitor relevant providers, and complete the validation required by their acquirer or payment brand.
See the PCI SSC’s guidance on merchants that outsource all payment processing before treating a processor’s compliance status as proof that the merchant has nothing left to do.
3. Remove Stored PAN and Use Tokens Where Possible
If recurring billing, refunds, subscriptions, or customer account features appear to require stored card details, ask whether the business actually needs the PAN or only needs the ability to reference a payment credential held by the processor.
Tokenization can replace the PAN with a surrogate value that applications use for later operations. Properly designed tokenization can reduce the number of systems containing cardholder data and therefore potentially reduce PCI DSS scope.
But tokenization contains a trap: the tokenization system itself does not magically become out of scope. Systems that generate tokens from PANs, convert tokens back into PANs, store the underlying PAN, or have relevant access to those functions remain important parts of the PCI environment.
The safest architecture for many merchants is therefore not to build their own token vault at all. A processor or specialized payment provider can hold the payment credential and return a token or customer reference that the merchant application can use without receiving the underlying card number.
After migrating, perform a historical cleanup. Search databases, logs, exports, object storage, queues, backups, support platforms, and development environments for copies left behind by the previous design. Changing checkout today does not automatically erase yesterday’s cardholder data.
4. Do Not Confuse Encryption With Scope Elimination
Encryption protects cardholder data. That makes it extremely important, but encryption by itself does not automatically remove encrypted cardholder data from PCI DSS scope.
The PCI SSC’s March 2026 clarification on encrypted cardholder data and PCI DSS scope states that strong cryptography is an accepted way to render stored cardholder data unreadable, but encryption alone is insufficient to render that data out of scope.
This is logical when the same organization controls both the encrypted data and the ability to decrypt it. The storage server may see ciphertext, but the surrounding environment still contains the keys, applications, identities, or processes capable of turning that ciphertext back into payment data.
Scope reduction therefore requires looking at the complete trust path, not simply checking whether the database column resembles random characters.
Masking is not the same as removing stored PAN
Masking also should not be mistaken for scope reduction. Masking controls what a person sees on a screen or report. A system can display only the last four digits while still retaining the complete PAN underneath.
Truncation is different because digits are actually removed from the stored value. PCI SSC’s guidance on masking versus truncation explains why these terms should not be used interchangeably.
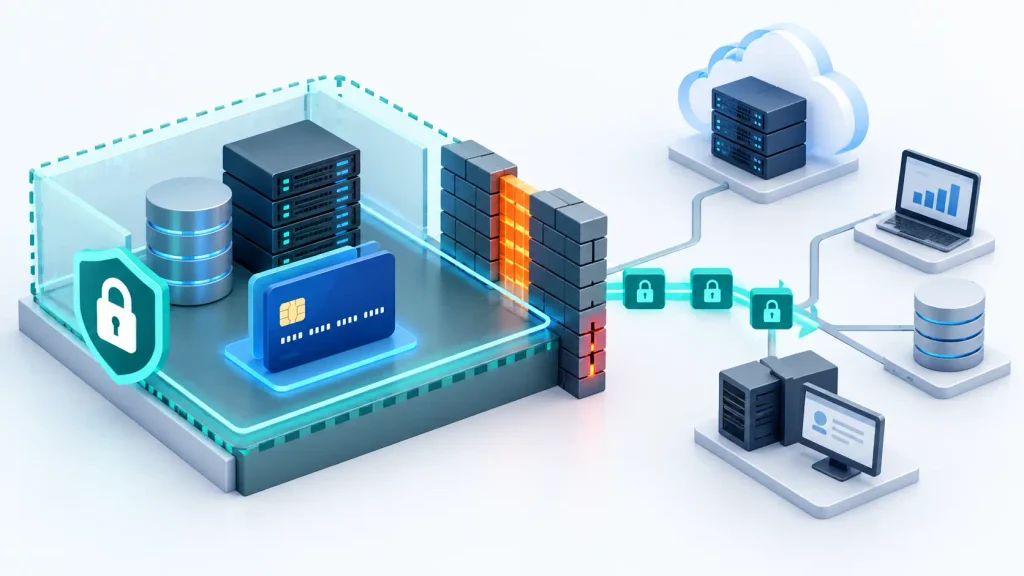
5. Segment the CDE Instead of Letting It Share the Whole Network
Once unnecessary payment data has been removed, network segmentation can help contain what remains.
The objective is not merely to put payment servers in a VLAN named “PCI.” The objective is to enforce separation so that compromise of an out-of-scope system cannot simply become a path into the cardholder data environment.
Depending on the architecture, effective segmentation may involve firewalls, access-control rules, cloud security controls, routing boundaries, identity restrictions, hardened administrative paths, separate management networks, and tightly controlled interfaces between environments.
Pay particular attention to systems that are often accidentally shared:
- Active Directory or other identity infrastructure;
- remote-access platforms;
- administrator workstations;
- bastion or jump hosts;
- configuration-management systems;
- endpoint-management tools;
- CI/CD infrastructure;
- monitoring and logging platforms;
- backup infrastructure;
- DNS and network-management systems;
- cloud administrative accounts.
A system does not need to contain a card number to matter. If compromise of that system gives an attacker administrative control over the CDE, its relationship with PCI scope needs careful evaluation.
Test the boundary rather than trusting the diagram
A network diagram is a statement of intent. Testing determines whether the separation actually exists.
Organizations using segmentation for PCI scope reduction should therefore make sure the boundary is included in the testing and validation activities applicable to their environment. When external specialists are required, define exactly which networks, applications, roles, and segmentation controls need to be examined. The small-business penetration testing cost guide explains why the number of targets and the requested testing depth can substantially change an engagement.
6. Consider PCI-Listed P2PE for Card-Present Payments
For card-present environments, PCI-listed point-to-point encryption can be another powerful scope-reduction tool.
A validated P2PE solution protects account data from the point of interaction through the validated decryption environment. According to the PCI SSC, using a PCI-listed P2PE solution can significantly reduce the number of PCI DSS requirements applicable to a merchant’s cardholder data environment.
The word listed matters. Generic statements such as “our terminal encrypts card data” are not automatically equivalent to using a PCI-listed P2PE solution. Encryption can improve security without producing the same PCI DSS validation effect.
P2PE also does not eliminate PCI DSS entirely. Merchants still need to implement and operate the solution according to its requirements, maintain applicable device and process controls, and address other payment channels that are not protected by the P2PE solution.
If a business accepts payment through both validated P2PE terminals and a separate e-commerce platform, for example, the online channel does not disappear merely because the physical terminals have a reduced validation scope.
7. Reduce Third-Party Scope Without Creating a Vendor Blind Spot
Third parties can reduce the amount of payment infrastructure a merchant operates directly, but every outsourced function introduces a responsibility boundary that needs to be understood.
For each relevant provider, record:
- what service it provides;
- whether it stores, processes, or transmits account data;
- whether it can affect the security of the CDE;
- which PCI DSS responsibilities it performs;
- which responsibilities remain with your organization;
- what PCI DSS evidence or Attestation of Compliance applies to the services you actually use;
- when that evidence was last reviewed;
- how incidents and material changes must be communicated.
PCI SSC’s guidance on third-party service providers stresses that customers must manage TPSP relationships and understand which requirements are performed by which party.
Do not stop at a checkbox asking whether a vendor is “PCI compliant.” The important question is whether its validated services correspond to the services, locations, components, and responsibilities on which your own compliance depends.
A structured review process helps here. The vendor security questionnaire template provides a broader framework for examining security ownership, vulnerability management, access, cloud configuration, and evidence rather than accepting a badge or one-line assurance.
8. Treat Scope as a Living Architecture, Not an Annual Questionnaire
A beautifully reduced PCI scope can expand again with one ordinary engineering change.
Examples include:
- adding a new payment-page script;
- changing from redirect checkout to a merchant-hosted payment form;
- adding a call-center payment process;
- sending card details into a CRM;
- creating a data warehouse export containing PAN;
- connecting a corporate management platform to CDE servers;
- moving workloads into a shared cloud account;
- allowing developers broader production access;
- changing payment processors;
- adding a new third-party integration.
PCI scoping should therefore be part of architecture and change management, not an archaeological expedition conducted once a year before the assessment.
Create a small set of payment-security change triggers. Any project that changes card-data collection, storage, payment-page behavior, network connectivity, privileged access, or relevant third parties should prompt a scope review before release.
Vulnerability management should receive the same treatment. A tightly scoped environment is valuable only if the systems that remain in it are maintained effectively. The vulnerability remediation SLA guide explains how organizations can define ownership and remediation windows instead of allowing findings to age indefinitely.
The 2026 SAQ A Trap: Hosted Checkout Still Leaves Website Work
One of the most important current scoping lessons concerns e-commerce merchants using SAQ A.
It is tempting to think that redirecting customers to a payment processor or embedding a processor’s iframe turns the merchant website into an irrelevant bystander. Current PCI guidance does not support that conclusion.
For e-commerce merchants using an embedded payment page or form, PCI SSC clarified in 2025 that SAQ A eligibility includes confirming that the merchant site is not susceptible to script attacks that could affect the e-commerce system. The Council describes approaches associated with PCI DSS Requirements 6.4.3 and 11.6.1, or obtaining the relevant confirmation from a compliant provider where the provider’s solution satisfies the applicable eligibility approach.
See the PCI SSC’s SAQ A script-security clarification for the distinction between embedded payment forms and redirect scenarios.
There was another important clarification in June 2026. PCI SSC FAQ 1604 confirms that SAQ A under PCI DSS v4.x includes applicable external vulnerability scanning by an Approved Scanning Vendor for merchant e-commerce webpages, including webpages that redirect transactions to a third-party service provider or contain a provider’s embedded iframe.
The current PCI SSC FAQ on ASV scanning for SAQ A merchants is therefore essential reading for teams working from older assumptions about outsourced checkout.
The practical lesson is simple: reducing where the card number travels does not necessarily make the security of the page leading customers into that payment flow irrelevant.
What Usually Does Not Reduce PCI DSS Scope by Itself
Several controls are important for security but should not be sold internally as automatic scope-removal mechanisms.
| Approach | Why it may not remove scope by itself |
|---|---|
| Encrypting stored PAN | Encryption protects stored data, but PCI SSC states that encryption alone does not make encrypted cardholder data out of scope. |
| Masking PAN on screens | The complete PAN may still exist underneath the masked display. |
| Creating a PCI VLAN | A network label is not effective segmentation if other systems can still reach or control the CDE. |
| Using a PCI-compliant processor | The merchant retains applicable responsibilities and must evaluate its own payment integration. |
| Tokenizing PAN internally | The tokenization, de-tokenization, PAN storage, and related access paths can remain in scope. |
| Using ordinary encryption at a payment terminal | Encryption is not automatically equivalent to a PCI-listed P2PE solution. |
These technologies can still be excellent controls. The mistake is assuming that a security control and a scope-reduction mechanism are automatically the same thing.
A Practical PCI DSS Scope-Reduction Review
Before buying another compliance platform or commissioning a large assessment, draw the payment architecture on one page.
- List every channel through which your organization accepts cards.
- Mark exactly where customers enter payment account data.
- Trace where that data is transmitted immediately afterward.
- Identify every location where full PAN could be stored, including logs and backups.
- Mark all systems with administrative or security influence over the CDE.
- Identify each payment processor and relevant service provider.
- Record where tokens replace PAN and who can reverse those tokens.
- Draw the segmentation boundary around the systems that remain.
- List every allowed connection crossing that boundary.
- Verify that the technical architecture matches the diagram.
Then ask four harder questions:
- Can we eliminate this copy of cardholder data?
- Can we outsource this payment-data function without creating an unacceptable business dependency?
- Can we isolate this supporting system so it no longer has unnecessary access to the CDE?
- What evidence demonstrates that the proposed scope reduction is real?
This exercise also makes budgeting more reliable. PCI projects become expensive when teams buy tools, consultants, scans, and tests before determining what actually belongs in the environment they are trying to validate.
Copy a before-and-after scope-change record
Use one record for a specific change, such as replacing merchant-hosted card entry or separating an administrative path. A design proposal and a verified scope conclusion are different stages. This is a planning record, not a determination that an asset is out of scope.
Change ID / date / owner / payment channel:
Before: data entry, destinations and retained copies:
Before: connected and security-impacting systems:
Proposed change and expected scope effect:
After: actual data flow / architecture reference:
Legacy data locations / cleanup evidence / unresolved retention:
Remaining keys, retrieval capability and privileged access:
Identity, deployment, logging and other shared dependencies:
Boundary controls / authorized validation scope:
Test or review evidence / date / actual result / limits:
Remaining in-scope systems and responsibilities:
Assets proposed for exclusion / rationale / pending questions:
Assessor or compliance-accepting entity confirmation:
Validation-document changes confirmed / reference:
Rollback impact / future changes requiring reassessment:
If you estimate savings, keep expected workload reduction separate from observed results. Record scope changes only after reviewing remaining data, access and security dependencies; do not remove an asset solely because PAN is absent from its primary database.
Choose Architecture Before Choosing the SAQ
A Self-Assessment Questionnaire should describe an eligible payment environment. It should not be used as an architectural wish list.
Do not start with, “We want SAQ A, so how do we answer these questions?” Start with, “How does payment data actually move, what systems can affect it, and which SAQ eligibility criteria does that architecture satisfy?”
The PCI SSC emphasizes that each SAQ has eligibility criteria tied to a particular type of payment environment. Meeting some of the criteria is not enough. Merchants should also confirm their required validation path with the acquirer, payment brand, processor, or other entity accepting their PCI DSS validation.
For organizations with custom payment applications, multiple payment channels, stored PAN, complicated segmentation, or uncertainty around shared administrative systems, professional scoping assistance may cost less than redesigning the wrong environment after an assessment has already begun.
The Best Scope Reduction Removes Risk Before It Removes Paperwork
PCI DSS scope reduction works best when the compliance benefit is a consequence of a simpler and safer payment architecture.
Remove unnecessary cardholder data first. Use a properly designed outsourced payment flow where it fits the business. Replace stored PAN with provider-managed tokens when possible. Segment what remains. Consider PCI-listed P2PE for suitable card-present environments. Control privileged access and third-party pathways. Finally, verify the result rather than trusting the architecture diagram.
The objective is not to make the questionnaire shorter at any cost. It is to create fewer places where cardholder data can exist, fewer systems capable of reaching it, and fewer pathways an attacker could use to compromise it.
When that architecture is done well, the compliance workload often becomes smaller too. That is the useful kind of scope reduction: less payment data, fewer risky dependencies, and a CDE small enough that the organization can actually understand and defend it.
Scope-review aid and evidence links reviewed: 2026-10-23. Added a before-and-after change record and checked PCI SSC FAQs 1086 and 1293. No environment was tested or approved for scope exclusion.