SAQ A and SAQ A-EP can look frustratingly similar: both are PCI DSS Self-Assessment Questionnaires, both can apply to ecommerce merchants using third-party payment providers, and neither is designed for a merchant that electronically stores, processes, or transmits account data on its own systems.
Table of Contents
The difference depends on the payment-data capture architecture and the complete SAQ eligibility criteria. SAQ A generally fits more fully outsourced card-not-present payment environments. SAQ A-EP is designed for ecommerce environments where payment processing is outsourced, but the merchant’s website can materially affect the security of the payment transaction.
That architectural distinction matters. Choosing the shorter questionnaire because it looks easier does not make your environment eligible for it. PCI SSC states that merchants should satisfy all eligibility criteria for the applicable SAQ and confirm the expected validation method with the organization accepting their PCI compliance evidence, typically an acquiring bank, payment brand, processor, or payment facilitator.
If you are budgeting for the wider assessment process as well as choosing a questionnaire, the related guide to PCI DSS SAQ versus ROC assessment costs explains why validation method and payment architecture can change the workload so dramatically.
7 Essential Checkout Checks Before Choosing an SAQ
Use these seven checks to prepare a discussion with your developer and compliance contact. This is an editorial evidence checklist, not the complete SAQ eligibility criteria. Record an implementation reference and an owner for each answer; a product name or screenshot of a payment button cannot establish the underlying data flow.
| Check | Question to answer | Useful evidence |
|---|---|---|
| 1. Integration identity | Which product, plugin, SDK and version serve each checkout route? | Deployment record and exact provider integration guide. |
| 2. Field origin | Who supplies the account-data entry fields? | Developer explanation tied to the implemented redirect, embedded component or merchant form. |
| 3. Submission path | Which systems receive payment details before tokenization? | Data-flow description and approved test-environment observations. |
| 4. Other collection paths | Do support tools, logs, phone orders or legacy pages collect account data? | Channel inventory and review of collection and logging configuration. |
| 5. Provider responsibility | Does the provider evidence cover the specific service used? | Applicable AOC and documented allocation of responsibilities. |
| 6. Website obligations | What addresses embedded-form script eligibility and the separate scan requirement? | Implementation-specific protection evidence and applicable ASV scope/results. |
| 7. Reporting acceptance | Who will accept the assessment, and what do they require? | Written confirmation of the form, reporting period, assessor requirements and due date. |
Read “unknown” as a task. If nobody can explain the field origin or submission path, assign that question to the integration owner before selecting a form. If the explanation disagrees with deployed custom code, resolve the mismatch rather than assuming the standard plugin documentation describes your implementation.
Review every relevant route, including checkout variants, failed-payment recovery, saved-card updates and old payment pages retained after a migration. A correct explanation of one route does not establish the architecture of the others. The related payment-provider migration checklist helps track deliberately retained paths.
SAQ A vs SAQ A-EP at a Glance
| Question | SAQ A | SAQ A-EP |
|---|---|---|
| Main use case | Card-not-present merchant with account-data functions fully outsourced | Ecommerce merchant with outsourced payment processing but a website that can affect payment security |
| Ecommerce only? | No. It can also apply to eligible mail-order/telephone-order environments | Yes |
| Can merchant systems electronically store, process, or transmit account data? | No, under the SAQ eligibility model | No, under the SAQ eligibility model |
| Who provides payment-page elements? | For the relevant ecommerce model, payment-page elements that accept account data originate from compliant third-party provider(s) | Payment-page elements may originate from the merchant website or compliant third-party provider(s) |
| Typical ecommerce example | Hosted redirect or appropriately implemented third-party embedded payment form | Direct Post or another merchant-controlled payment page that sends account data directly from the browser to the processor |
| Merchant website security scope | Reduced, but definitely not zero | Materially broader because the website can affect transaction security |
| Relative assessment burden | Generally narrower | Generally broader |
This table is a starting point, not an eligibility determination. PCI SSC maintains separate SAQs because different payment architectures create different security risks. Its PCI DSS resources and SAQ documentation should be used alongside instructions from the entity that accepts your compliance validation.
What SAQ A Is Designed For
SAQ A is designed for eligible card-not-present merchants that outsource account-data functions to PCI DSS compliant third-party service providers and do not electronically store, process, or transmit account data on their own systems or premises.
For ecommerce, the important idea is that the component collecting the customer’s payment account data comes from the compliant payment provider rather than being created by the merchant’s own website.
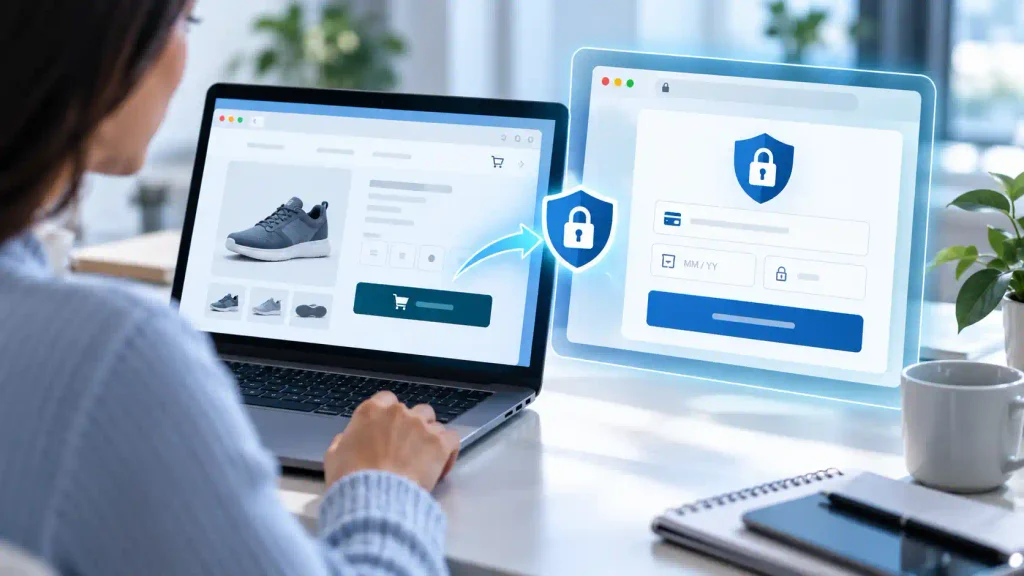
A familiar example is a hosted checkout redirect. A shopper clicks the payment button on your store and is sent to a payment page operated by the payment processor. The customer enters payment details there rather than into a card-data form generated by your ecommerce application.
An embedded payment form or iframe can also potentially fit SAQ A when the implementation satisfies the current eligibility criteria. The visual distinction can be deceptive: the customer may appear to remain on your website even though the actual payment fields originate from the third-party payment provider.
PCI SSC’s guidance comparing SAQ A and SAQ A-EP payment-page elements explains the fundamental distinction. SAQ A requires the relevant payment-page elements to originate from PCI DSS compliant service providers, while SAQ A-EP permits payment-page elements to originate from either the merchant or compliant service providers, assuming all other eligibility conditions are also met.
What SAQ A-EP Is Designed For
SAQ A-EP exists for a narrower but more technically involved ecommerce situation. The merchant still outsources payment processing and does not electronically store, process, or transmit account data on merchant systems, but the merchant website has enough control over the payment experience to affect the security of the transaction.
The classic example is Direct Post.
Imagine that your own website generates the checkout page and the form containing the card-number field. When the shopper submits the form, the browser sends the account data directly to the payment processor rather than sending it through your web server.
Your server might never receive the card number. That sounds very similar to SAQ A until you ask a more important question: Who controlled the page into which the customer typed the card information?
If your website generated or controlled relevant elements of that payment page, compromise of your website could potentially alter the form, change its destination, insert malicious code, or otherwise interfere with the payment transaction. That creates the broader security exposure addressed by SAQ A-EP.
PCI SSC’s Direct Post versus iframe and redirect guidance describes this architectural distinction and why the two implementation styles lead to different SAQ paths.
The Simplest Way to Understand the Difference
Do not begin with the question, “Does my server receive the card number?” Both SAQ A and SAQ A-EP can involve environments where the merchant’s systems do not electronically receive account data.
Instead, ask:
- Who generates the fields into which the shopper enters payment information?
- Can code controlled by the merchant alter those fields?
- Does the merchant’s website construct part of the payment page?
- Does payment information go directly from a provider-controlled field to the processor, or from a merchant-generated form?
- Which systems could change where the browser sends payment data?
If the payment-data capture mechanism is genuinely supplied by the compliant payment provider and all SAQ A conditions are satisfied, SAQ A may be the appropriate route. If your ecommerce website constructs or controls payment-page components that can affect account-data capture while the browser sends the data directly to the processor, SAQ A-EP may be the more likely direction.
The word may matters. A merchant page can affect the payment journey even in a redirect or iframe setup, so that capability alone does not classify the checkout as A-EP. Review field origins, data flows and every eligibility condition; your compliance-accepting entity needs to accept the validation path.
Redirect Checkout: Usually the Clearest SAQ A Example
A redirect creates one of the easiest architectures to visualize.
- The customer shops on merchant.example.
- The customer clicks a payment or checkout button.
- The browser is redirected to the payment provider.
- The payment provider presents the payment-data entry page.
- The provider handles the account data.
- The customer is returned to the merchant after payment.
The merchant site still matters to security. An attacker who compromises it could potentially tamper with redirects, impersonate the checkout flow, or manipulate customer navigation. But the merchant is not building the form that actually accepts the account data.
That distinction helps explain why redirect-based architectures can often support SAQ A eligibility when all other criteria are met.
Iframe Checkout Can Also Be SAQ A, but Inspect the Implementation
An iframe checkout often confuses merchants because the payment fields appear inside the merchant’s page.
The relevant question is not what the checkout looks like. It is where the payment-data entry elements originate and who controls them.
Suppose your store page contains ordinary merchant-controlled content such as product information, shipping choices, headings, and order summaries, while a compliant payment provider supplies the embedded component containing the card-entry fields. That structure can potentially fall within SAQ A if it meets the full current eligibility criteria.
Do not assume every embedded widget works this way. Payment integrations that look nearly identical on screen can behave very differently underneath. Inspect the provider’s technical documentation, implementation method, and PCI guidance rather than classifying the integration from its appearance.
Direct Post Points Toward SAQ A-EP
Direct Post illustrates why “we never store card numbers” is not enough to select SAQ A.
In a Direct Post arrangement, your website can generate the form used to collect account data, but the customer’s browser submits that data directly to the processor. The merchant’s backend may therefore avoid receiving the card information while the merchant-controlled webpage still sits directly in the security path.
If malicious code compromises that page, the attacker may be able to alter how payment information is collected or where it is sent. The merchant environment therefore requires controls beyond those expected of the more fully outsourced SAQ A architecture.
This is the territory SAQ A-EP was created to address.
The 2025 SAQ A Revision: What Changed and What Did Not
PCI SSC’s official explanation of the SAQ A revision confirms that Requirements 6.4.3, 11.6.1 and 12.3.1 were removed from SAQ A and a script-attack eligibility condition was added. Those requirements were not removed from PCI DSS itself. Use the current questionnaire rather than a saved copy or an old requirement count.
For embedded forms, FAQ 1588 describes either deploying appropriate protective techniques or obtaining confirmation from the compliant provider that the embedded solution includes protections when implemented as instructed. The specific criterion does not apply to full redirects or fully outsourced payment-link flows. Other eligibility criteria and applicable requirements remain.
Keep three answers separate: whether the architecture fits SAQ A, how an embedded implementation addresses script eligibility, and which external scans apply. A provider’s general compliance statement does not by itself answer all three. Nor does an exception for redirects under one criterion establish an exception from scanning.
SAQ A Does Not Mean “No Website Security Requirements”
This is one of the most important misconceptions to remove.
Outsourcing payment processing can sharply reduce PCI scope, but it does not turn the merchant website into an irrelevant spectator.
PCI SSC revised SAQ A under PCI DSS v4.0.1. For certain ecommerce merchants using an embedded third-party payment page or form, current eligibility includes confirming that the merchant site is not susceptible to script attacks that could affect the ecommerce system. PCI SSC’s SAQ A script-security FAQ explains ways this eligibility condition can be addressed and clarifies that it specifically concerns embedded payment-page or payment-form implementations.
Redirect-only implementations are treated differently for that particular script eligibility criterion, but that does not eliminate other applicable SAQ A requirements.
SAQ A Merchants May Still Need ASV Scanning
Another dangerous shortcut is assuming that an outsourced payment page eliminates external vulnerability scanning.
PCI SSC clarified in June 2026 that applicable SAQ A ecommerce webpages are subject to external vulnerability scanning requirements under PCI DSS Requirement 11.3.2, including merchant webpages that redirect transactions to third-party service providers and webpages containing third-party embedded iframes.
The required PCI scan must be performed using an Approved Scanning Vendor where the SAQ requirement applies. The Council explains the scope in its 2026 SAQ A ASV scanning FAQ.
That clarification is especially useful if your organization based its PCI process on older assumptions. A merchant that chose its compliance workflow several years ago should not automatically reuse the old checklist without reviewing the current PCI DSS v4.0.1 questionnaire.
For a broader look at how scanning, staff time, remediation, and assessment effort affect smaller organizations, see the Kioptrix guide to PCI DSS compliance costs for small businesses.
Why SAQ A-EP Is Broader
The difference between A and A-EP is not simply questionnaire length. SAQ A-EP carries a broader set of security obligations because the merchant website has a stronger ability to influence the payment transaction.
Depending on the current questionnaire and your environment, that broader responsibility can reach areas such as secure configurations, malware protection, vulnerability management, application security, access control, authentication, logging, payment-page protections, security policies, and incident-related responsibilities.
This is why moving from a provider-hosted checkout toward a custom merchant-controlled checkout can create a larger compliance project even if card numbers never touch the merchant’s database.
If you are estimating the commercial impact of that architectural choice, the guide to PCI DSS compliance costs for ecommerce stores examines how hosted checkout, merchant-controlled payment flows, scanning, testing, and remediation affect total compliance effort.
A Practical SAQ A vs SAQ A-EP Decision Walkthrough
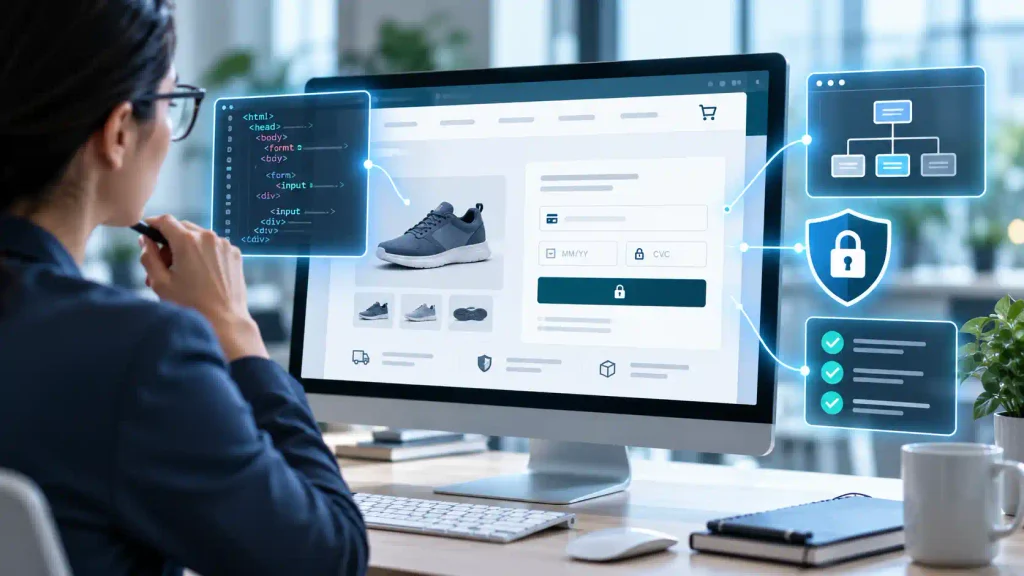
Use the following sequence as a scoping exercise before completing either questionnaire.
Step 1: Confirm that you are a merchant, not a service provider
SAQ A and SAQ A-EP are merchant questionnaires. Service providers should not use merchant SAQ eligibility criteria as a shortcut for determining their PCI DSS assessment requirements.
Step 2: Map where customers enter account data
Do not begin with vendor names. “We use Provider X” does not describe a payment architecture because the same provider may offer redirects, hosted fields, embedded forms, APIs, Direct Post integrations, and other checkout methods.
Draw the browser, merchant website, payment form, processor, and any intermediate services. Then mark the component that generates the account-data entry fields.
Step 3: Determine whether merchant systems receive account data
If merchant systems electronically store, process, or transmit account data, the environment may not qualify for either SAQ A or SAQ A-EP. Investigate a broader SAQ or assessment path rather than trying to squeeze the environment into one of these forms.
Step 4: Identify who creates the payment-data fields
If the PCI DSS compliant payment provider creates the payment-data entry mechanism and the full SAQ A eligibility criteria are met, SAQ A may fit.
If the merchant website creates relevant payment-page elements and the browser sends account data directly to the processor without merchant systems receiving it, investigate SAQ A-EP.
Step 5: Inventory scripts and services that can affect checkout
Modern ecommerce sites can load analytics, consent platforms, tag managers, live chat, advertising pixels, A/B testing libraries, fraud tools, customer-support widgets, and other third-party JavaScript.
Do not decide that something is irrelevant merely because it never intentionally receives a card number. Ask whether compromise of that component could affect the payment experience, alter browser behavior, redirect a customer, or change payment-page content.
Step 6: Check your provider’s AOC and service scope
Using a company that has passed a PCI DSS assessment is not enough by itself. Confirm that its Attestation of Compliance covers the service you actually use and understand which PCI responsibilities remain with you.
Step 7: Ask the compliance-accepting entity to confirm the validation path
This final step keeps an architectural assumption from becoming an annual reporting mistake. PCI SSC publishes standards and validation tools, but payment brands, acquirers, and other compliance-program operators determine what evidence they require and accept.
PCI SSC has specifically cautioned that SAQ eligibility criteria should not simply be repurposed as a universal applicability tool outside their intended validation context. Treat the questionnaire as a reporting mechanism for an eligible environment, not as a way to redesign scope after the fact.
Three Checkout Examples
Example 1: Full redirect
A retailer’s “Pay Now” button sends customers to a PCI DSS compliant processor’s hosted payment page. The processor generates the payment fields and handles account data. The retailer stores no electronic account data.
Likely direction: investigate SAQ A, subject to every eligibility criterion and the acquirer’s requirements.
Example 2: Provider-hosted iframe
The checkout remains visually inside the retailer’s website, but the account-data entry component is delivered by the compliant processor through an embedded iframe. The merchant does not electronically receive the account data.
Likely direction: SAQ A may apply if the implementation satisfies the current eligibility criteria, including relevant website-security conditions. Current SAQ A scanning requirements should also be reviewed.
Example 3: Merchant-generated Direct Post form
The merchant’s application creates the checkout form containing payment fields. On submission, the shopper’s browser posts the payment data straight to the processor, so the merchant’s server does not intentionally receive it.
Likely direction: investigate SAQ A-EP because the merchant-generated page can influence account-data collection and transaction security.
Copy an SAQ Selection and Evidence Record
Use this working note to keep the decision traceable. Store evidence references and sanitized observations, not card numbers, CVV values, secret keys or full browser network exports. Where an answer is unresolved, name the person who will resolve it.
Review date / responsible owner:
Merchant role / channels covered:
Checkout URLs or route references:
Provider product / integration / version:
Field origin / supporting implementation reference:
Browser submission destination / merchant data handling:
Other payment paths / support and logging review:
Provider evidence / responsibility allocation:
Candidate SAQ / current eligibility criteria checked:
Embedded-form script eligibility evidence if relevant:
Applicable ASV scan scope / owner / results reference:
Compliance-accepting entity / required documents / deadline:
Validation route confirmed by / date / written reference:
Unresolved questions / owners / due dates:
Change that triggers another review:
A useful request to the developer is: “Please identify who supplies the card-entry fields on each route and whether any merchant-controlled code receives account data before it reaches the provider. Link the deployed integration to the provider’s documentation and explain customizations.” If the answer only says “tokenized,” ask where tokenization occurs and what handles the data before that point.
Keep a separate record of merchant-level classification. Volume and brand rules influence reporting expectations, while the payment architecture informs SAQ eligibility. The card-brand merchant-level comparison explains why one number cannot determine the questionnaire.
Questions That Often Block SAQ Selection
Does adding analytics automatically make my checkout SAQ A-EP?
No automatic classification follows from that fact alone. Review the payment-data capture mechanism, script impact and complete eligibility criteria. Both redirect and embedded SAQ A environments can require website security work. A merchant website’s ability to affect a transaction is not, on its own, a sufficient A-versus-A-EP test.
What if the plugin guide says SAQ A but our custom code handles card data?
Resolve the discrepancy against the deployed flow. Generic product documentation cannot override what your implementation does. Document the custom data path and ask the compliance contact to confirm the appropriate assessment route before completing an attestation.
Can I classify the whole business from one online checkout?
No. Record other channels and retained integrations separately. A checkout review does not automatically cover telephone collection, manual entry, mobile acceptance or historical electronically retained account data. Confirm how the complete environment should be reported.
These answers guide evidence collection; they do not establish eligibility for a real merchant. A useful outcome is a documented decision or a clearly assigned unresolved question, rather than a guessed questionnaire.
Common SAQ Selection Mistakes
- Choosing SAQ A because it is shorter. Eligibility follows architecture, not convenience.
- Assuming “Stripe,” “PayPal,” or another provider name determines the SAQ. Integration method matters more than the logo on the checkout.
- Assuming no stored card numbers means SAQ A. SAQ A-EP can also apply where merchant systems do not electronically store account data.
- Classifying a checkout from its appearance. An iframe and a merchant-generated form can look almost identical to the shopper.
- Ignoring JavaScript. Browser-side compromise is a major ecommerce payment-security concern.
- Assuming SAQ A eliminates scanning. Current SAQ A ecommerce requirements can include ASV external vulnerability scans.
- Reusing last year’s SAQ without checking changes. PCI DSS guidance and supporting validation materials evolve.
- Letting a blog make the final determination. Documentation and your compliance-accepting entity should settle the reporting path.
SAQ A vs SAQ A-EP: Which One Should You Complete?
Start with the payment architecture, not the questionnaire.
If your card-not-present payment functions are fully outsourced, your merchant systems do not electronically store, process, or transmit account data, and the payment-data entry mechanism comes from compliant third-party providers, SAQ A may be the appropriate validation route when all current eligibility criteria are satisfied.
If you are an ecommerce merchant whose systems still do not electronically store, process, or transmit account data but whose website generates or controls payment-page elements capable of affecting the transaction, SAQ A-EP may be the appropriate route.
If cardholder data actually passes through or resides on systems you control, stop trying to choose between A and A-EP until the wider environment has been scoped. A different SAQ or validation method may be required.
The most useful next action is a one-page payment-flow diagram. Mark your website, browser, payment fields, processor, third-party scripts, APIs, redirects, and every location where account data might travel. Then compare that diagram against the current SAQ eligibility criteria and ask the entity accepting your PCI validation to confirm the expected form.
The diagram should be detailed enough to resolve the actual eligibility questions. Completion time is not a readiness test. Record unknowns and evidence references before signing the applicable attestation.
Official References and Review Boundaries
- PCI SSC FAQ 1291: Direct Post, iframe and redirect distinctions.
- PCI SSC FAQ 1293: payment-page element origins and full eligibility.
- PCI SSC FAQ 1588: embedded-form script eligibility.
- PCI SSC FAQ 1604: SAQ A external scanning.
- PCI SSC FAQ 1331: SAQ criteria and applicability decisions for ROC assessments.
- PCI SSC document library: current questionnaires and instructions.
Editorial review: November 16, 2026. Checked the linked PCI SSC guidance and added an evidence checklist, a selection record and clarification of the SAQ A revision. FAQs 1291 and 1293 explain the architectural distinction but predate the current SAQ revision; use them together with the current forms and newer FAQs. No live checkout, merchant account or payment data was accessed or tested.