Skip to content

Kioptrix Labs

Practical cybersecurity guides, labs & compliance

  • Home
  • Start Here
    • Beginner Roadmap
  • Downloads
    • Level 1 Setup
    • Level 3 Setup
  • About
    • Privacy Policy
    • Terms of Service & Disclaimer
    • Contact
  • Cybersecurity
  • Kali Linux
  • Compliance Guides
    • PCI DSS
  • All Articles

Vendor Risk Management

SaaS Security Addendum: Review Obligations Before Signing
October 24, 2026September 13, 2026 by Kioptrix Labs
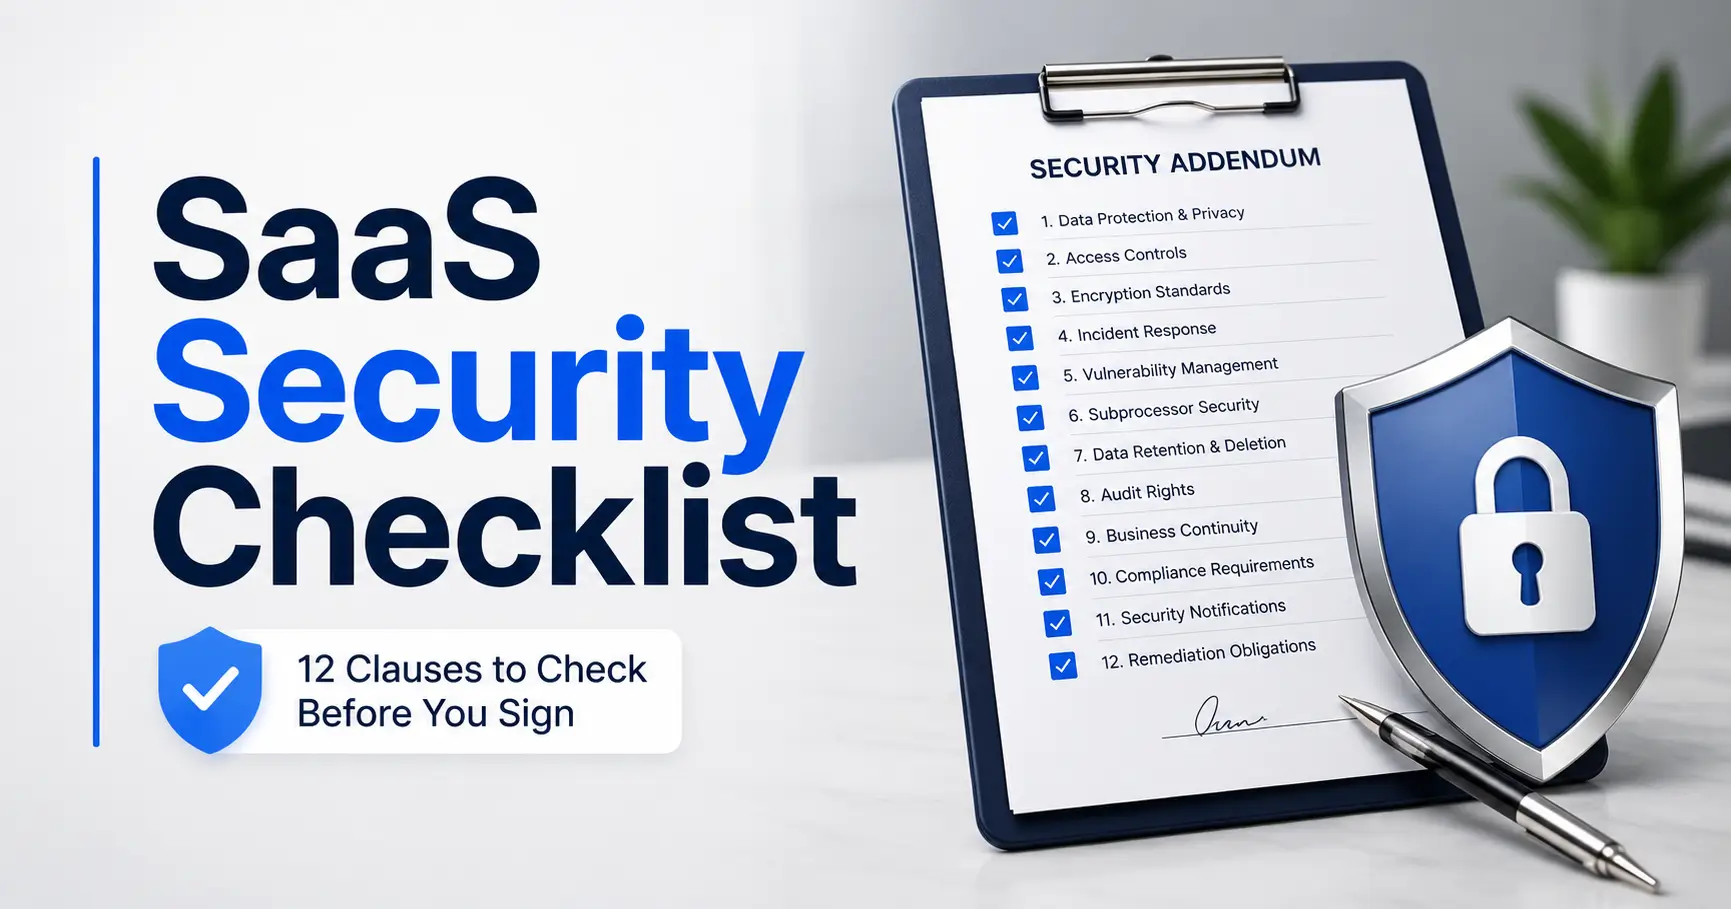
SaaS Security Addendum Checklist

Review a SaaS security addendum against the controls and processes your team can actually support. Check incident triggers, audit scope, subprocessors, deletion and backup exceptions, then record gaps and responsible reviewers before agreeing to commitments.
Categories Cybersecurity Tags Cybersecurity Compliance, SaaS Contracts, SaaS security, Vendor Risk Management

Answer Encryption Questions With Scoped Evidence

October 24, 2026September 6, 2026 by Kioptrix Labs
Encryption questionnaire

Answer customer encryption questions by mapping transport, storage, backups and key responsibility. Use the coverage register to connect each statement to dated configuration evidence and disclose exceptions or unreviewed systems.

Categories Cybersecurity Tags Compliance, Encryption, SaaS security, Vendor Risk Management

Answer Customer Security Questionnaires Accurately

October 24, 2026August 23, 2026 by Kioptrix Labs
customer security questionnaire

Prepare scoped customer security answers with approved evidence. Distinguish current capabilities from plans, qualify partial coverage, and use the approval record and contradiction review before making a customer commitment.

Categories Cybersecurity Tags cybersecurity tools, enterprise sales, SaaS security, Security Compliance, Vendor Risk Management

Vendor Security Questionnaire Template: Evidence First

October 24, 2026August 22, 2026 by Kioptrix Labs
Vendor security questionnaire template

Assess a vendor for the service and data access you intend to use. Adapt the questionnaire, link each claim to dated evidence, and complete the review decision card with owners, exceptions and follow-up actions.

Categories Cybersecurity Tags Cybersecurity Compliance, SaaS security, Third-Party Risk, Vendor Risk Management

SOC 2 Type 1 vs Type 2: Which Report Do Buyers Need?

October 24, 2026August 20, 2026 by Kioptrix Labs
SOC 2 Type 1 vs Type 2

Compare a SOC 2 report with your actual buying requirement. Review scope, date or period, opinion and exceptions, then use the acceptance record to document missing evidence and follow-up questions.

Categories Cybersecurity Tags Cybersecurity Audits, SaaS security, SOC 2 Compliance, Vendor Risk Management

Choose your next step

Browse guides by task

Hands-on labs

  • Set up Level 1
  • Fix a VM or network error
  • Choose the next check
  • Walkthrough & hints

Records & projects

  • Copy a lab session note
  • Create a review record
  • Present a learning project

Business security

  • Choose a compliance framework
  • CMMC preparation
  • FedRAMP budgeting

All articles · Author & evidence policy

E-mail:

dalo78@naver.com

  • About
  • All Articles
  • Find a Guide
  • Kioptrix Downloads
  • Kioptrix Level 1 Download & Setup Guide
  • Kioptrix Level 3 Download & Setup Guide
  • Privacy Policy
  • Start Here: Kioptrix Labs, Tools & Security Guides
  • Terms of Service & Disclaimer
© 2026 Kioptrix Labs • Built with GeneratePress