Security Addendum Checklist for SaaS Contracts: 12 Clauses to Check Before You Sign
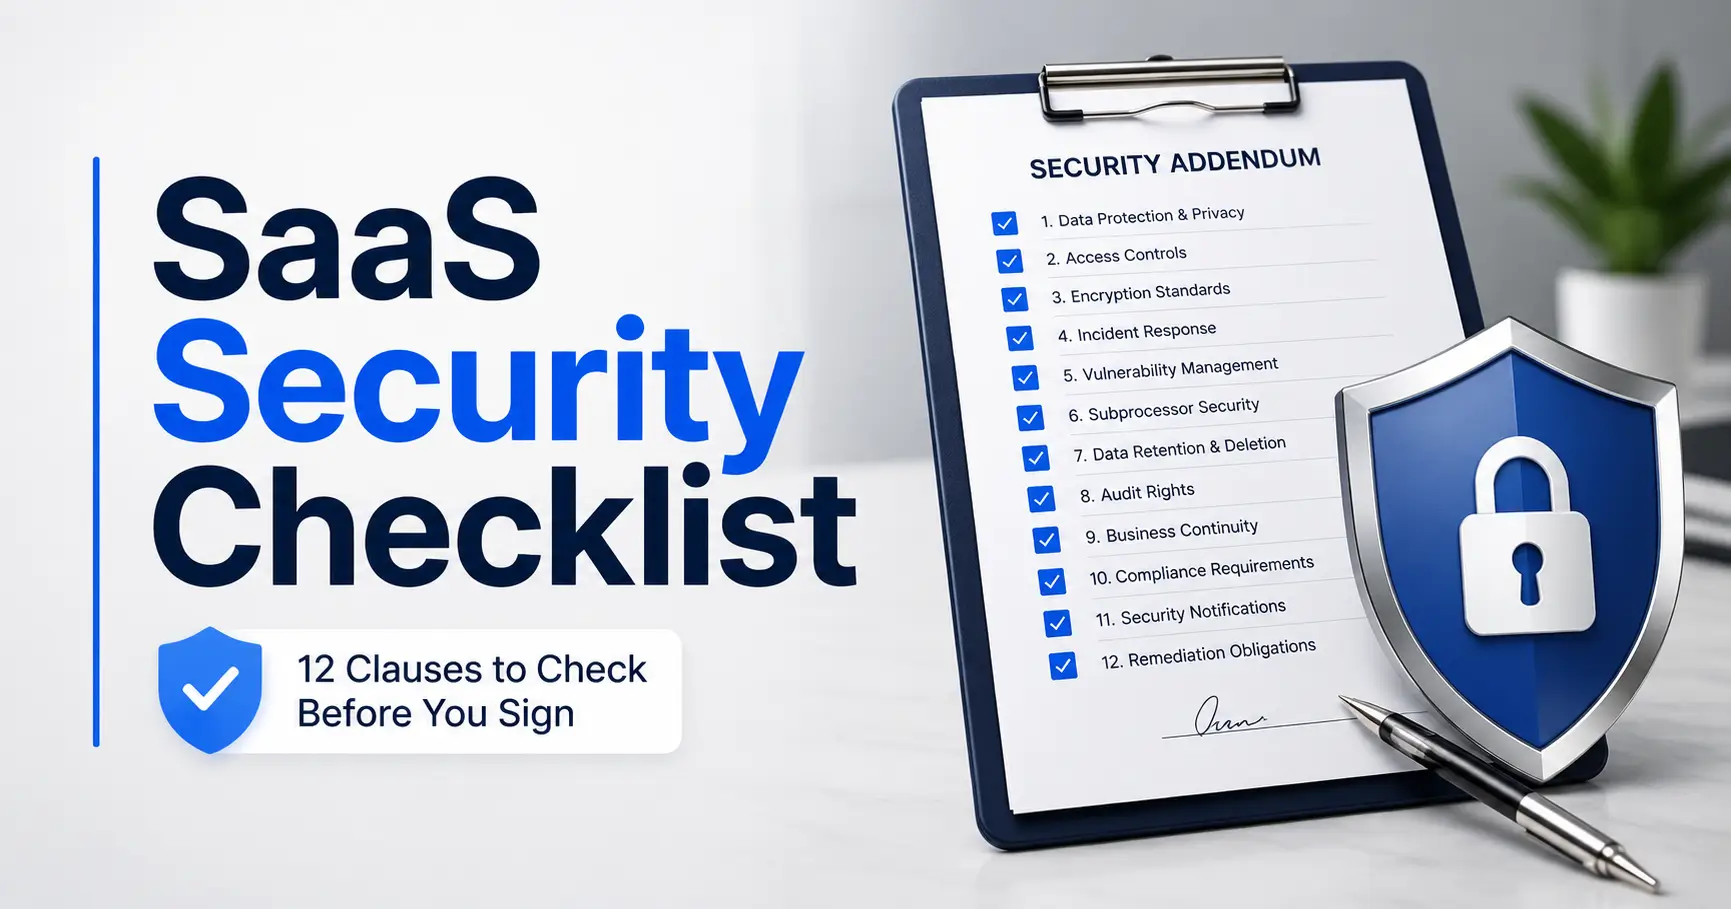
SaaS Security Addendum Checklist

SaaS Procurement & Vendor Risk Security Addendum Checklist for SaaS Contracts:12 Clauses to Check Before You Sign A SaaS agreement can look reassuringly polished while leaving the uncomfortable questions in soft focus. Who can access your data? How quickly must the vendor tell you about an incident? What happens if a subprocessor fails? And after … Read more

Manual Pentest vs Automated Scanner: Buy the Coverage You Actually Need

Manual Pentest vs Automated Scanner

Security Testing Buyer Guide Manual Pentest vs Automated Scanner:Buy the Coverage You Actually Need The awkward part of buying security testing is that two vendors can promise to “find vulnerabilities” while selling substantially different things. One may give you continuous automated visibility across hundreds of assets. Another may spend days following application workflows, validating suspicious … Read more

Security Questionnaire Answers for Encryption: Say Exactly What You Can Defend

Encryption questionnaire

Security due diligence without accidental promises Security Questionnaire Answers for Encryption:Say Exactly What You Can Defend An encryption question may occupy one line in a customer spreadsheet, yet the answer can quietly become a sales representation, an audit artifact, and a contractual expectation. That is why “Yes, AES-256” is rarely the reassuring answer it appears … Read more

MVP Threat Modeling for Startups: Secure SaaS Before Launch

MVP threat modeling for startups

Founder-Friendly SaaS Security MVP Threat Modeling for Startups:Secure SaaS Before Launch A startup rarely loses sleep over an abstract threat category. It loses sleep over the customer who can see another company’s records, the leaked deployment key discovered on a Friday evening, or the support request that quietly turns into an account takeover. MVP threat … Read more

API Security Checklist for SaaS Founders: 12 Controls to Verify Before Launch

API security checklist for SaaS founders

SaaS launch security guide API Security Checklist for SaaS Founders:12 Controls to Verify Before Launch Your API may pass every happy-path test and still allow one customer to read another customer’s invoices. It may authenticate users correctly while exposing an administrative action through an undocumented route. It may also turn a perfectly valid request into … Read more

Azure Security Baseline for SaaS Startups: Secure the company before the next security questionnaire

Azure security baseline for SaaS

A practical 30-day hardening roadmap Azure Security Baseline for SaaS Startups: Secure the company before the next security questionnaire The first serious enterprise prospect often arrives carrying two things: promising revenue and a spreadsheet filled with questions about access control, encryption, logging, backups, incident response, and vendor risk. At that moment, security stops feeling like … Read more

How to Answer a Customer Security Questionnaire Without Delaying the Deal

customer security questionnaire

Enterprise Sales Security Guide How to Answer a Customer Security QuestionnaireWithout Delaying the Deal A customer security questionnaire often arrives disguised as a spreadsheet. In practice, it is part technical assessment, part sales checkpoint, part evidence request, and sometimes part contract negotiation wearing sensible office shoes. The fastest response is not the one filled with … Read more

Vendor Security Questionnaire Template for SaaS Decisions You Can Defend

Vendor security questionnaire template

Practical SaaS Vendor Risk Assessment Vendor Security Questionnaire Template for SaaS Decisions You Can Defend A vendor questionnaire should help you decide whether a SaaS product is safe enough for its intended job. It should not become a ceremonial spreadsheet passed between inboxes until everyone is too tired to ask what the answers mean. The … Read more

SOC 2 Type 1 vs Type 2: Which Report Do Buyers Need?

SOC 2 Type 1 vs Type 2

Enterprise Vendor Risk Guide SOC 2 Type 1 vs Type 2:Which Report Do Buyers Need? A vendor says, “We have SOC 2.” The sales team exhales. Procurement checks a box. Everyone inches toward signature day. Then someone opens the report and discovers that the controls were examined on one date, the relevant product is missing … Read more

SOC 2 Policies Every Startup Needs Before the Audit Gets Real

SOC 2 policies for startups

Startup compliance without the fog machine SOC 2 Policies Every Startup NeedsBefore the Audit Gets Real SOC 2 pressure rarely arrives politely. One week your startup is shipping features, patching bugs, and trying to close deals. The next week an enterprise buyer asks for your SOC 2 report, your security questionnaire grows teeth, and every … Read more