Skip to content

Kioptrix Labs

Practical cybersecurity guides, labs & compliance

  • Home
  • Start Here
    • Beginner Roadmap
  • Downloads
    • Level 1 Setup
    • Level 3 Setup
  • About
    • Privacy Policy
    • Terms of Service & Disclaimer
    • Contact
  • Cybersecurity
  • Kali Linux
  • Compliance Guides
    • PCI DSS
  • All Articles

Practice Labs & Tools

Rubber Duck Debugging: Five Steps and an Experiment Card
October 24, 2026October 11, 2026 by Kioptrix Labs
A programmer practices rubber duck debugging at a cozy desk beside a laptop and coffee.

Explain expected and observed behavior, identify one assumption, and choose a test that distinguishes possible causes. Follow five debugging steps, a worked example, and an editable experiment card for your own notes.
Categories Practice Labs & Tools Tags cybersecurity training

Vulnerability Retesting Checklist: Five Checks and a Closure Record

October 24, 2026October 9, 2026 by Kioptrix Labs
Vulnerability retesting concept with a server, magnifying glass, shield, and the words Verify the Fix

Retest a specific vulnerability after an authorized change. Five checks cover deployment, comparable conditions, secure behavior and closure evidence. Includes a worked inconclusive result and an editable record for remediation, mitigation or unresolved status.

Categories Practice Labs & Tools Tags Cybersecurity Labs, cybersecurity training

Nmap Enumeration Flags: Reference, Command Patterns and Limits

October 24, 2026September 10, 2026 by Kioptrix Labs
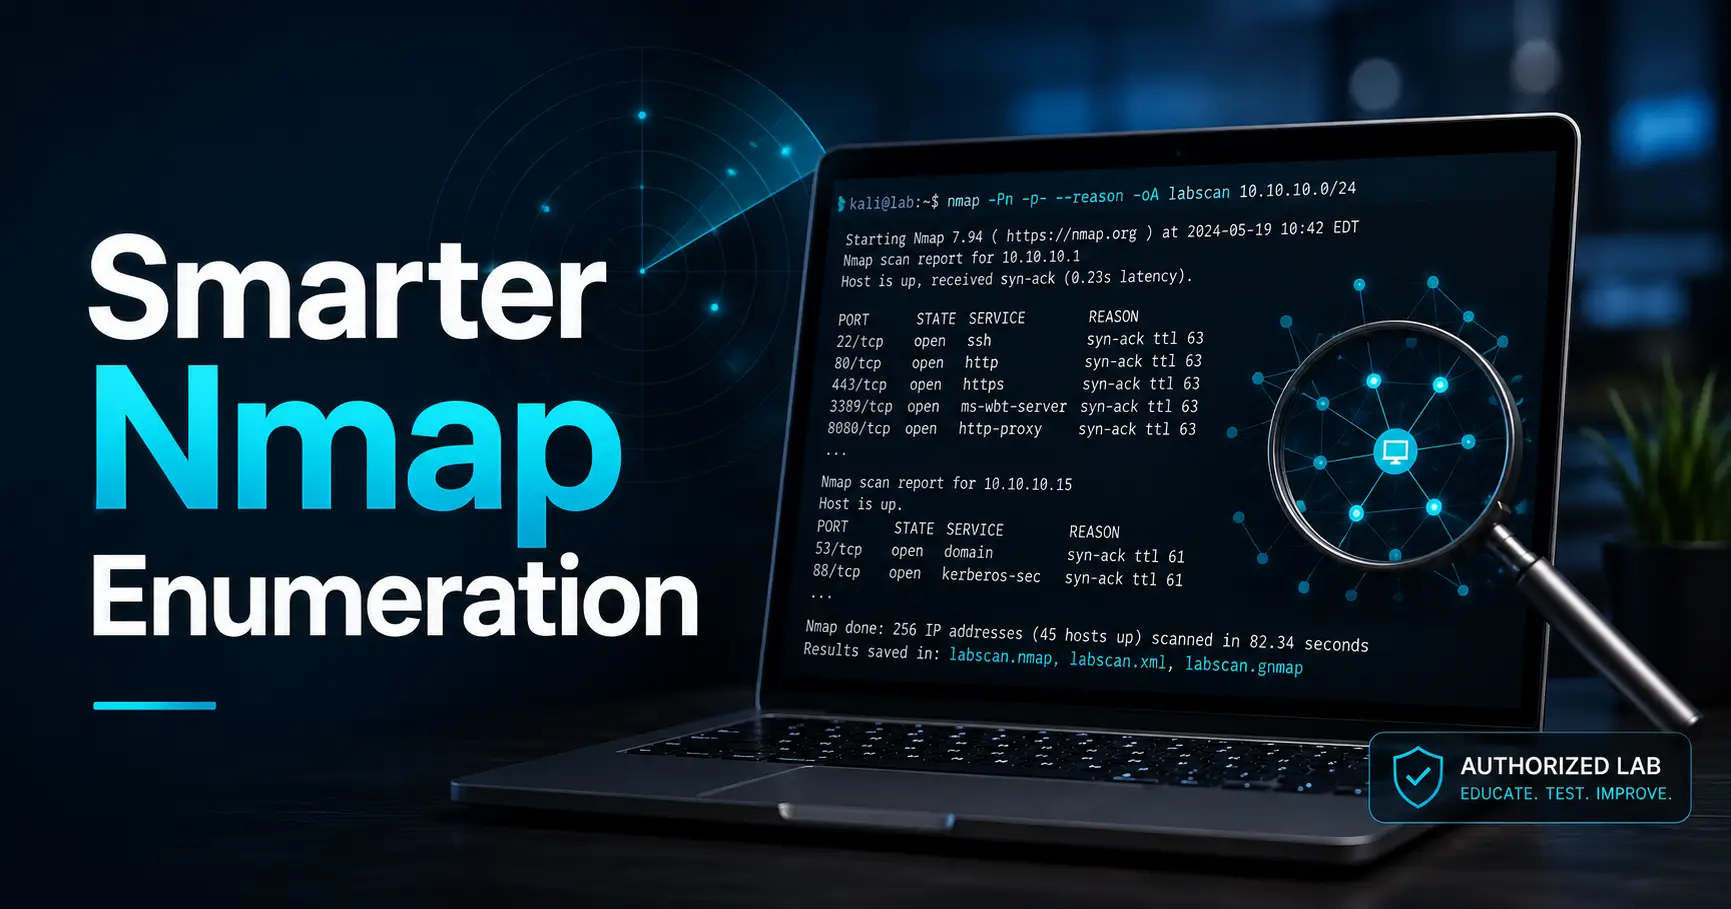
Nmap flags for enumeration

Build an Nmap command you can explain: targets, discovery, ports, service probes and saved output. Includes a flag reference, isolated-lab command ladder and five review questions before rerunning a scan.

Categories Kioptrix Series, Practice Labs & Tools Tags Cybersecurity Labs, Network Enumeration, nmap, penetration testing

NoSQL Injection Labs: Check Query Construction

October 24, 2026August 12, 2026 by Kioptrix Labs
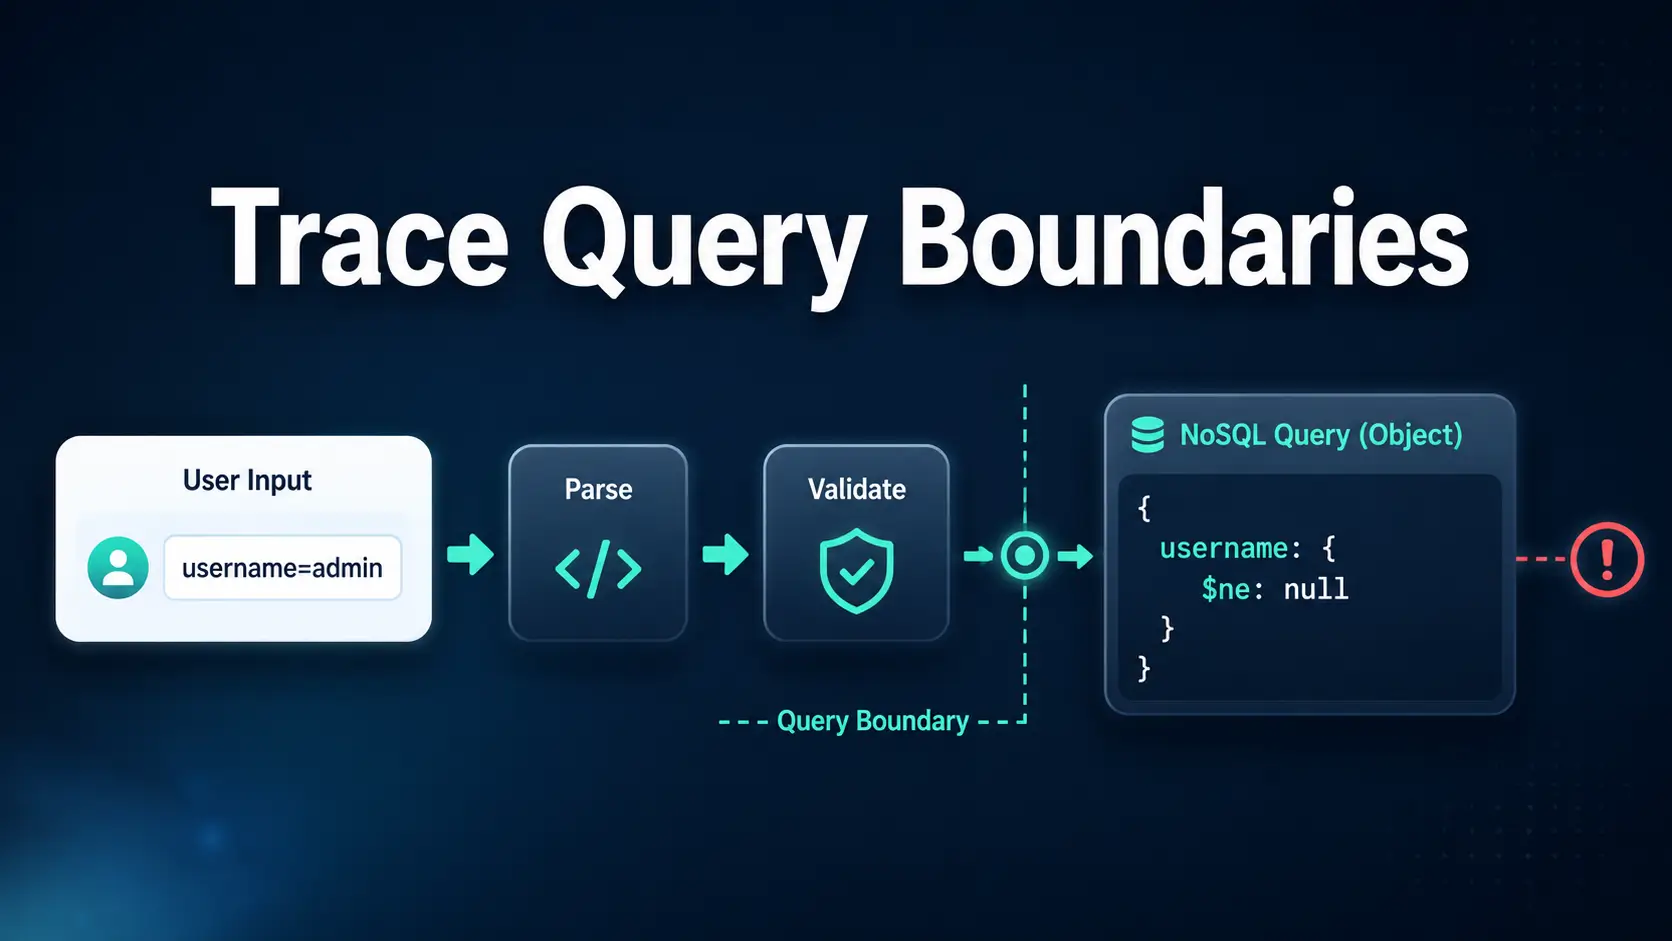
NoSQL Injection Testing

Trace one NoSQL input from its parser and expected type to the database query. Use the query-boundary review and worked example to document observed behavior, remaining uncertainty and repair checks.

Categories Practice Labs & Tools, Cybersecurity Tags NoSQL Security, penetration testing, Secure Coding, Web Application Security

Web Exploitation Practice: Evidence in Authorized Labs

October 24, 2026August 6, 2026 by Kioptrix Labs
web exploitation labs

Define a permitted web-lab exercise and the security boundary you expect. Use the boundary record and worked example to preserve controlled observations, compare explanations and avoid unsupported vulnerability claims.

Categories Practice Labs & Tools Tags cybersecurity, ethical hacking, IT Training, OWASP, Web Security

Privilege Escalation Notes: Avoid Unsupported Paths

October 24, 2026August 4, 2026 by Kioptrix Labs
privilege escalation for beginners

Review a proposed privilege-escalation path against the identity, permissions and prerequisites actually observed. Use the hypothesis filter to choose the next authorized check and document absent evidence or an unchanged boundary.

Categories Practice Labs & Tools, Cybersecurity Tags Beginner Guides, cybersecurity, ethical hacking, IT Security, penetration testing

Nmap Version Detection: Check a Suspected False Positive

October 24, 2026August 1, 2026 by Kioptrix Labs
nmap -sV false positives

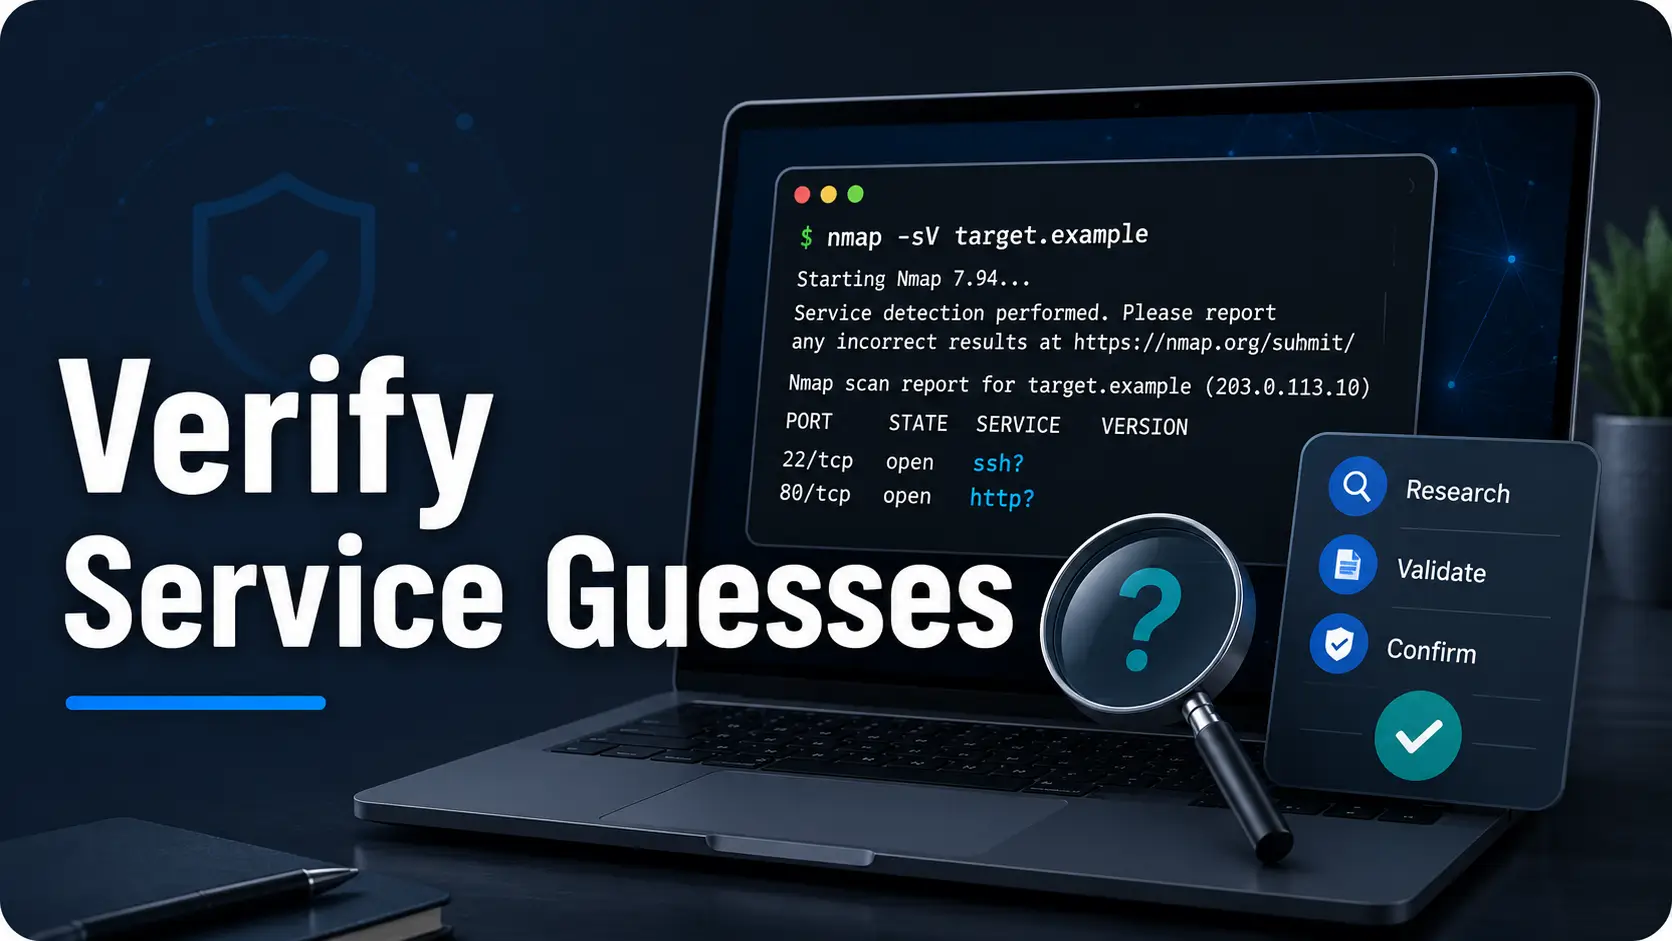
Check a suspected Nmap version false positive using probe context, XML output and authorized package evidence. Use the verification record to separate a service clue from confirmed vulnerability prerequisites.

Categories Practice Labs & Tools Tags cybersecurity, ethical hacking, nmap, SOC Training, Vulnerability Management

SMB Enumeration Checklist: Follow the Failure Stage

October 24, 2026July 30, 2026 by Kioptrix Labs
SMB enumeration checklist

Troubleshoot SMB enumeration by separating transport, negotiation, session setup, tree connect and file operations. Use the permission matrix and working record to document the last successful stage, exact error and next controlled check.

Categories Practice Labs & Tools, Pentest for Founders Tags cybersecurity, ethical hacking, Network Security, penetration testing, SMB Security

PHP App Recon: Routes, State and Evidence Limits

October 24, 2026March 15, 2026 by Kioptrix Labs
Kioptrix PHP recon

Review a PHP-style application by recording routes, inputs, account context and state transitions. Use the task record to separate implementation hints from demonstrated authentication, authorization or injection behavior.

Categories Kioptrix Series, Practice Labs & Tools Tags beginner-guides, kioptrix, pentesting, PHP-security, web-recon

Vulnerability Disclosure Intake: Reporting Routes and Policy Review

October 24, 2026February 21, 2026 by Kioptrix Labs
Vulnerability Disclosure Policy

Prepare vulnerability-disclosure intake with a monitored reporting route, an owner and a publication review. Use the record to separate contact-file checks from policy scope, response commitments and authorization to test.

Categories Practice Labs & Tools Tags cybersecurity, SaaS security, security.txt, vulnerability disclosure
Older posts
Page1 Page2 Next →

Choose your next step

Browse guides by task

Hands-on labs

  • Set up Level 1
  • Fix a VM or network error
  • Choose the next check
  • Walkthrough & hints

Records & projects

  • Copy a lab session note
  • Create a review record
  • Present a learning project

Business security

  • Choose a compliance framework
  • CMMC preparation
  • FedRAMP budgeting

All articles · Author & evidence policy

E-mail:

dalo78@naver.com

  • About
  • All Articles
  • Find a Guide
  • Kioptrix Downloads
  • Kioptrix Level 1 Download & Setup Guide
  • Kioptrix Level 3 Download & Setup Guide
  • Privacy Policy
  • Start Here: Kioptrix Labs, Tools & Security Guides
  • Terms of Service & Disclaimer
© 2026 Kioptrix Labs • Built with GeneratePress