MDR Pricing for Small Businesses: 9 Checks Before You Buy
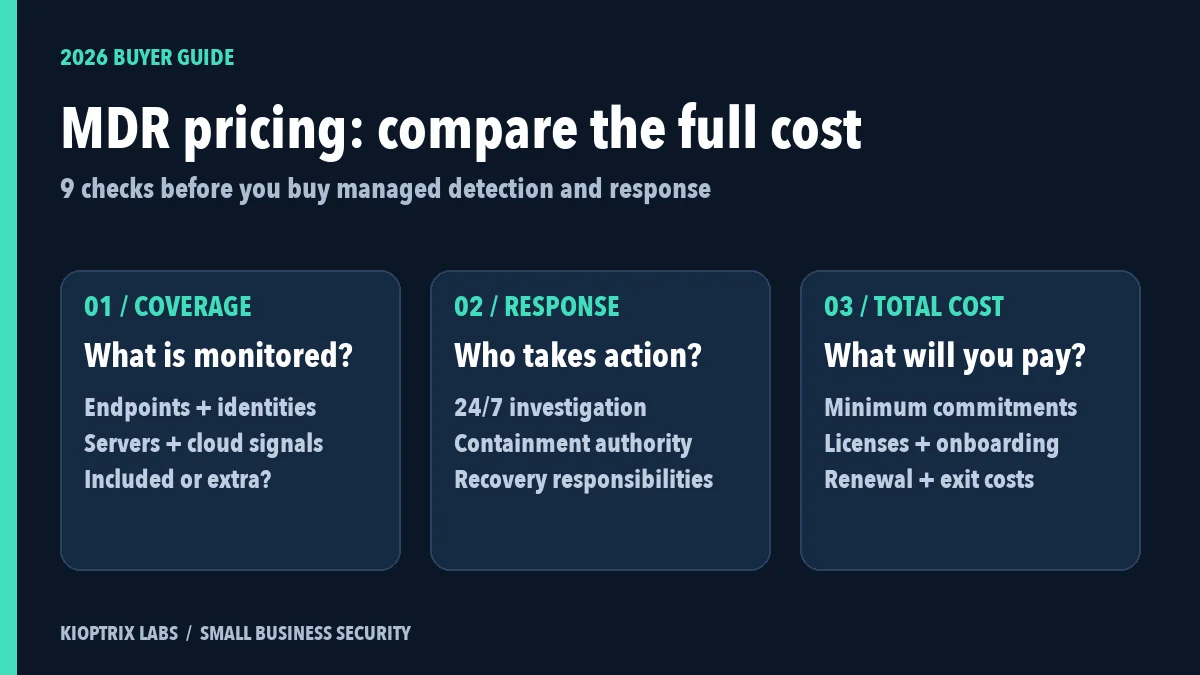
Compare MDR pricing for small businesses with nine quote checks, three service models, a worked annual budget, and a copyable vendor worksheet.
Practical cybersecurity guides, labs & compliance
Compare MDR pricing for small businesses with nine quote checks, three service models, a worked annual budget, and a copyable vendor worksheet.
Check your Atlassian deployment against the linked CVE-2026-21589 advisory. Follow seven response checks covering instance inventory, exposure, patching, log preservation and node verification, with a register for unresolved evidence.

Choose between manual pentesting and automated scanning using a defined testing brief. Compare authenticated roles, business logic, validation, reporting and retesting, with questions to ask providers about actual coverage.
Evaluate questionnaire automation using your own review workflow. Compare answer reuse, evidence mapping, access controls and reviewer effort, then use the assertion review record to keep scope, dates and exceptions attached to each answer.
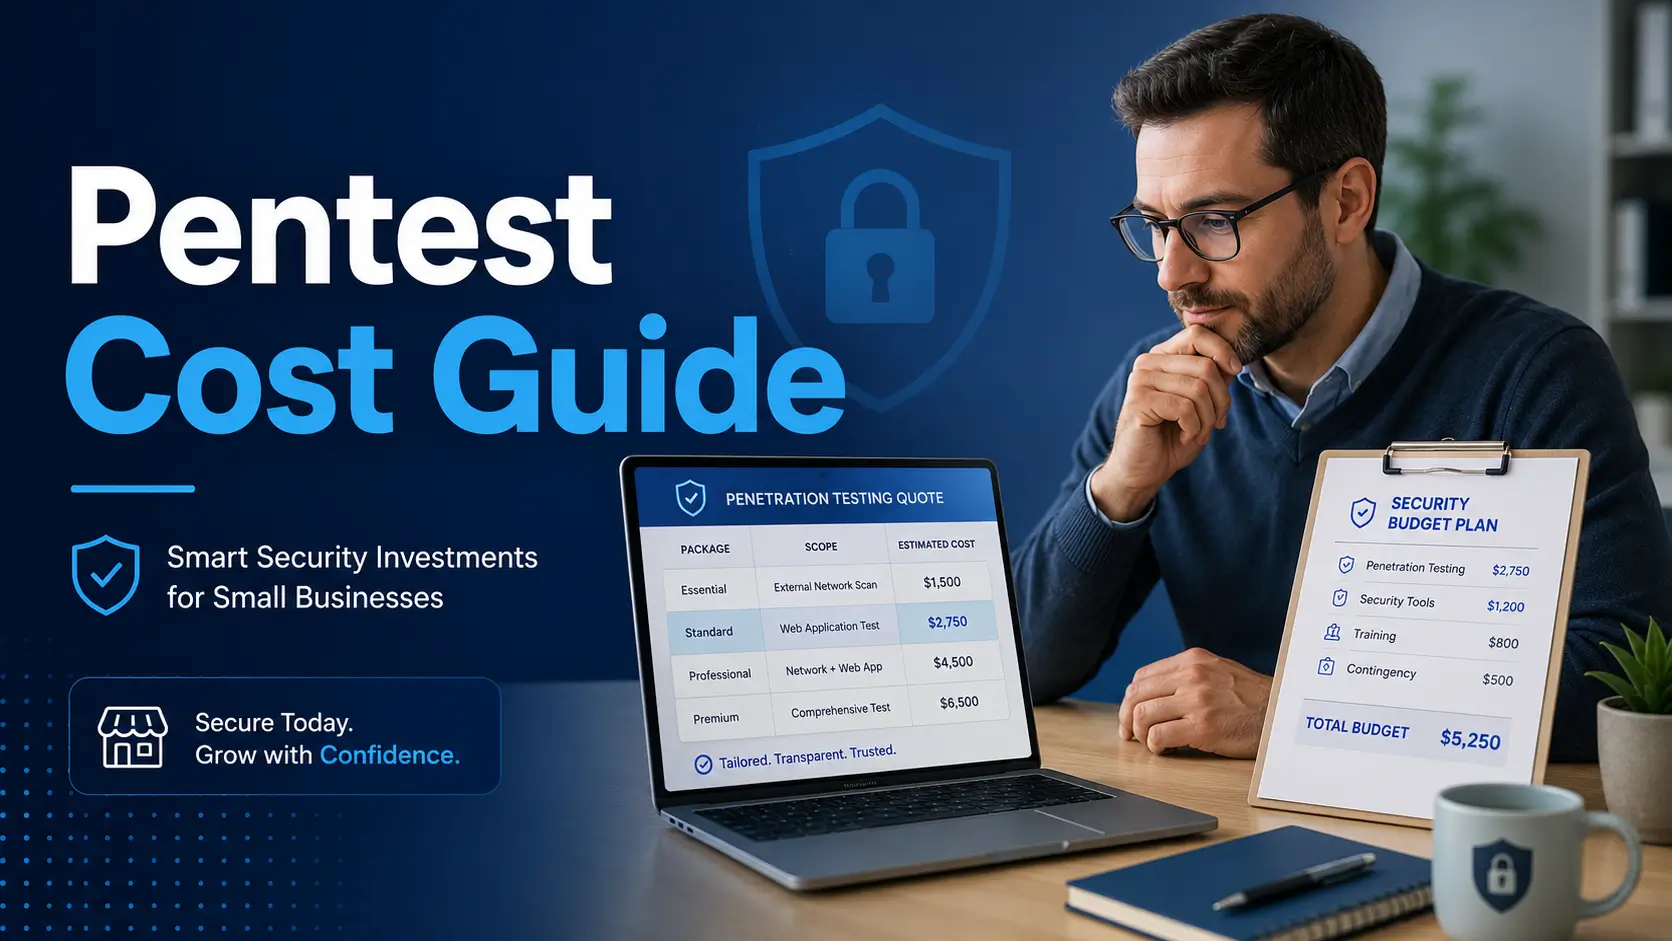
Compare small-business pentest proposals using the same assets, roles and workflows. Build a scope brief, check exclusions and retest terms, and keep hypothetical budget examples separate from actual supplier quotes.
Build a SaaS startup SOC 2 budget from examination scope, readiness, software, remediation and staff work. Keep external cash and internal labor separate, compare equivalent CPA proposals, and avoid double-counting bundled services.
Test scoped API authorization across roles, object ownership and tenant boundaries. Use the expectation matrix and two-tenant drill to record allowed and denied operations, supporting evidence and endpoints still unreviewed.
Plan seven flexible cybersecurity practice sessions, each with a saved artifact. Check prerequisites, track observations and verification, then decide when to repeat a task, use a hint or choose the next skill.
Prepare a cyber-insurance questionnaire evidence pack with dated control records, population coverage and owned exceptions. Verify assertions such as enforced MFA and tested restoration before submitting answers for review.
Define a permitted web-lab exercise and the security boundary you expect. Use the boundary record and worked example to preserve controlled observations, compare explanations and avoid unsupported vulnerability claims.