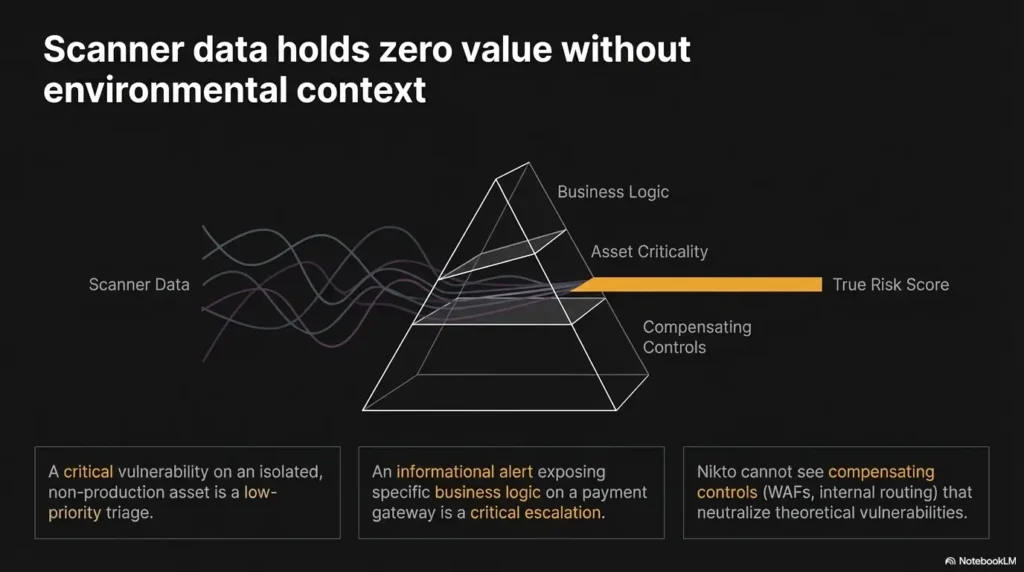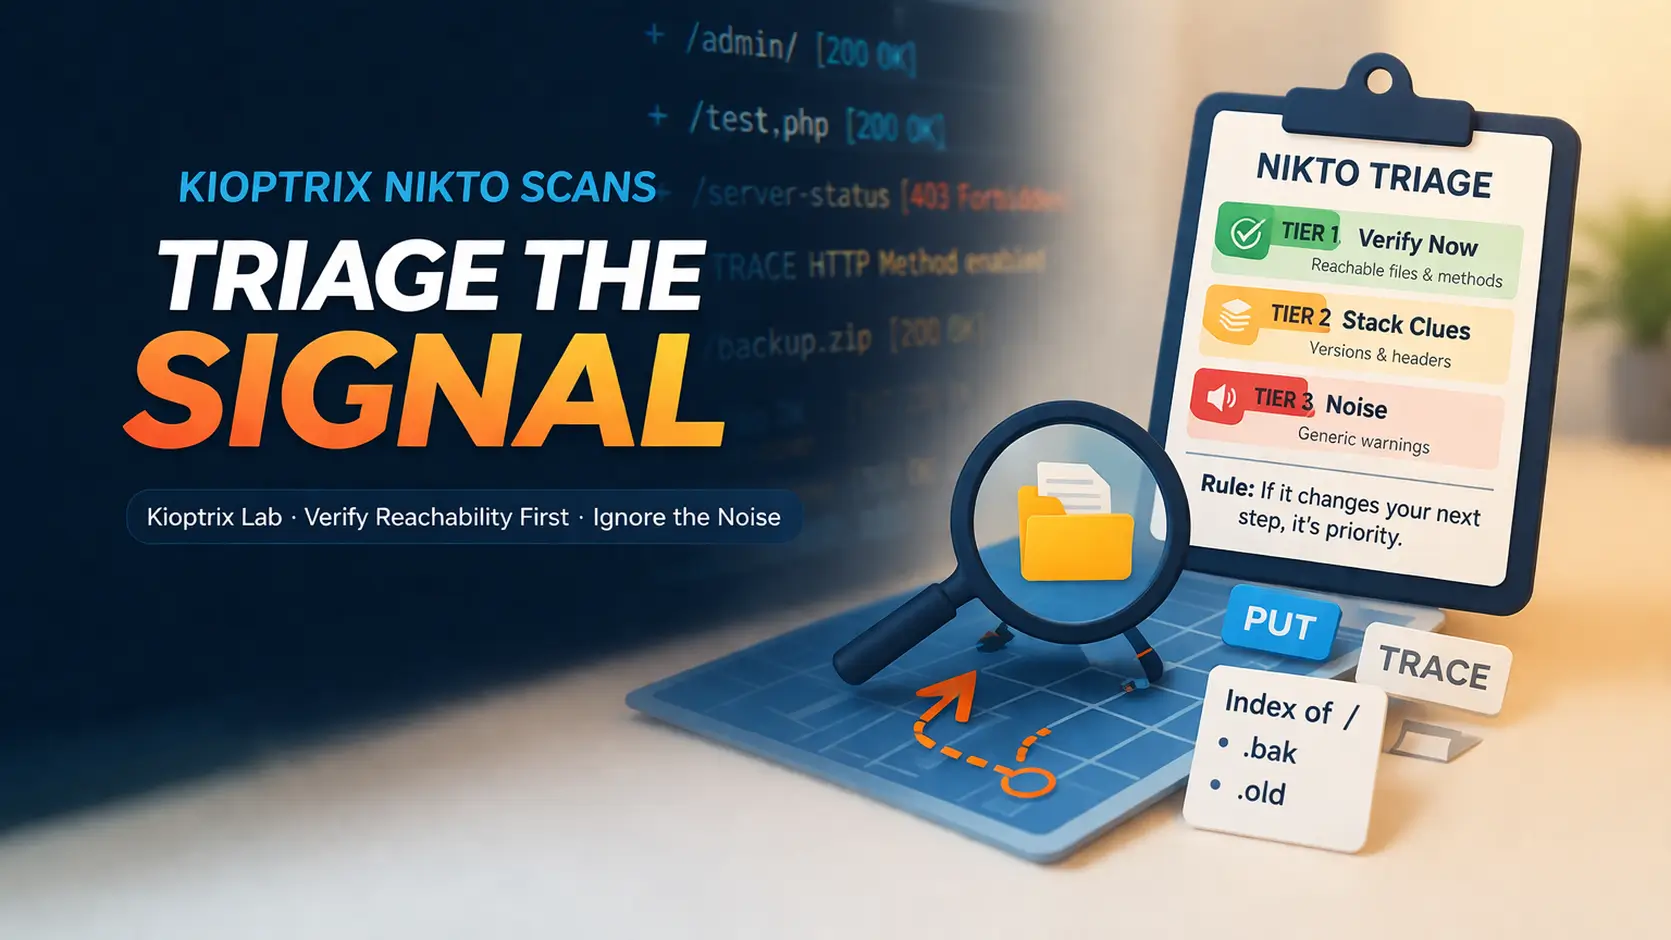
A Nikto alert is a candidate for review. Preserve the request context, confirm what the server returned, and decide whether the claimed issue applies. This guide helps you produce a defensible finding or an explicit unresolved item, rather than counting scanner lines as confirmed vulnerabilities.
Official Documentation: the Nikto project describes informational and application-specific checks as well as false-positive reduction. Its documentation discusses response-based false positives. The examples below are illustrative; no scan was executed for this update.
Preserve enough context to reproduce the observation
- Confirm the single authorized target, scheme, port and hostname. Keep redirects inside scope.
- Record Nikto version, database revision where available, scan options, time, authentication context, completion state and errors.
- Save the exact candidate URL, alert wording and matching request/response. A summary line alone is weak evidence.
- Compare a normal response and a missing-resource response under the same relevant conditions.
- Record the missing condition between the observation and the claimed impact. Keep the conclusion provisional when that condition is untested.
Interpret each kind of alert on its own evidence
| Observation | Useful follow-up | What it does not prove |
|---|---|---|
| Old-looking server banner | Check vendor advisory, build, modules and configuration prerequisites. | A banner alone does not establish exploitability. |
| Reported backup or default file | Compare actual content with a missing-path control and authentication behavior. | HTTP 200 alone does not prove the named file exists. |
| Directory indexing | Record visible entries and intended access policy using lab data. | A listing alone does not establish sensitive disclosure. |
| Missing security header | Check the affected response and application context; explain a realistic consequence. | It is not automatic account compromise. |
| PUT, DELETE or TRACE advertised | Separate advertised methods from authorization and behavior on a particular resource. | An Allow response is not permission to write or delete content. |
| Repeated generic page or redirect | Compare final destination, body and request context; group duplicate root causes. | Many matching lines are not many independent weaknesses. |
Worked example: a false file-exposure lead
Illustrative Example: Nikto reports a backup path. Both that path and a known-missing path return the same generic page with status 200. Record this as an unconfirmed scanner candidate, with the control response that weakens it. If a later request returns actual archive content, append the new evidence and reassess rather than erasing the earlier uncertainty.
Keep validation proportionate and authorized
Inspection can still affect a service. Keep the vulnerable VM isolated and save a recovery point. State-changing validation needs explicit scope and a disposable lab resource. Do not DELETE existing content to demonstrate a method, collect unrelated secrets, or follow an external redirect just because a scanner found it.
Use testable-claim planning to define a distinguishing check. If the application stops responding, preserve the error and use the troubleshooting workflow.
How should I prioritize the remaining candidates?
Start with observations that can be checked within scope and that resolve a meaningful uncertainty. Consider evidence strength, possible impact, applicability and recovery cost separately. A quick-to-check header warning is not automatically more severe than an unresolved service issue. This is an editorial triage method, not a calibrated risk score.
Nikto finding validation record
Complete one record, then generate a summary to copy or download. Use sanitized notes only. This tool has no server submission or automatic local saving; page reloads clear the form.
Further reference: OWASP Web Security Testing Guide. Preserve original scan evidence in the recon log.
Revised October 20, 2026 (UTC). Removed unverified personal anecdotes and repeated generic encouragement; added distinct alert interpretation, a negative-control example and exportable finding notes. Author and evidence policy.