CMMC Requirements for MSPs Serving Defense Contractors
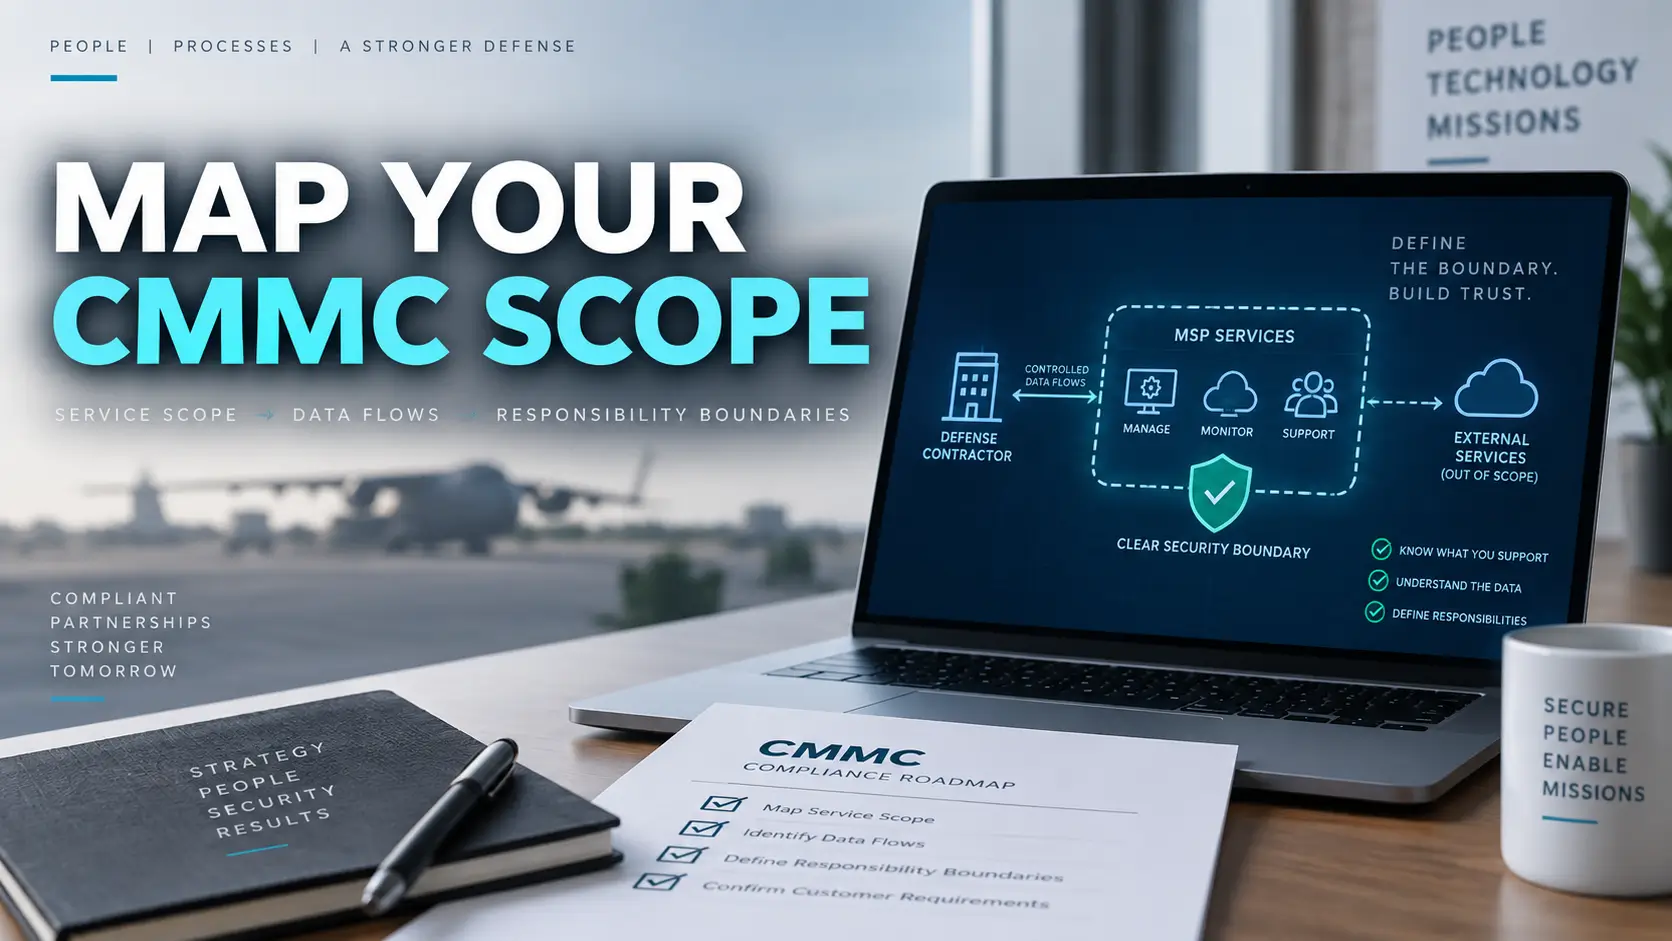
CMMC requirements for MSPs

An MSP serving defense contractors does not automatically need its own CMMC certification. The decisive question is what the MSP actually does with Federal Contract Information (FCI), Controlled Unclassified Information (CUI), and Security Protection Data (SPD), and whether the provider is functioning as an MSP, another type of External Service Provider (ESP), or a Cloud … Read more
CMMC Compliance for Subcontractors

CMMC compliance for subcontractors

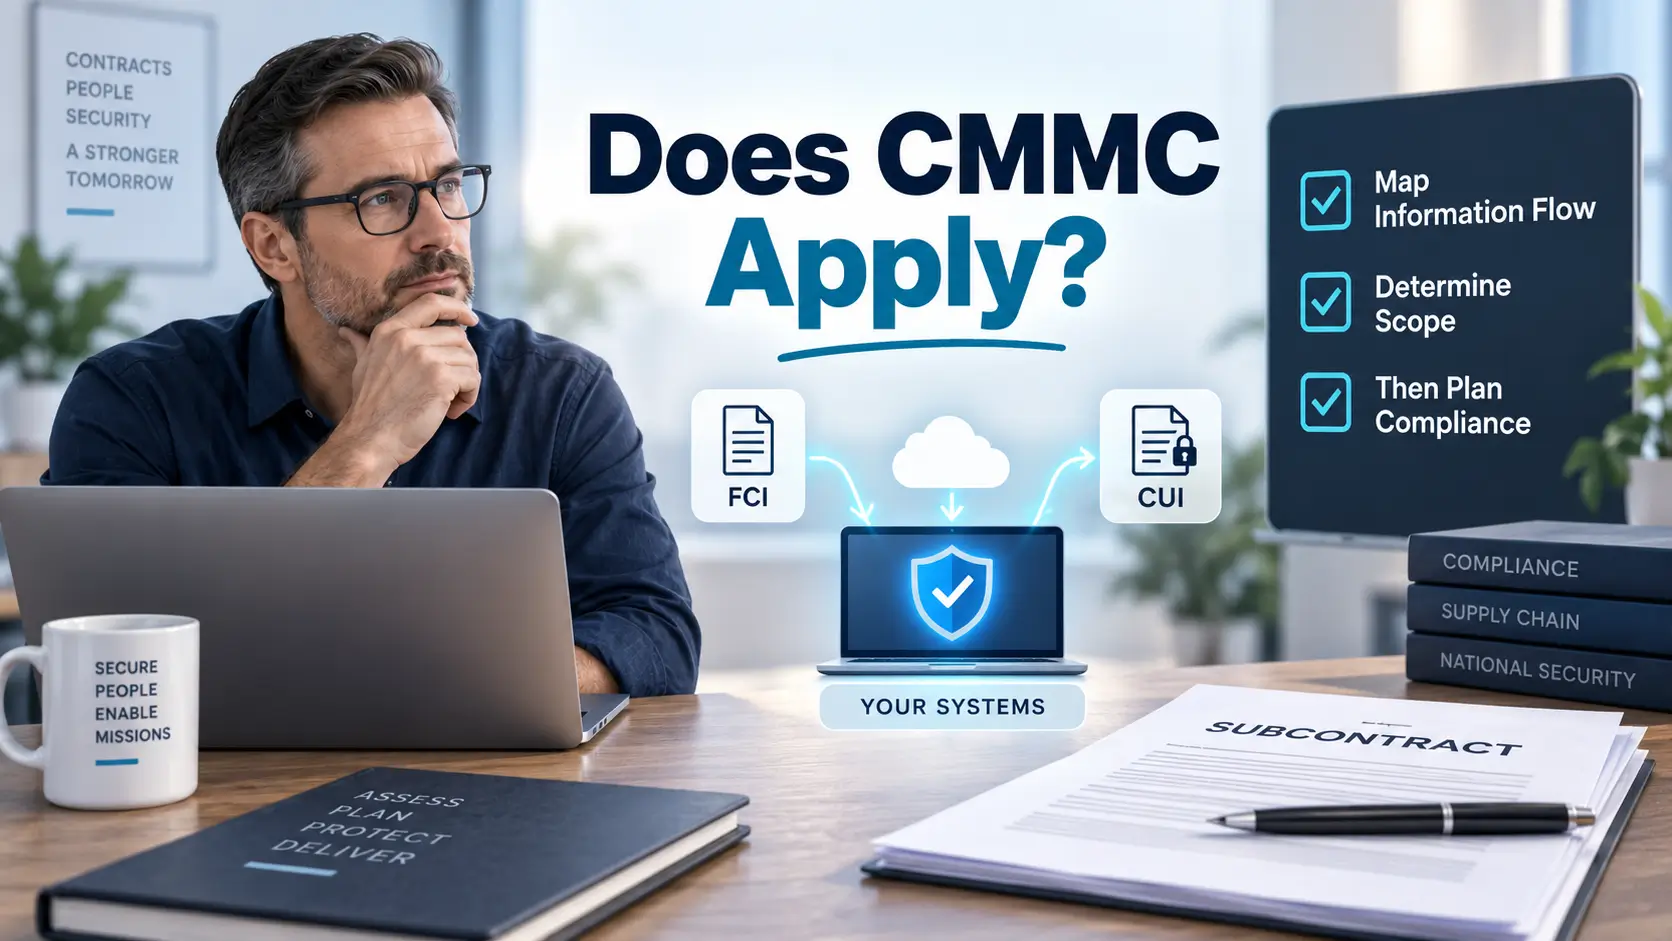
If you are a subcontractor on a U.S. defense contract, CMMC does not automatically mean “get Level 2 certified.” The first question is much narrower: Will your subcontract require your systems to process, store, or transmit Federal Contract Information (FCI) or Controlled Unclassified Information (CUI)? Open the practical working record to document this decision with … Read more

CMMC Scoping Guide for Small Defense Contractors

CMMC scoping guide

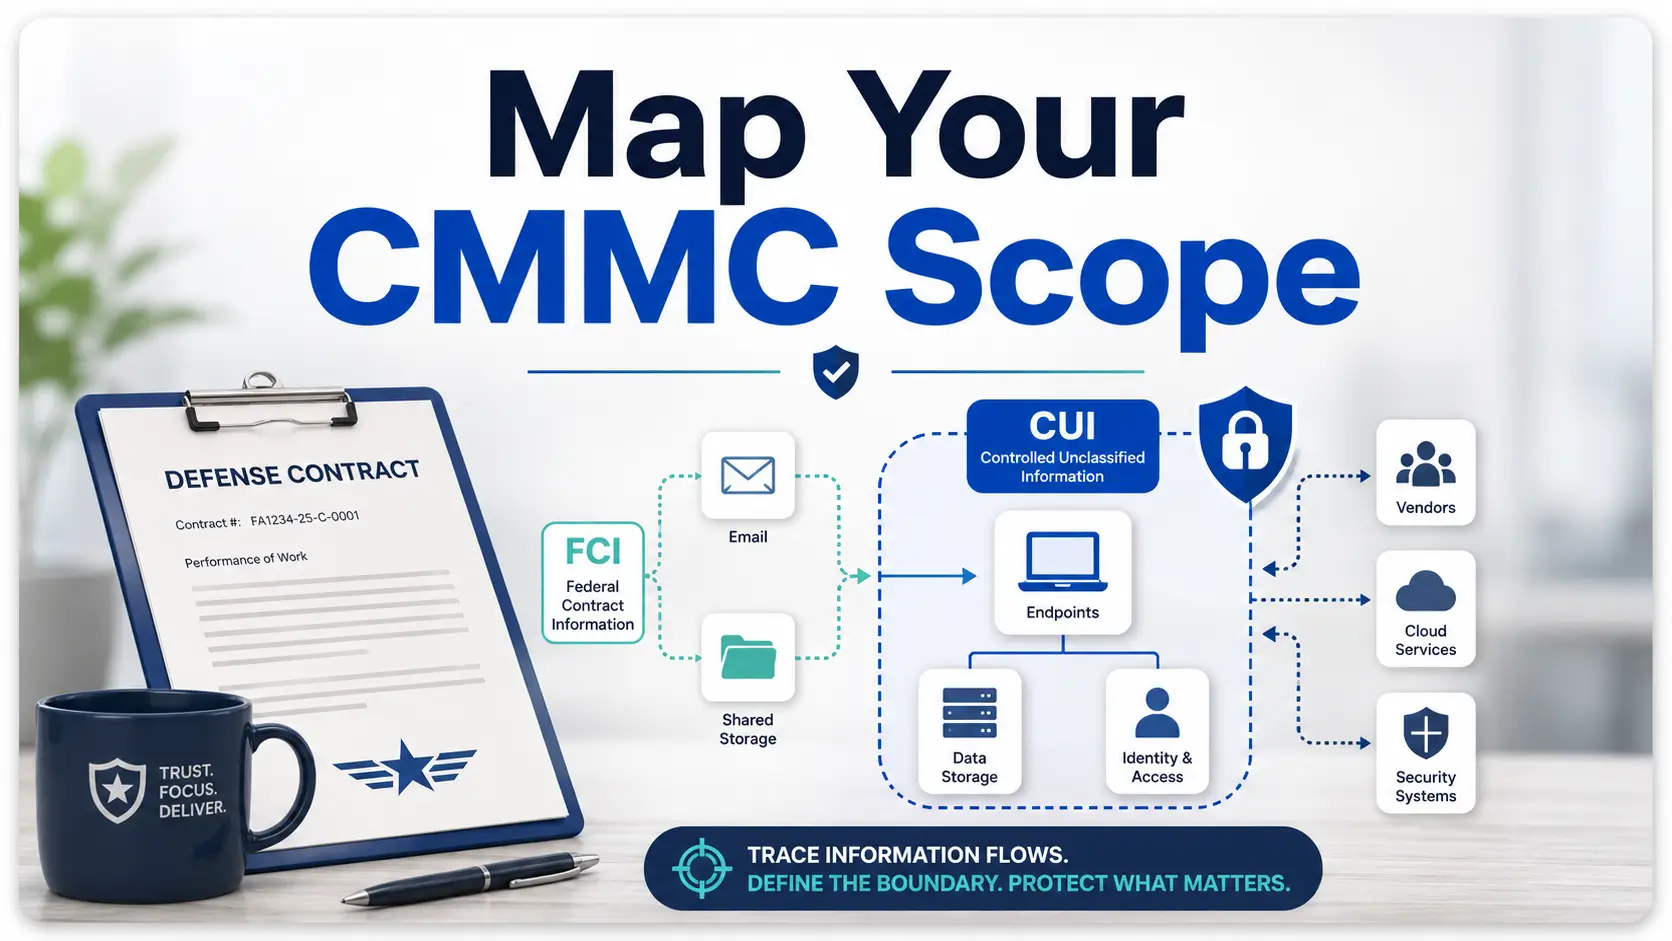
For a small defense contractor, CMMC scope is not automatically the entire company. At Level 1, the core boundary is the contractor information systems that process, store, or transmit Federal Contract Information (FCI). At Level 2, the boundary centers on Controlled Unclassified Information (CUI), but it also reaches security systems, certain connected assets, specialized equipment, … Read more

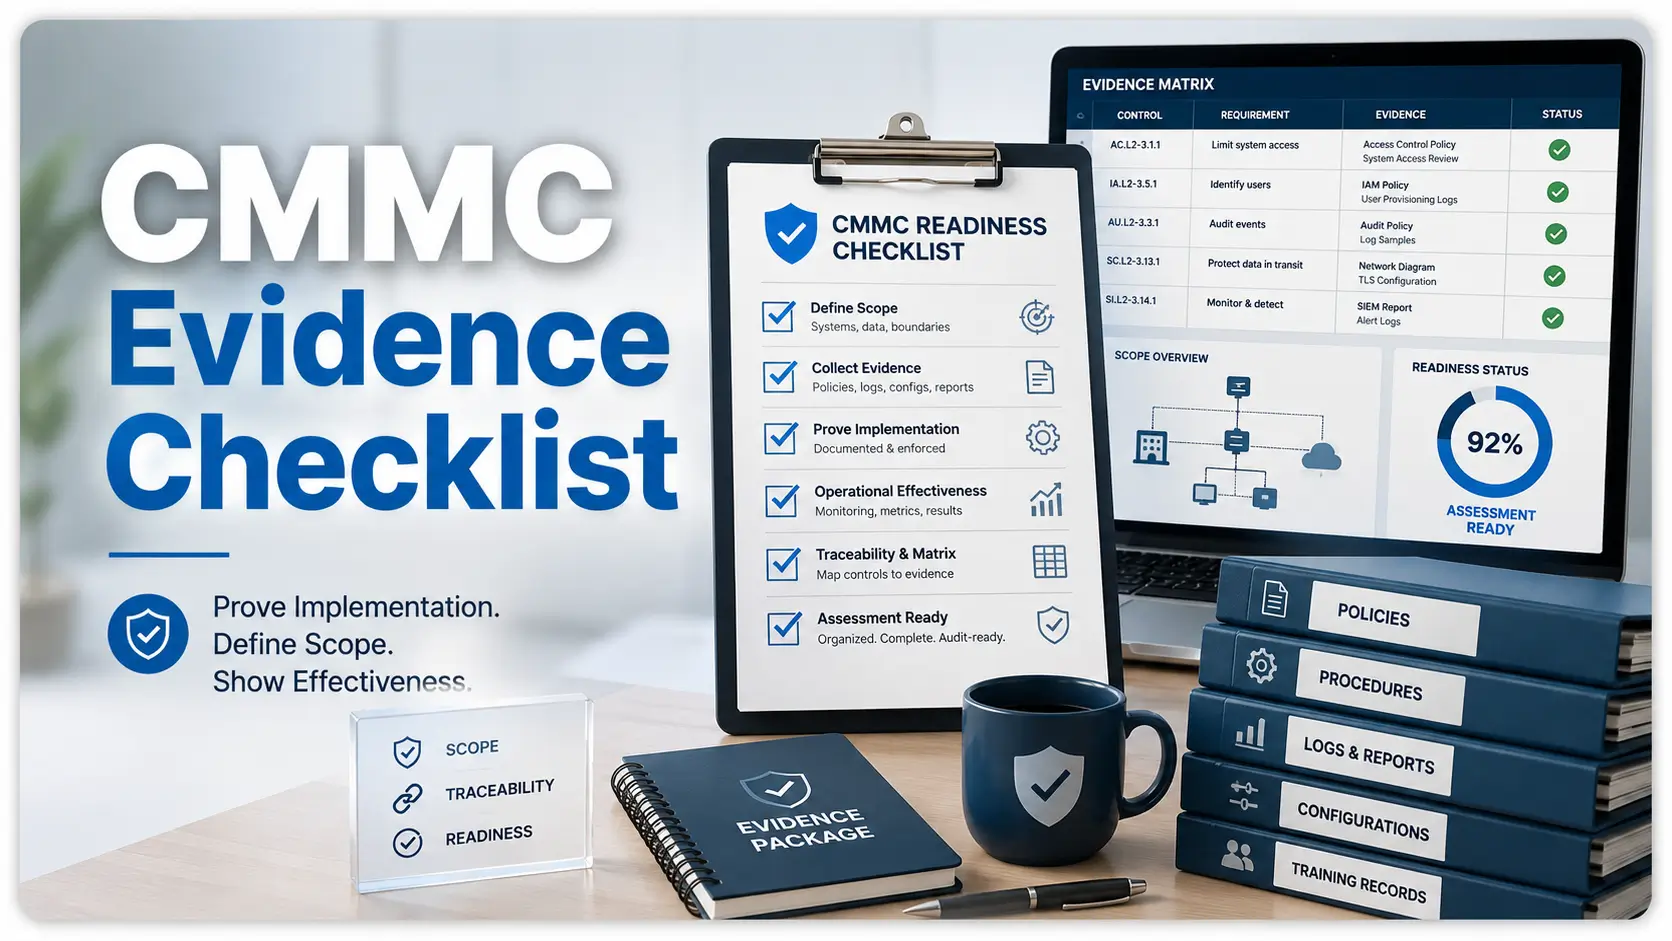
CMMC Evidence Collection Checklist

CMMC evidence collection checklist

Key claims reviewed: October 19, 2026. For Level 2 Self, assessment artifacts are retained for six years from the CMMC Status Date. Level 2 C3PAO assessments additionally require artifact hashing and the prescribed integrity record. This is not a universal six-year rule for every temporary export or a universal screenshot freshness limit. Level 2 Self … Read more