FedRAMP 20x vs Rev5: 7 Essential Checks for Better Planning
Compare FedRAMP 20x and Rev5 paths, check 2026–2027 deadlines, and build a SaaS decision record before commissioning assessment work.
Practical cybersecurity guides, labs & compliance
Compare FedRAMP 20x and Rev5 paths, check 2026–2027 deadlines, and build a SaaS decision record before commissioning assessment work.
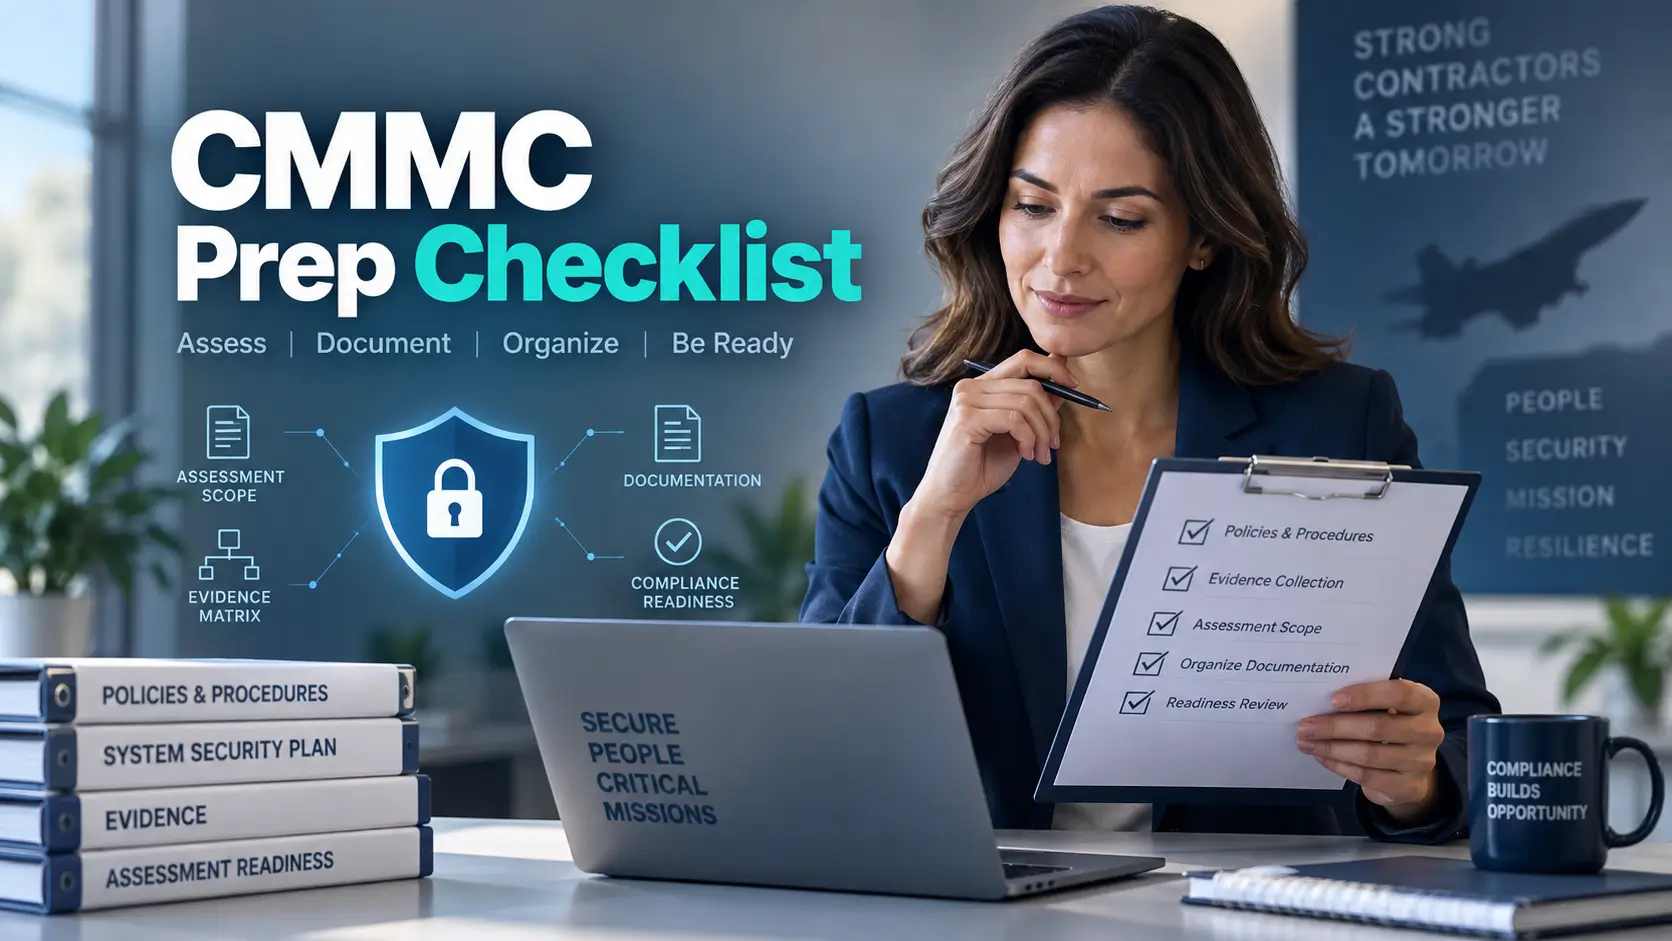
Confirm the assessment your contract requires, define the FCI/CUI boundary, and build an evidence matrix with owners, gaps and next actions. Includes a copyable preparation record and a reminder to check current CMMC program status.
Build a CMMC remediation budget from actual findings, eligible POA&M items and assessment outcomes. Separate engineering, evidence, tooling and assessor costs, and confirm the applicable closeout path before spending.
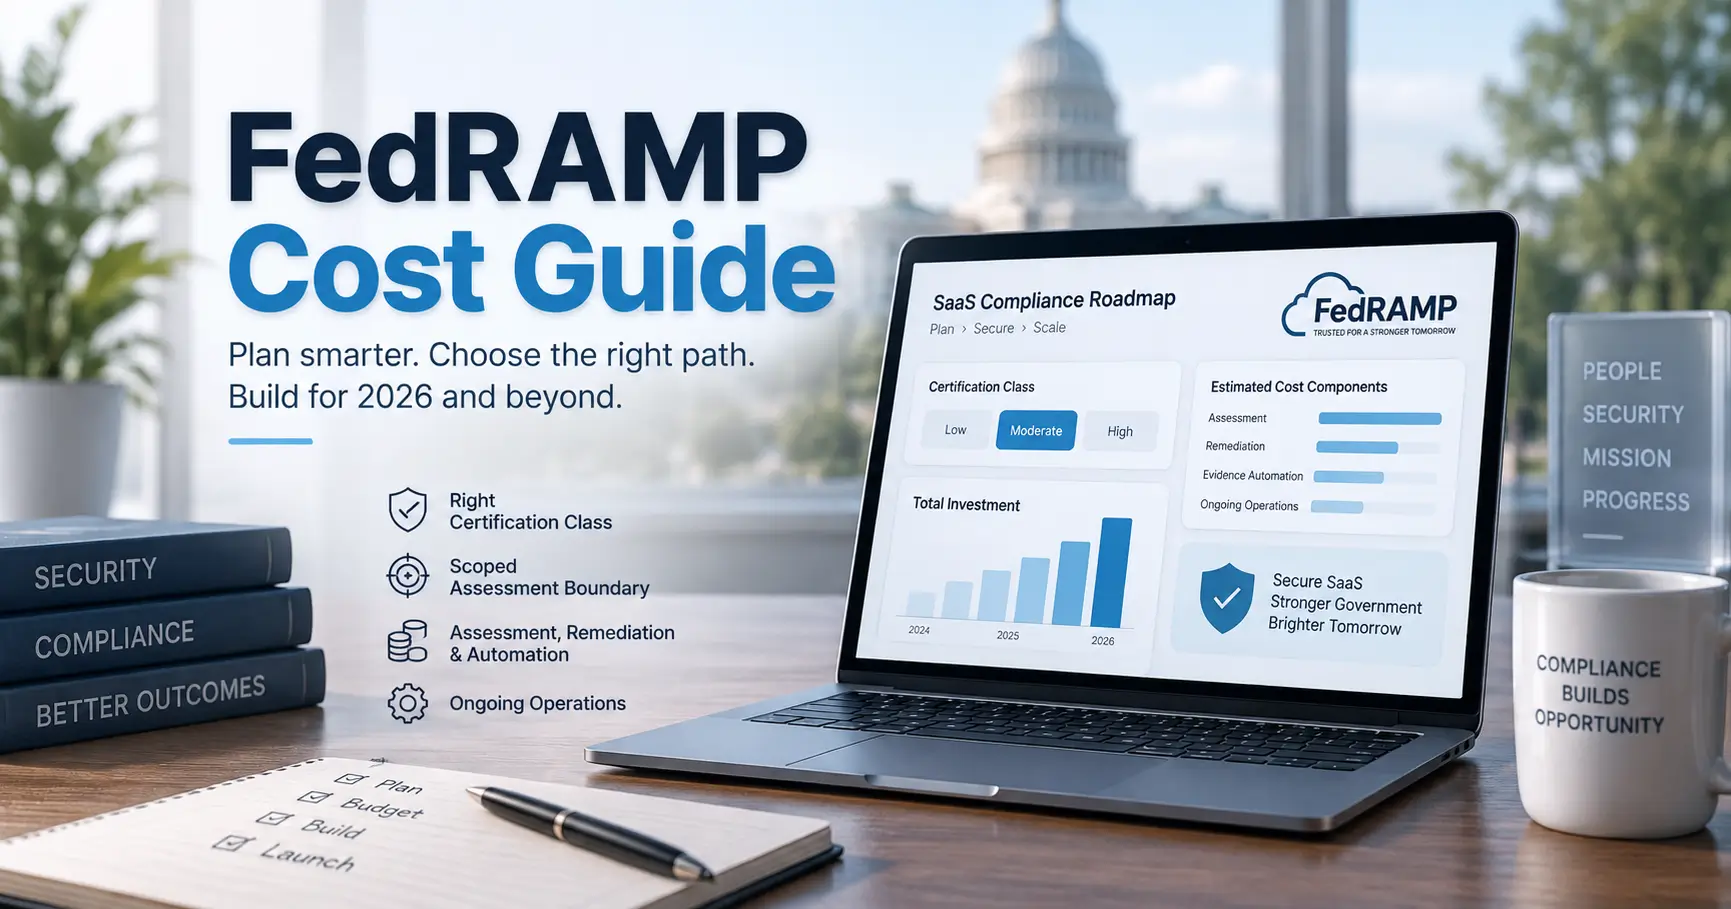
Estimate FedRAMP work from the accepted pathway and service boundary. Compare assessor fees, internal labor, remediation, evidence infrastructure and recurring work, with a checklist for quote exclusions and transition assumptions.
Compare ISO 27001 audit quotations by scope, auditor-days, fees and exclusions. Separate initial certification, surveillance and renewal, and use the working record to track assumptions and questions for certification bodies.
Confirm the PCI DSS validation route with your acquirer, then compare QSA quotations for the same environment. Check assessment scope, evidence readiness, testing, travel and exclusions before treating a quoted fee as the full budget.
Review CUI boundaries, MFA coverage, logging, configuration changes and shared responsibilities. Use the evidence map to connect each applicable control to an owner, implementation, supporting record and unresolved gap.
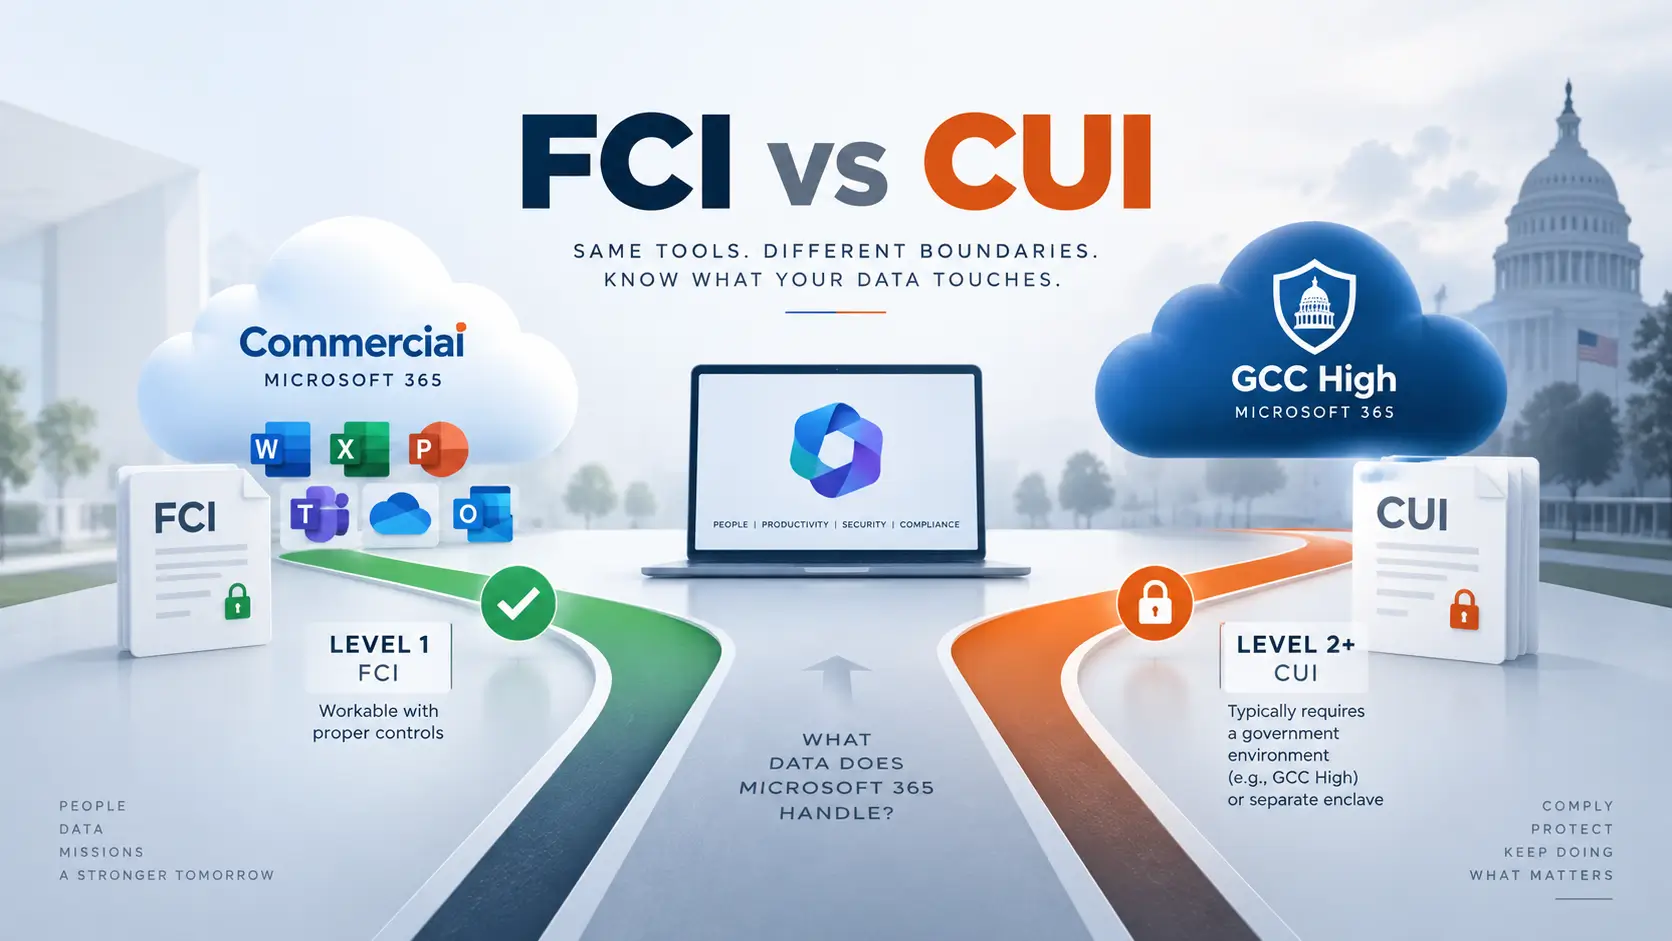
Trace FCI and CUI through Microsoft 365 before comparing Commercial, GCC and GCC High. Review service commitments, customer responsibilities and migration quote inclusions against your actual contract and data flows.
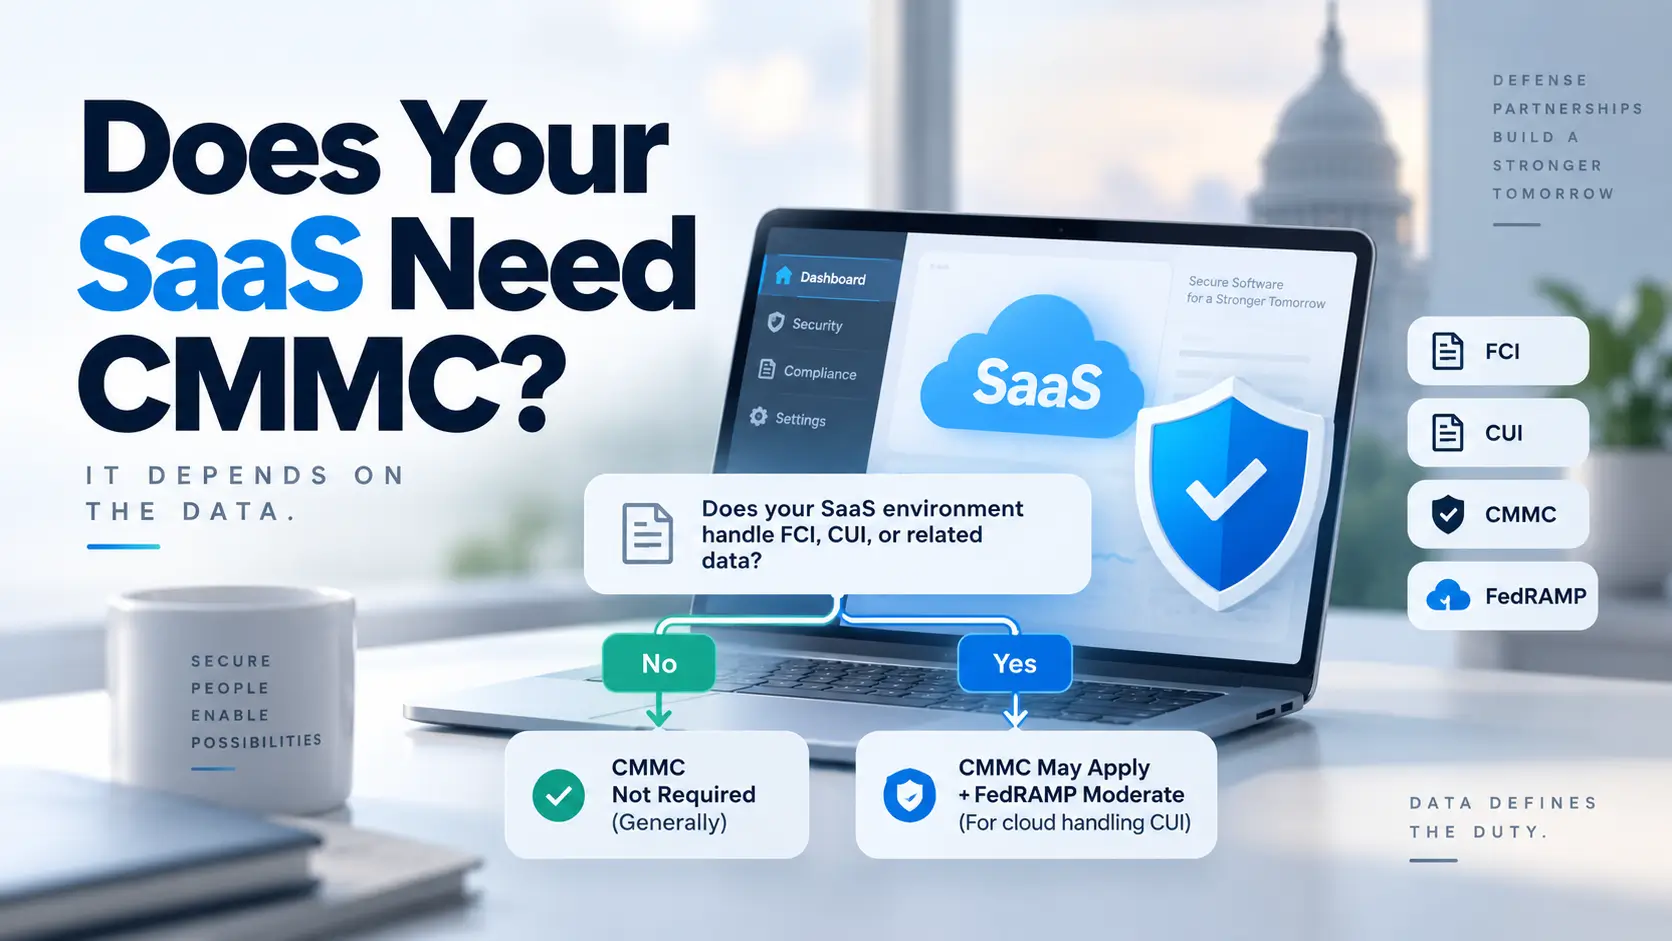
On this page — 15 sections The CMMC Decision Hinge for a SaaS Vendor What Changed in 2026: CMMC Phase II Was Suspended Which CMMC Level Applies to SaaS Vendors? Commercial SaaS Is Not Automatically Exempt If Your SaaS Stores CUI, FedRAMP Becomes a Separate Gate How External Service Providers Enter CMMC Scope The SaaS … Read more
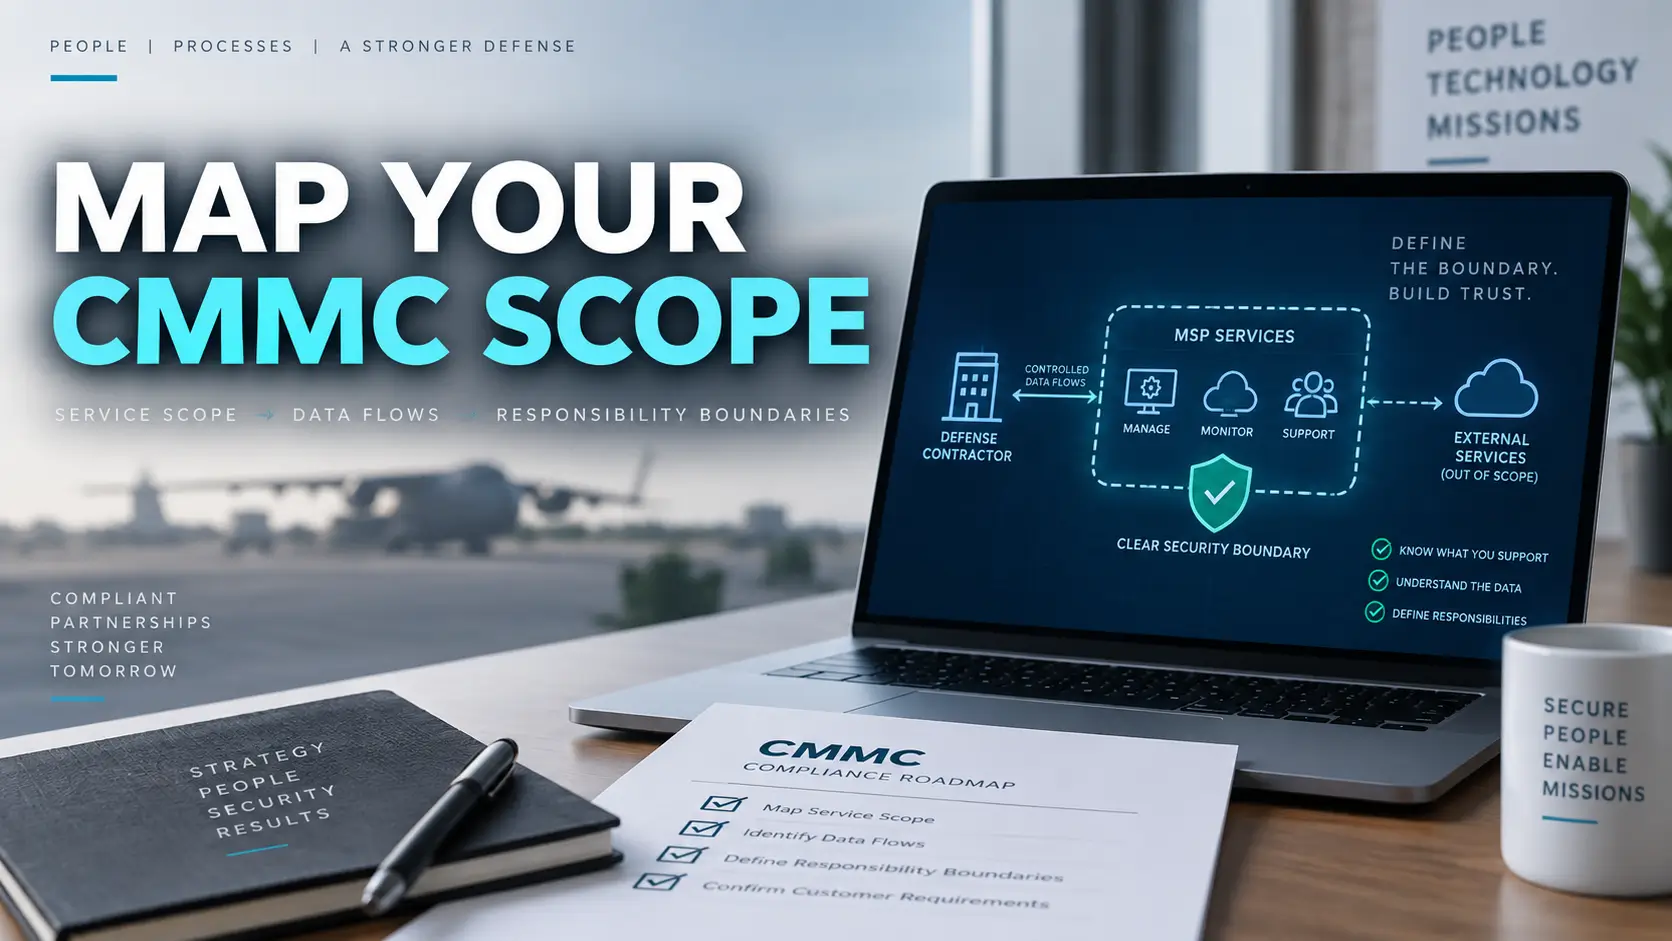
On this page — 15 sections What CMMC Requires From MSPs in 2026 The Decision Hinge: MSP, ESP, or CSP? Does an MSP Need Its Own CMMC Certification? What Level 2 Means for the MSP's Actual Work Build the Customer Responsibility Matrix Before the Assessment The MSP Evidence Package Should Exist Before Anyone Asks for … Read more