Skip to content

Kioptrix Labs

Practical cybersecurity guides, labs & compliance

  • Home
  • Start Here
    • Beginner Roadmap
  • Downloads
    • Level 1 Setup
    • Level 3 Setup
  • About
    • Privacy Policy
    • Terms of Service & Disclaimer
    • Contact
  • Cybersecurity
  • Kali Linux
  • Compliance Guides
    • PCI DSS
  • All Articles

application security

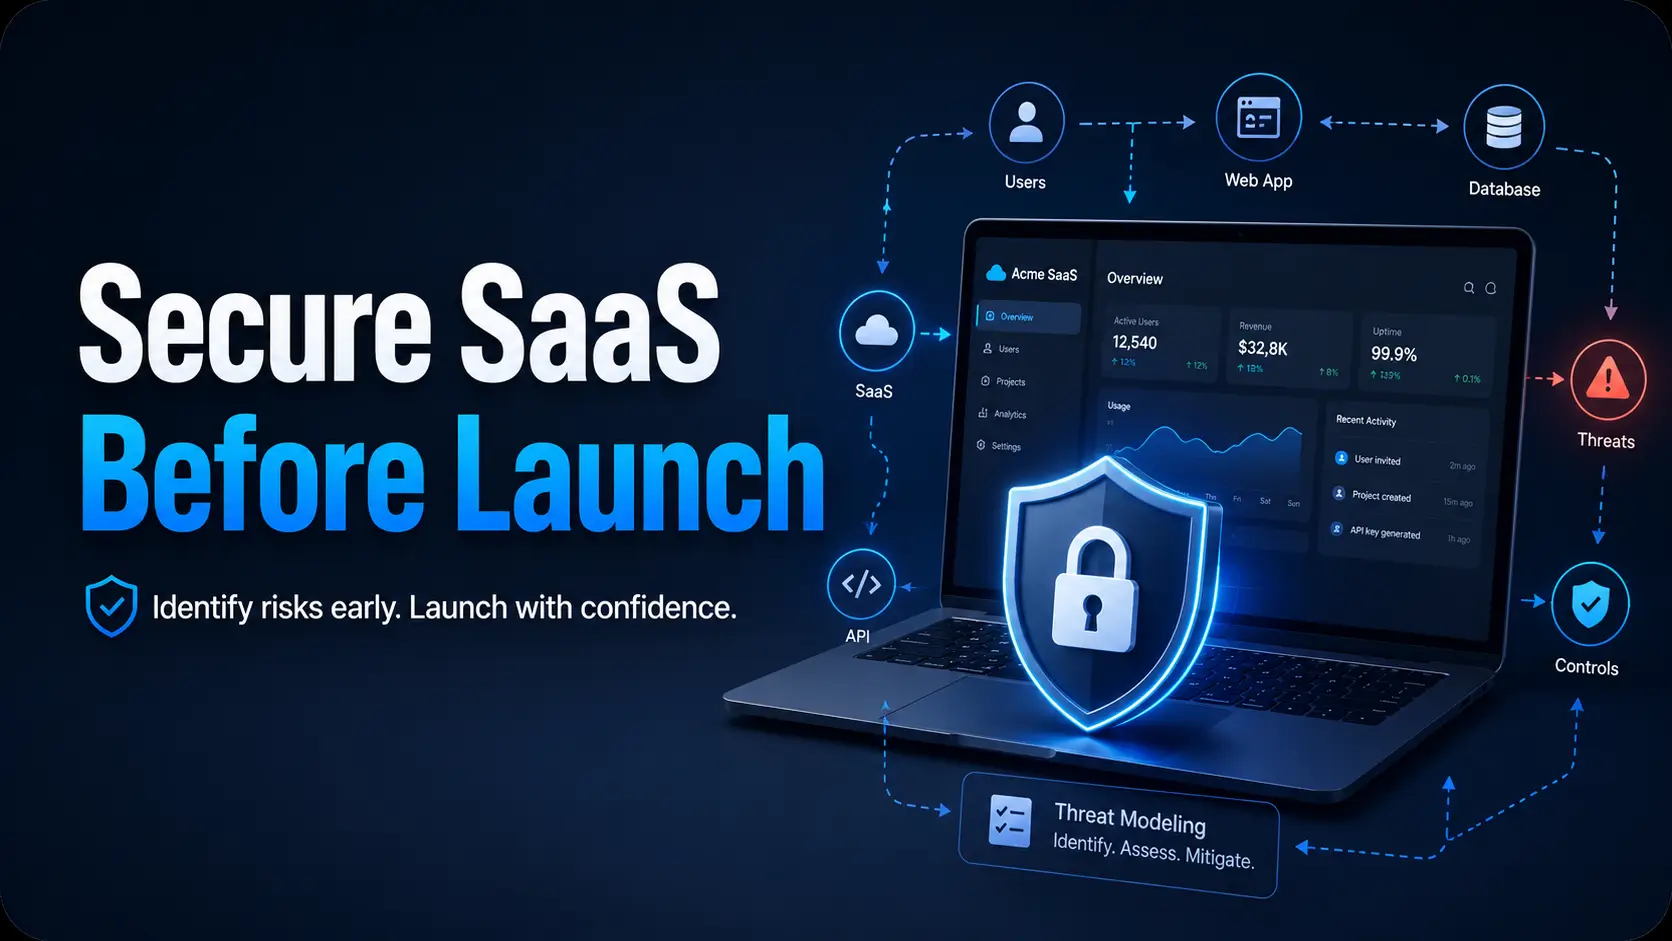
MVP Threat Modeling: Data Flows and Decisions
October 24, 2026September 1, 2026 by Kioptrix Labs
MVP threat modeling for startups

Trace one MVP data flow and its trust boundaries. Use the threat-to-test sheet to turn plausible misuse into mitigation owners, engineering tasks and acceptance checks, while recording assumptions outside the model.

Categories Cybersecurity Tags application security, SaaS security, Startup Cybersecurity, Threat Modeling

SQL Injection Login Bypass: Verify the Lab Claim

October 24, 2026August 24, 2026 by Kioptrix Labs
SQL injection login bypass testing

Evaluate suspected SQL login bypass in a contained, authorized lab. Compare requests and resulting session identity, document the repair, and use the evidence record to separate unusual responses from demonstrated access.

Categories Cybersecurity Tags application security, Cybersecurity Labs, penetration testing, Secure Coding, SQL Injection

Planning Security Testing: Coverage Gaps, Scope and Response Capacity

October 24, 2026February 15, 2026 by Kioptrix Labs
security testing strategy

Choose security testing from the unresolved coverage gap, permitted work and capacity to handle findings. Use the readiness review to compare scanning, pentests and disclosure channels with owners, response terms and retest evidence.

Categories Pentest for Founders Tags application security, bug bounty, cybersecurity, penetration testing

WAF vs RASP vs CSP: Enforcement Layers and Evaluation Criteria

October 24, 2026February 14, 2026 by Kioptrix Labs
WAF vs RASP vs CSP for startups

Compare WAF, RASP and CSP by the failure case, enforcement point and operational owner. Use the acceptance plan to review blocking versus observation, supported environments, false positives, latency and recovery.

Categories Pentest for Founders Tags application security, RASP, startup security, WAF

Burp WebSocket Review: Connection Identity, Messages and Application State

October 24, 2026December 18, 2025 by Kioptrix Labs
Burp Suite WebSocket Workflow

Review WebSocket behavior in Burp with handshake identity, connection context and application state preserved. Use reversible test data and one permitted change to distinguish message delivery from the actual authorization or state outcome.

Categories Pentest for Founders Tags application security, burp suite, penetration testing, websocket repeater, websocket security

Choose your next step

Browse guides by task

Hands-on labs

  • Set up Level 1
  • Fix a VM or network error
  • Choose the next check
  • Walkthrough & hints

Records & projects

  • Copy a lab session note
  • Create a review record
  • Present a learning project

Business security

  • Choose a compliance framework
  • CMMC preparation
  • FedRAMP budgeting

All articles · Author & evidence policy

E-mail:

dalo78@naver.com

  • About
  • All Articles
  • Find a Guide
  • Kioptrix Downloads
  • Kioptrix Level 1 Download & Setup Guide
  • Kioptrix Level 3 Download & Setup Guide
  • Privacy Policy
  • Start Here: Kioptrix Labs, Tools & Security Guides
  • Terms of Service & Disclaimer
© 2026 Kioptrix Labs • Built with GeneratePress