Skip to content

Kioptrix Labs

Practical cybersecurity guides, labs & compliance

  • Home
  • Start Here
    • Beginner Roadmap
  • Downloads
    • Level 1 Setup
    • Level 3 Setup
  • About
    • Privacy Policy
    • Terms of Service & Disclaimer
    • Contact
  • Cybersecurity
  • Kali Linux
  • Compliance Guides
    • PCI DSS
  • All Articles

API security

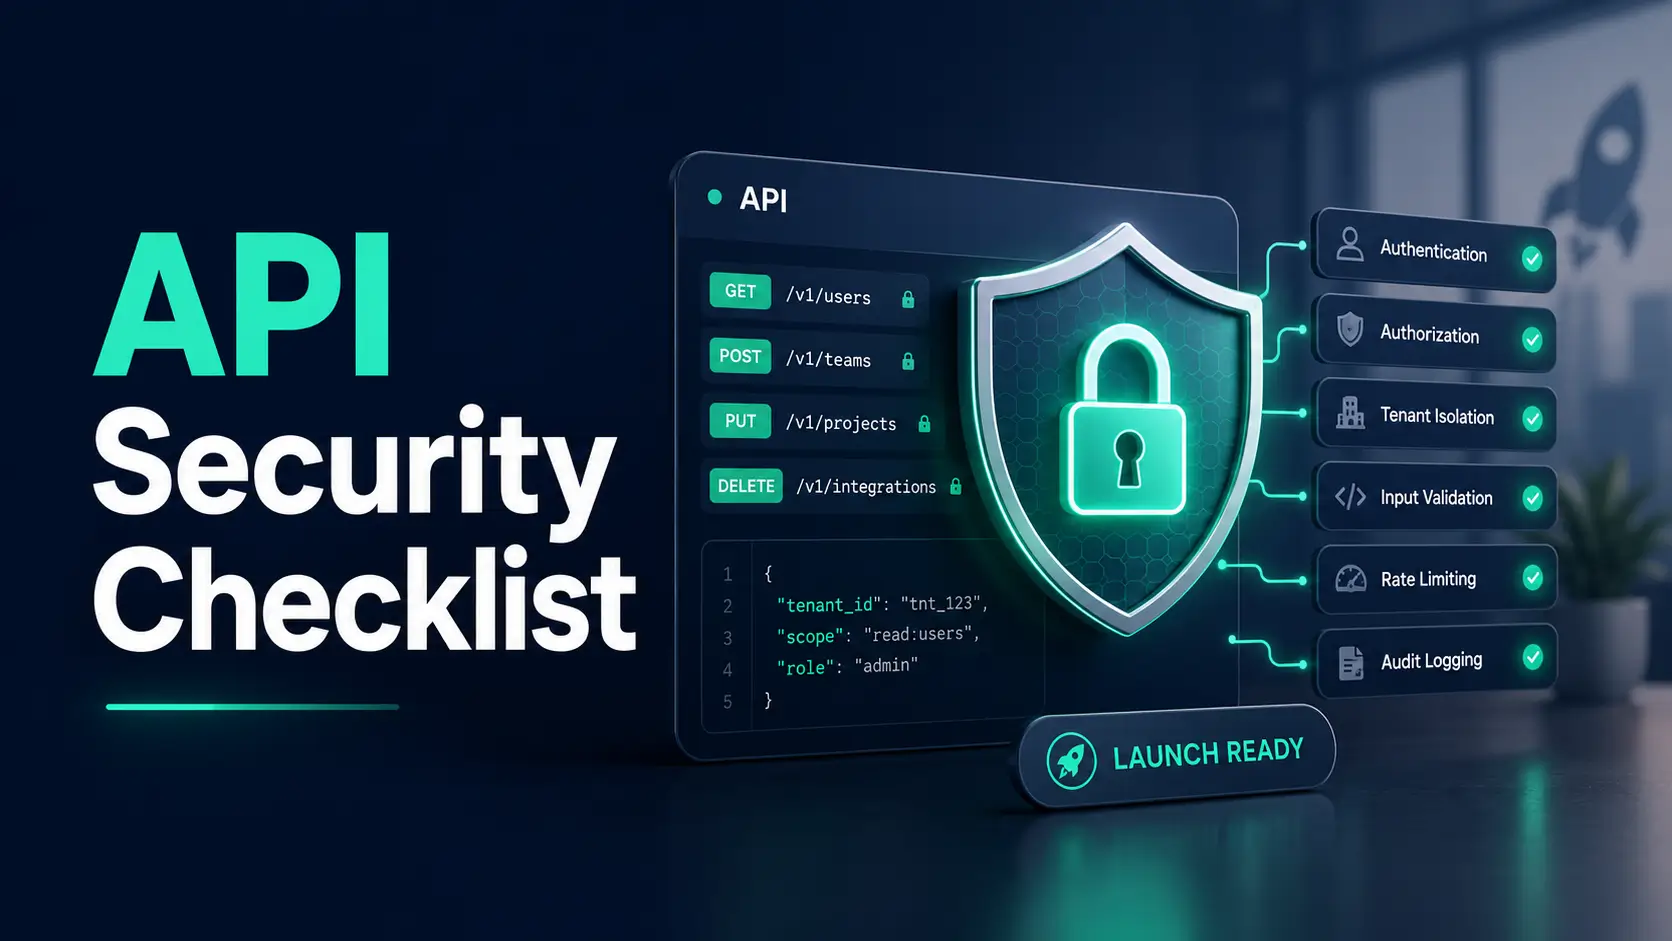
API Security Checklist: Test Authorization Boundaries
October 24, 2026August 30, 2026 by Kioptrix Labs
API security checklist for SaaS founders

Test scoped API authorization across roles, object ownership and tenant boundaries. Use the expectation matrix and two-tenant drill to record allowed and denied operations, supporting evidence and endpoints still unreviewed.
Categories Cybersecurity Tags API security, cybersecurity, penetration testing, SaaS security, Startup Compliance

SaaS API Security: Authentication and Authorization Checks

October 24, 2026February 17, 2026 by Kioptrix Labs
API authentication and authorization for SaaS

Review SaaS API security with a synthetic matrix of tenants, roles, object ownership and actions. Keep token validation separate from server-side authorization, including list, export and background workflows.

Categories Pentest for Founders Tags API security, Authorization, OAuth, SaaS security

MVP Threat Modeling: Flows, Threats, Responses and Validation

October 24, 2026February 10, 2026 by Kioptrix Labs
MVP threat modeling for startups

Create an MVP threat-model record linking data flows and trust boundaries to a threat, chosen response and validation question. Assign owners, retain residual risks and revisit assumptions as the system changes.

Categories Pentest for Founders Tags API security, SaaS, SOC 2, startup security, Threat Modeling

NoSQL Injection Patterns: 7 Checks for Query Types, Tenant Scope and Evidence

October 24, 2026December 5, 2025 by Kioptrix Labs
NoSQL injection patterns

Review NoSQL input from the request parser through the final executed query. Record casting, dropped keys and tenant restrictions separately, and use observed authorization outcomes rather than a rejected payload or unusual response as the conclusion.

Categories Pentest for Founders Tags API security, ethical hacking, MongoDB security, NoSQL injection

Choose your next step

Browse guides by task

Hands-on labs

  • Set up Level 1
  • Fix a VM or network error
  • Choose the next check
  • Walkthrough & hints

Records & projects

  • Copy a lab session note
  • Create a review record
  • Present a learning project

Business security

  • Choose a compliance framework
  • CMMC preparation
  • FedRAMP budgeting

All articles · Author & evidence policy

E-mail:

dalo78@naver.com

  • About
  • All Articles
  • Find a Guide
  • Kioptrix Downloads
  • Kioptrix Level 1 Download & Setup Guide
  • Kioptrix Level 3 Download & Setup Guide
  • Privacy Policy
  • Start Here: Kioptrix Labs, Tools & Security Guides
  • Terms of Service & Disclaimer
© 2026 Kioptrix Labs • Built with GeneratePress