CMMC Requirements for SaaS Vendors
CMMC requirements for SaaS vendors

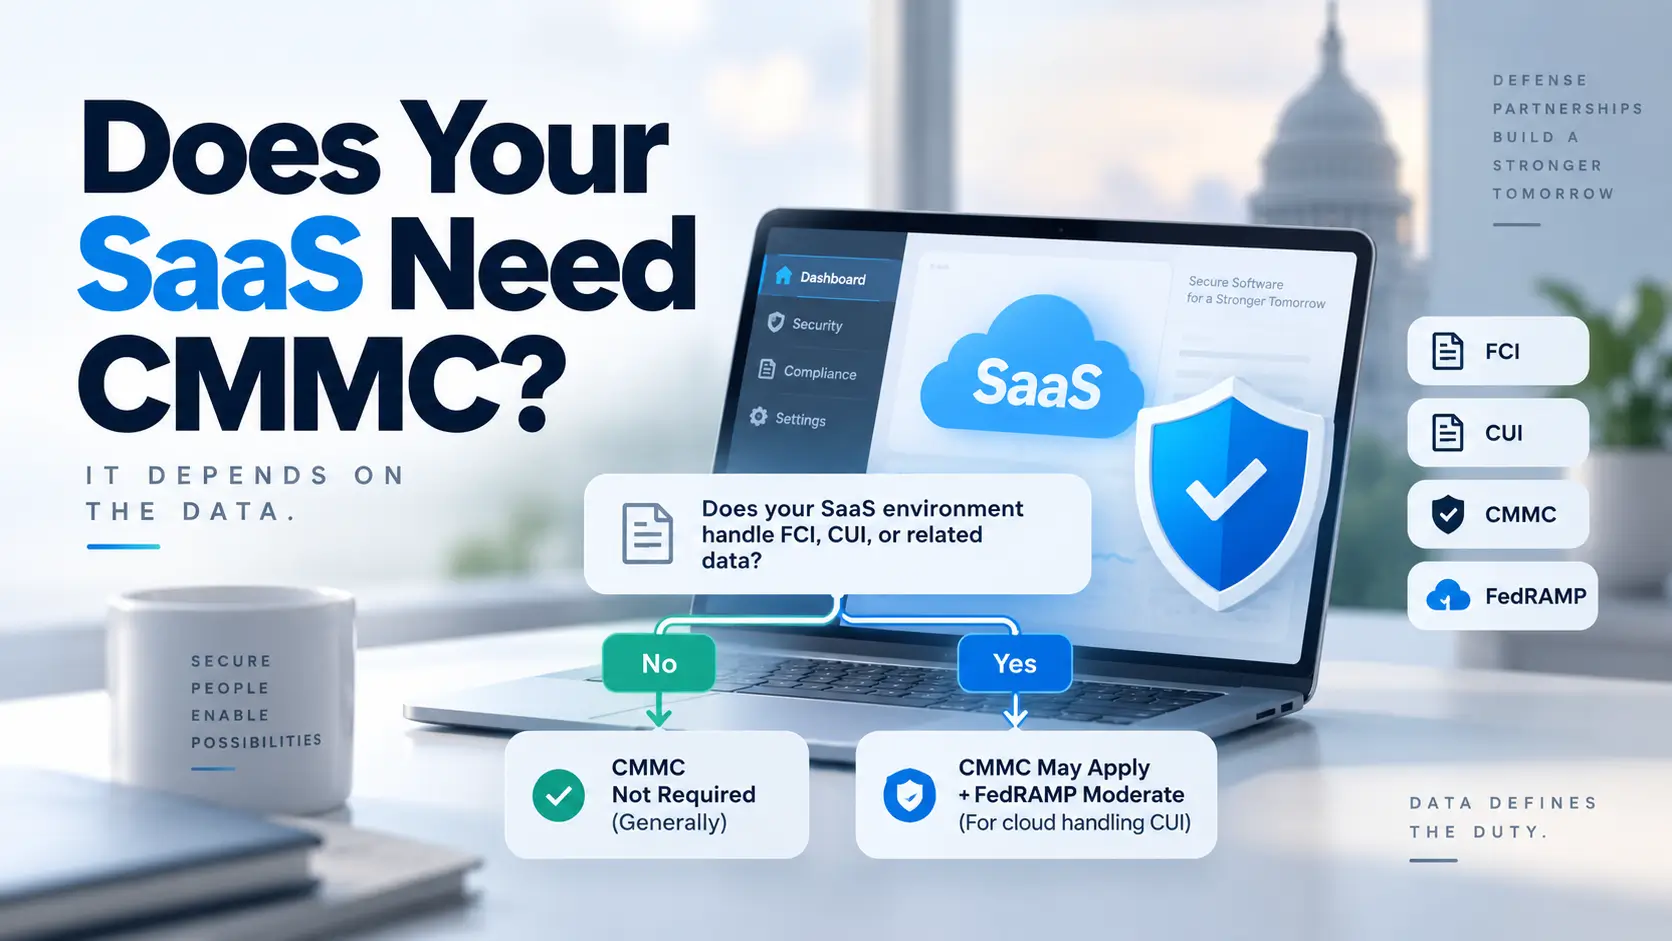
Short answer: a SaaS vendor does not need CMMC simply because it sells software to a defense contractor. The requirement turns on what information the SaaS environment will process, store, or transmit, how the vendor participates in the DoD contract, and what CMMC level the contract or subcontract requires. If your SaaS handles only ordinary … Read more
AWS Security Hub vs GuardDuty for Small Teams: Which One Should You Turn On First?

AWS Security Hub vs GuardDuty

Small-team AWS security guide AWS Security Hub CSPM vs GuardDuty for Small Teams:Which One Should You Turn On First? For a small AWS team, the hardest security decision is rarely “Which service has more features?” It is usually quieter and more annoying: “Which alert will someone actually read at 4:37 p.m. on a Tuesday, between … Read more

Cloud Misconfiguration Top 10 (AWS/GCP): The Settings That Actually Trigger Real Incidents

cloud misconfigurations

Cloud Misconfigurations: The Real Anatomy of a Breach Most cloud breaches don’t start with zero-days. They start with a storage bucket someone thought was “internal,” an IAM wildcard added during a release crunch, or a service account key that never expired. If you’re running AWS or GCP at speed, cloud misconfiguration isn’t a theoretical risk—it’s … Read more

Secrets Management 101 for Startups: The Minimum Setup to End .env Hell

startup secrets management

From .env Hell to Controlled Operations: A Pragmatic Secrets Management Guide Most startups don’t get burned by sophisticated attacks first—they get burned by convenience. A production token copied into chat, a screenshot with one unblurred corner, or a “temporary” .env file that quietly becomes permanent. That’s how secrets management turns from a developer shortcut into … Read more