GCC vs GCC High: Match Data and Contract Requirements
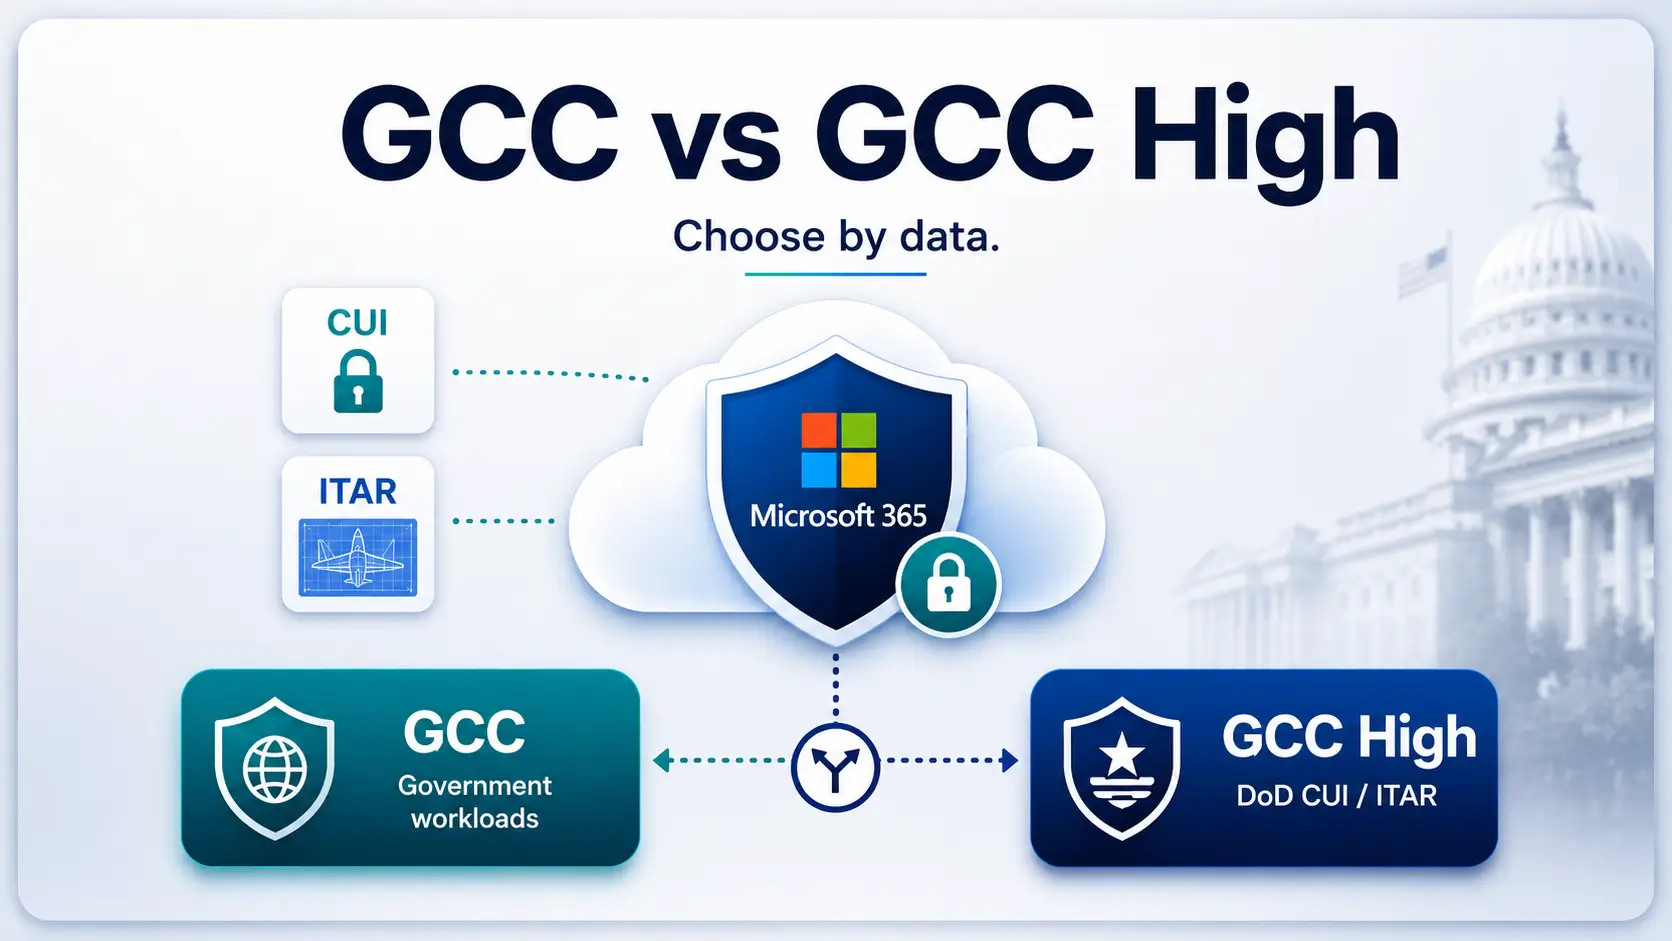
Compare Microsoft 365 GCC and GCC High for defense work. Start with your data types, contract requirements, migration needs, and operating responsibilities.
Practical cybersecurity guides, labs & compliance
Compare Microsoft 365 GCC and GCC High for defense work. Start with your data types, contract requirements, migration needs, and operating responsibilities.
Compare five CMMC software candidates using the same requirement, evidence update and export. Separate advertised capabilities from demonstrated results, and check packages, add-ons, staff responsibilities and exit costs before buying.
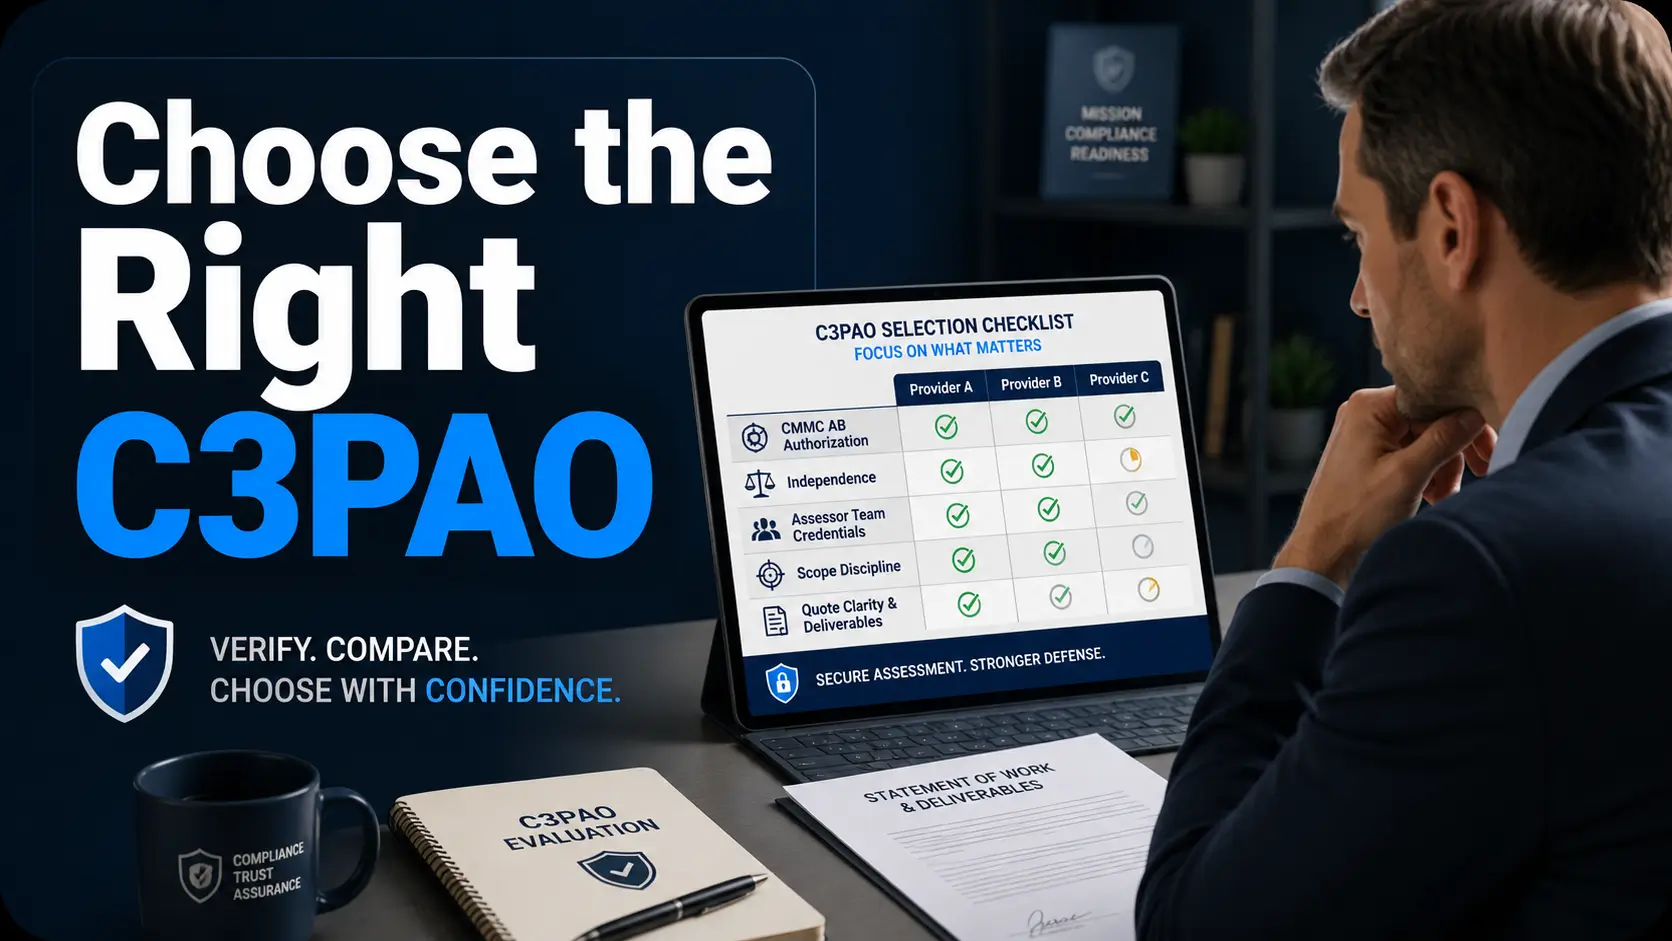
Verify whether a C3PAO engagement is required, then compare eligibility, independence, named personnel, scope and quote terms. Use the evidence record to keep proposed commitments and unresolved questions visible before choosing a provider.
Separate a C3PAO assessor quote from internal assessment work, readiness and remediation. Understand the limits of the government’s historical cost model, then compare provider scope, expenses, exclusions and possible closeout work.
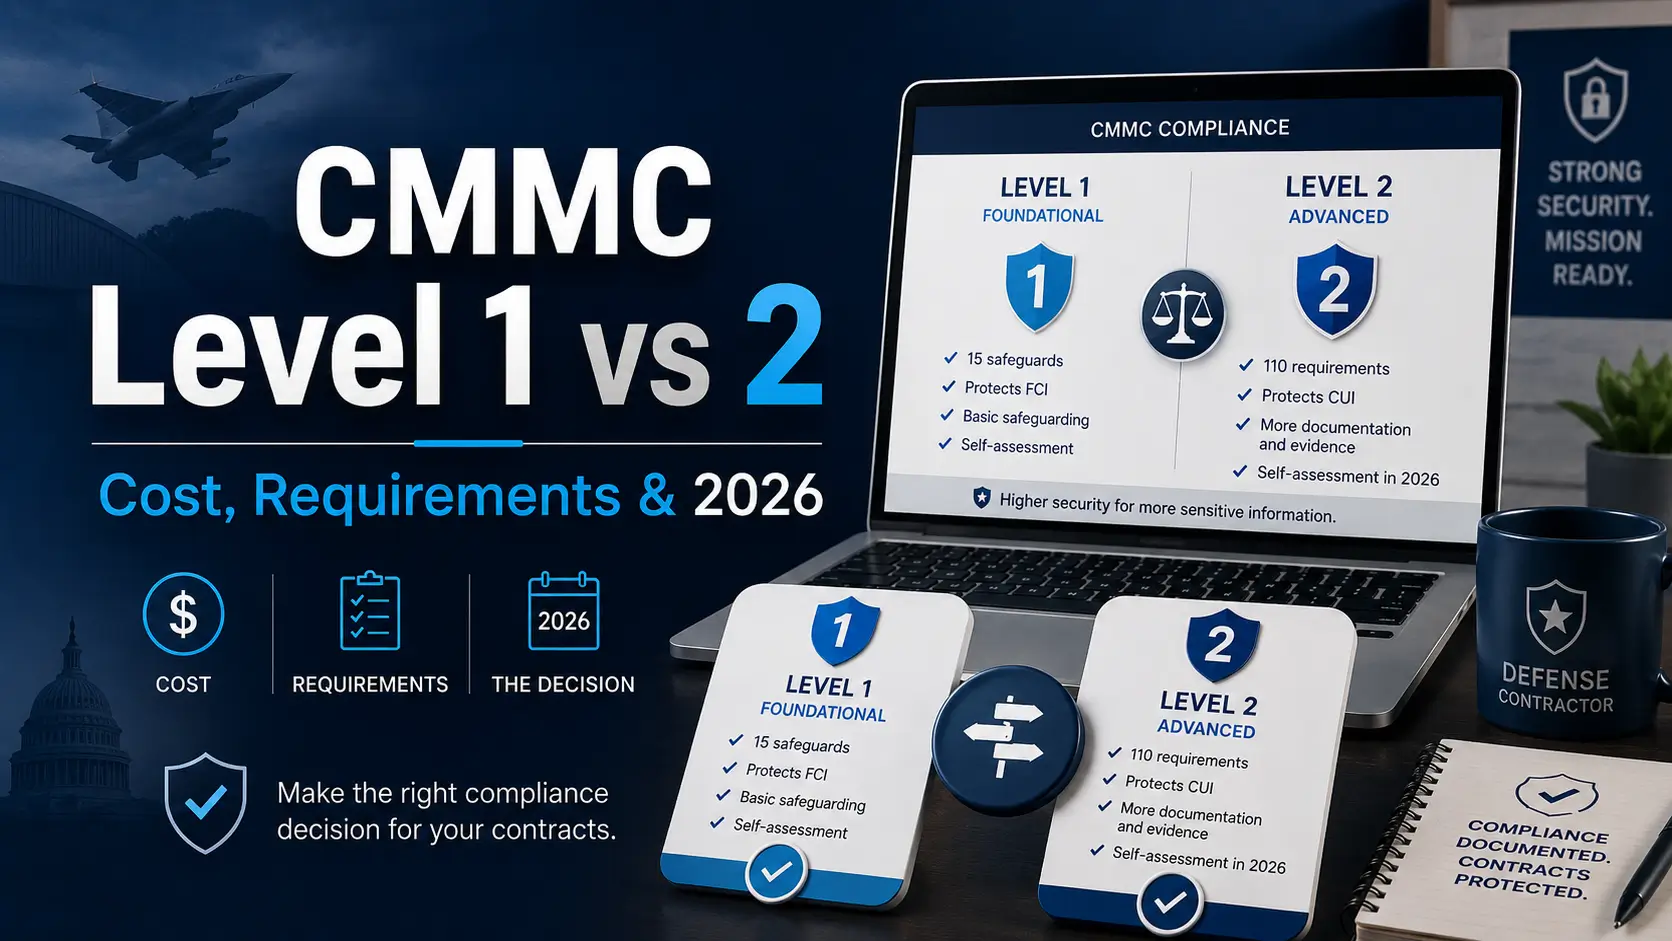
Compare CMMC Level 1 and Level 2 through your contract, FCI/CUI data flows and system boundary. Separate implementation, evidence and assessment work before choosing a budget or commissioning outside help.
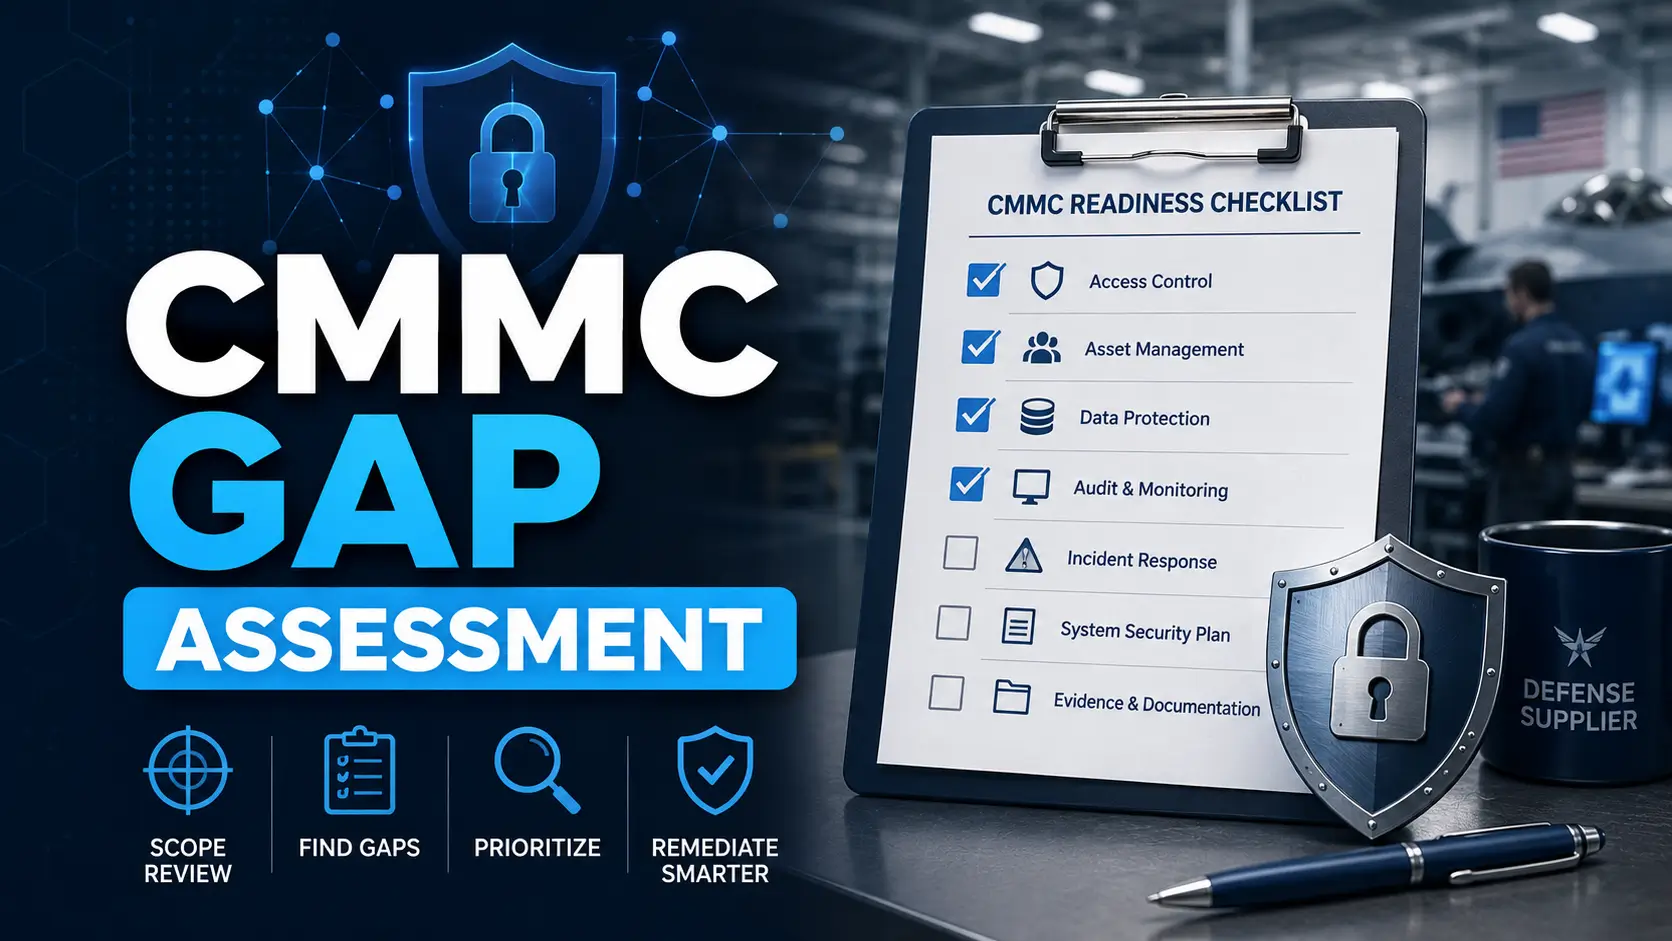
Define the assessment boundary, compare applicable requirements with implemented controls, and record gaps in evidence, coverage and ownership. Use the checklist to assign remediation actions without treating a readiness label as official CMMC status.
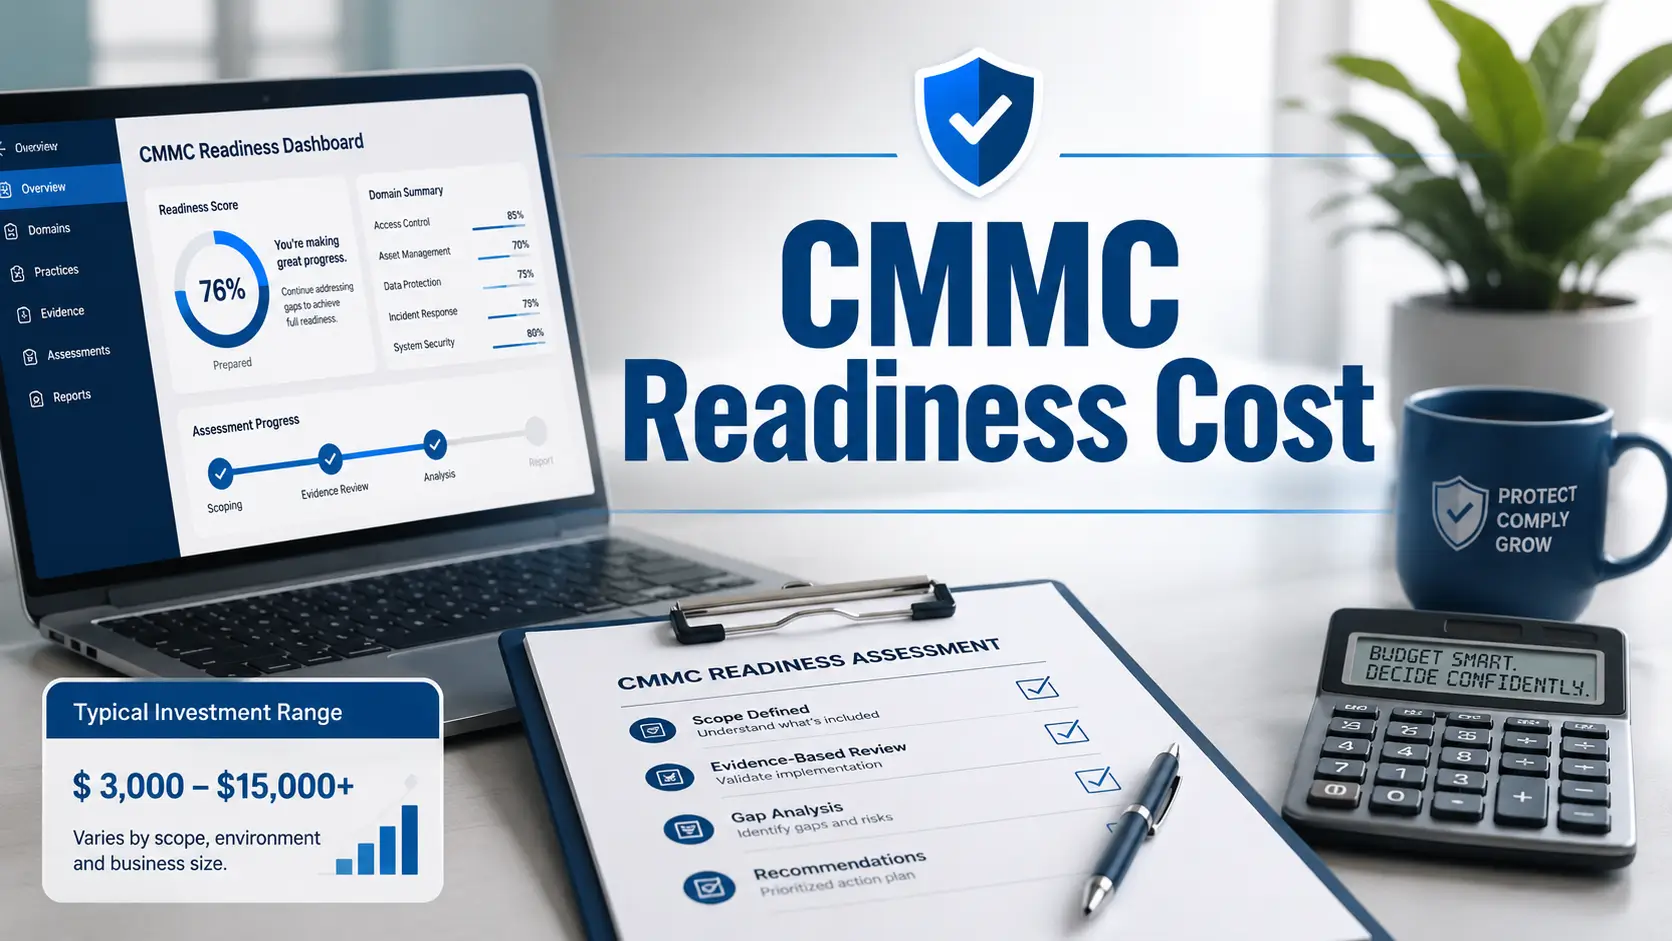
Compare what a CMMC readiness assessment actually includes: scope discovery, interviews, evidence testing, SSP review and remediation planning. Record exclusions and completion criteria before comparing fees; preparation work does not create official status.
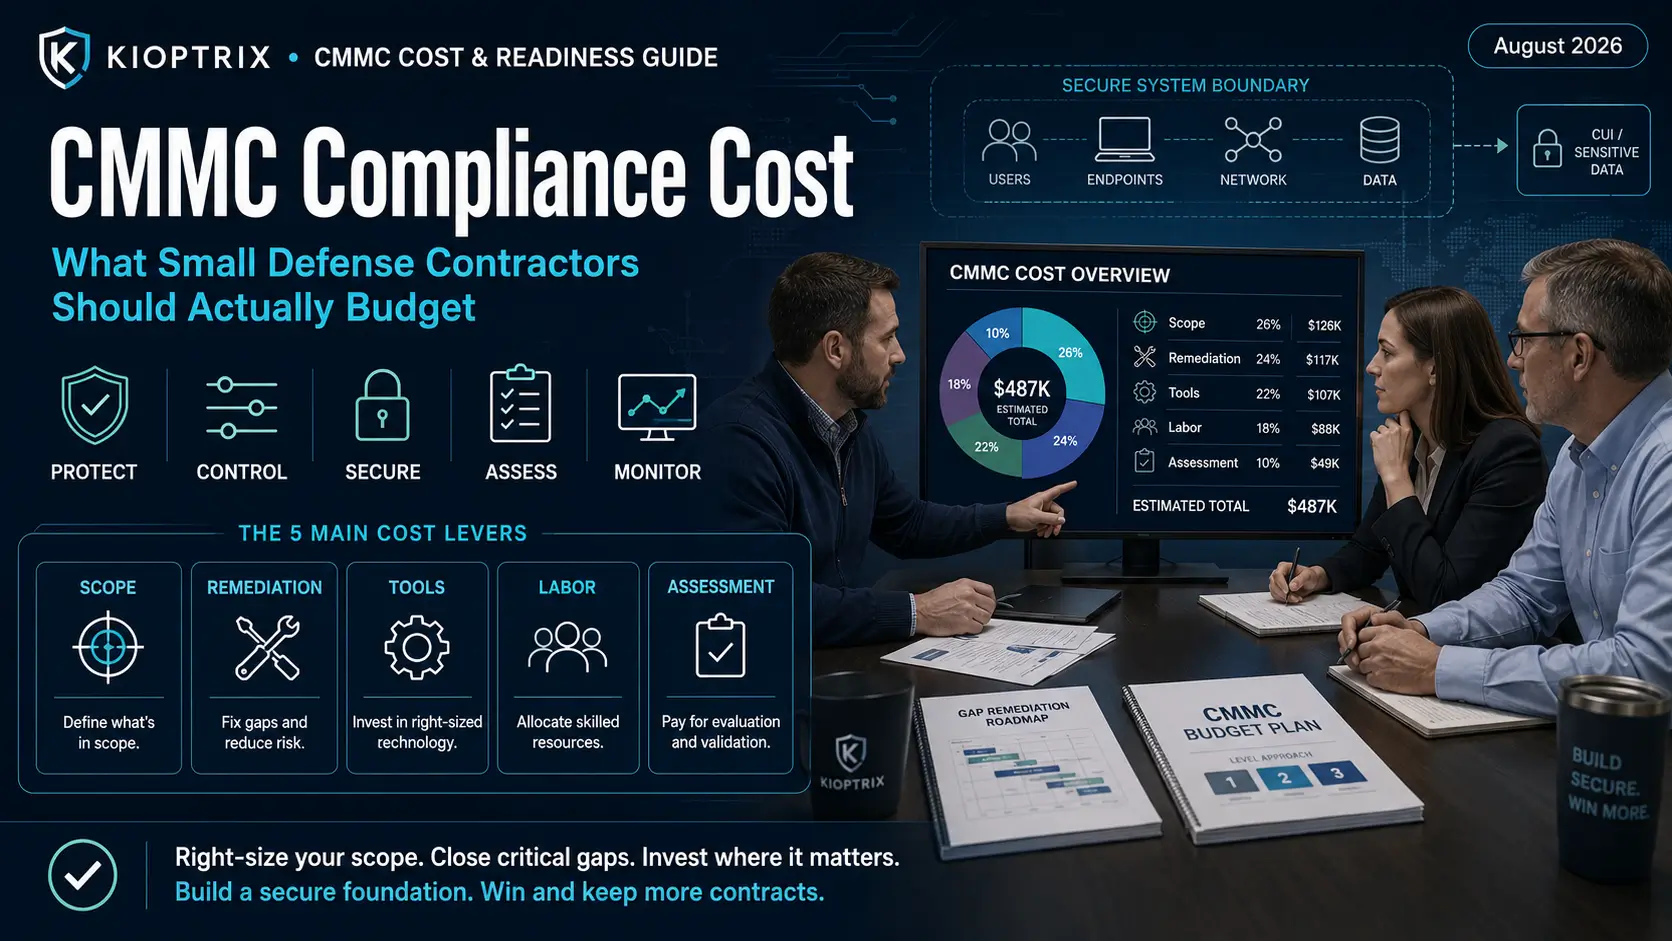
Build a CMMC budget from the actual contract, scope and assessment path. Separate historical government models, supplier quotes, remediation, internal capacity and recurring costs.