Skip to content

Kioptrix Labs

Practical cybersecurity guides, labs & compliance

  • Home
  • Start Here
    • Beginner Roadmap
  • Downloads
    • Level 1 Setup
    • Level 3 Setup
  • About
    • Privacy Policy
    • Terms of Service & Disclaimer
    • Contact
  • Cybersecurity
  • Kali Linux
  • Compliance Guides
    • PCI DSS
  • All Articles

SaaS security

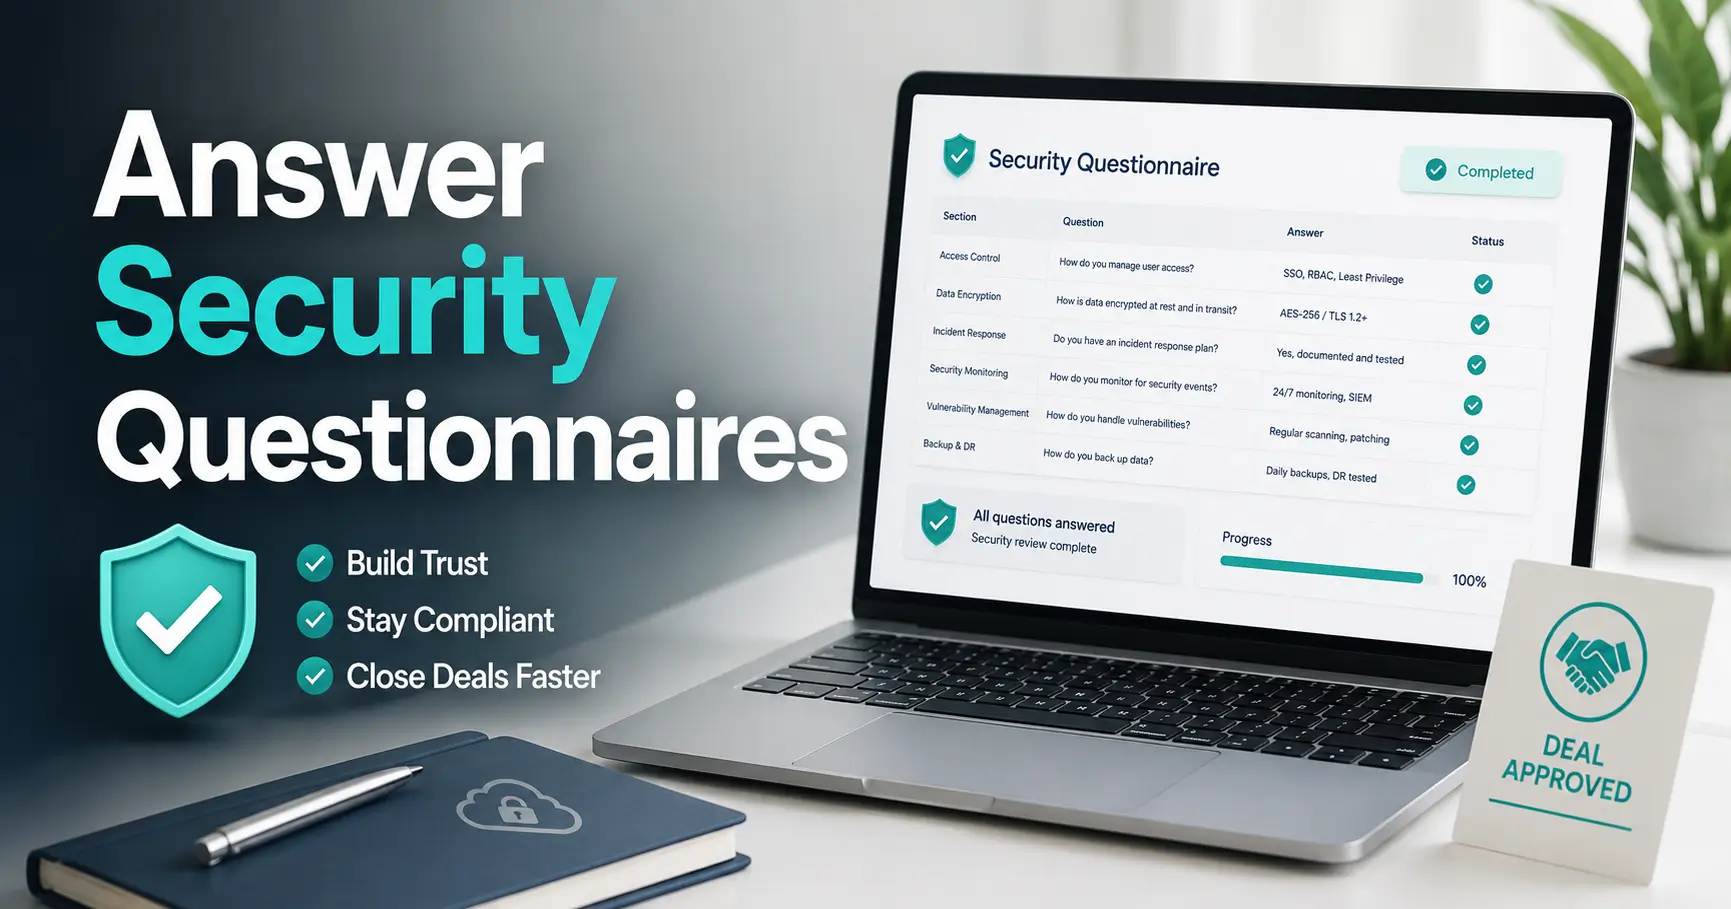
Answer Customer Security Questionnaires Accurately
October 24, 2026August 23, 2026 by Kioptrix Labs
customer security questionnaire

Prepare scoped customer security answers with approved evidence. Distinguish current capabilities from plans, qualify partial coverage, and use the approval record and contradiction review before making a customer commitment.
Categories Cybersecurity Tags cybersecurity tools, enterprise sales, SaaS security, Security Compliance, Vendor Risk Management

Vendor Security Questionnaire Template: Evidence First

October 24, 2026August 22, 2026 by Kioptrix Labs
Vendor security questionnaire template

Assess a vendor for the service and data access you intend to use. Adapt the questionnaire, link each claim to dated evidence, and complete the review decision card with owners, exceptions and follow-up actions.

Categories Cybersecurity Tags Cybersecurity Compliance, SaaS security, Third-Party Risk, Vendor Risk Management

SOC 2 Type 1 vs Type 2: Which Report Do Buyers Need?

October 24, 2026August 20, 2026 by Kioptrix Labs
SOC 2 Type 1 vs Type 2

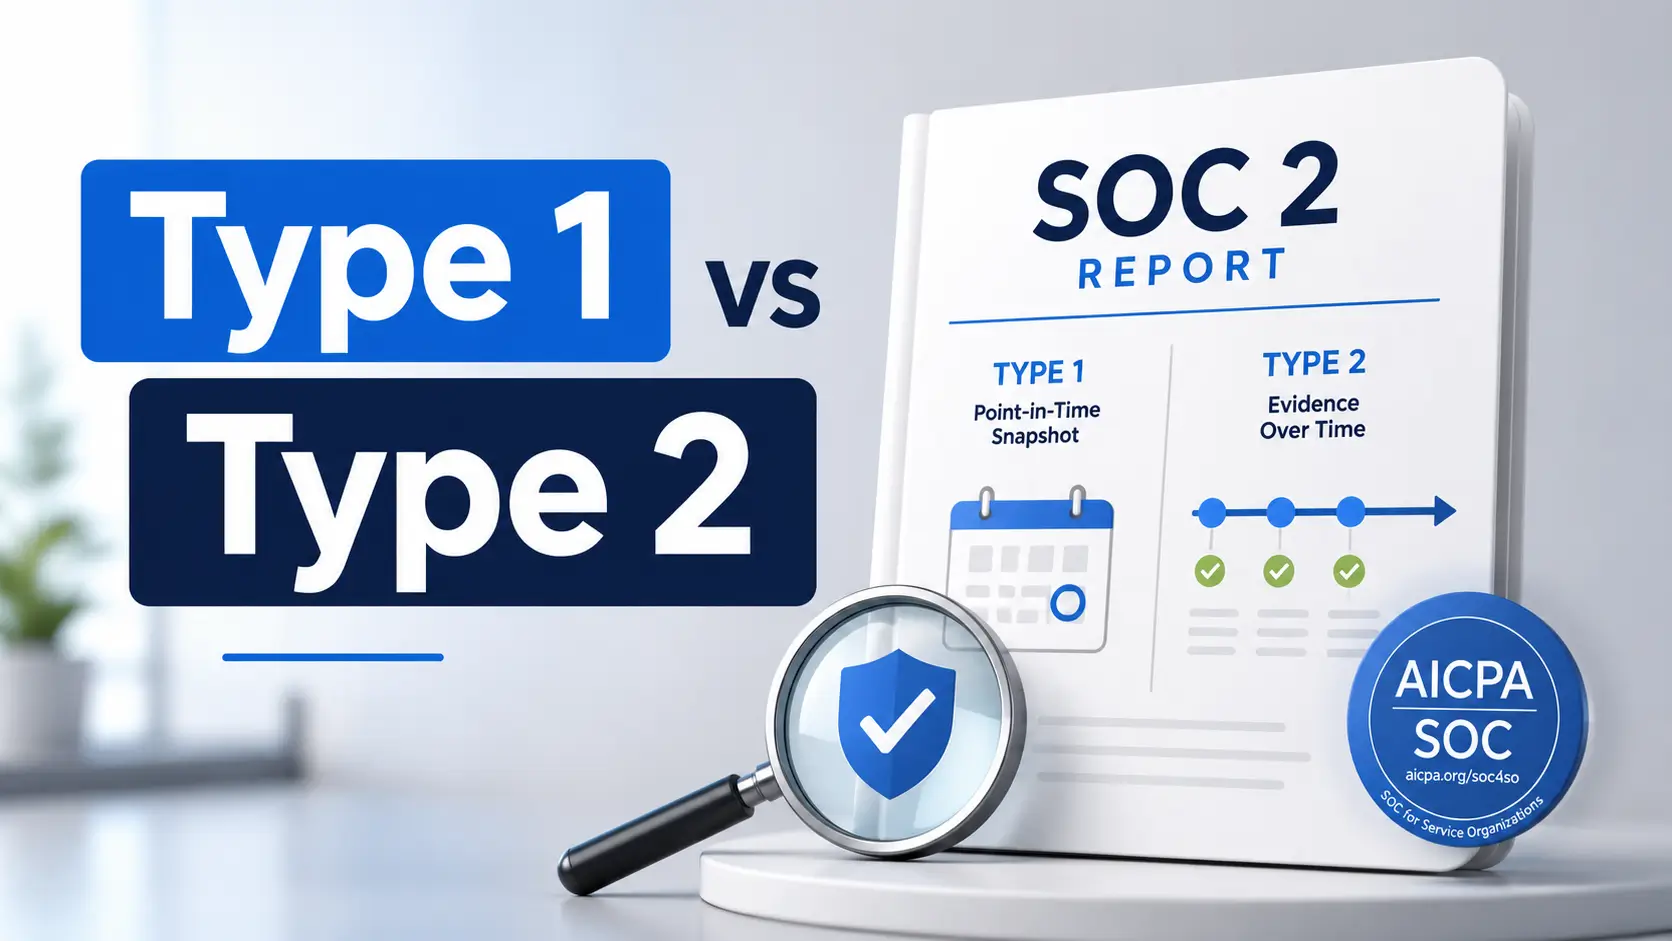
Compare a SOC 2 report with your actual buying requirement. Review scope, date or period, opinion and exceptions, then use the acceptance record to document missing evidence and follow-up questions.

Categories Cybersecurity Tags Cybersecurity Audits, SaaS security, SOC 2 Compliance, Vendor Risk Management

SOC 2 Policy Checklist for Startups: Scope, Owners and Evidence

October 24, 2026July 25, 2026 by Kioptrix Labs
SOC 2 policies for startups

Map startup security policies to the actual service, owners and operating evidence. Use the policy-readiness matrix and acceptance record to track revisions, implementation gaps and the next review action.

Categories Cybersecurity Tags Audit Readiness, SaaS security, SOC 2 Compliance, Startup Operations

SaaS Acceptable Use Policy: Scope and Enforcement

October 24, 2026July 24, 2026 by Kioptrix Labs
SaaS acceptable use policy template

Draft a SaaS acceptable-use policy that matches your service and enforcement process. Use the gap test and enforcement map to connect restrictions with abuse reporting, case review, escalation and accountable owners.

Categories Cybersecurity Tags SaaS Legal, SaaS security, Startup Compliance, Trust and Safety

Vulnerability Disclosure Intake: Reporting Routes and Policy Review

October 24, 2026February 21, 2026 by Kioptrix Labs
Vulnerability Disclosure Policy

Prepare vulnerability-disclosure intake with a monitored reporting route, an owner and a publication review. Use the record to separate contact-file checks from policy scope, response commitments and authorization to test.

Categories Practice Labs & Tools Tags cybersecurity, SaaS security, security.txt, vulnerability disclosure

How to Read a Pentest Report: Evidence and Next Actions

October 24, 2026February 20, 2026 by Kioptrix Labs
how to read a penetration test report

Read a penetration-test finding through affected assets, evidence, prerequisites and confidence. Use the action card to separate demonstrated impact from assumptions, assign an owner and define a remediation acceptance check.

Categories Pentest for Founders Tags cybersecurity, enterprise sales, penetration testing, risk management, SaaS security

SaaS API Security: Authentication and Authorization Checks

October 24, 2026February 17, 2026 by Kioptrix Labs
API authentication and authorization for SaaS

Review SaaS API security with a synthetic matrix of tenants, roles, object ownership and actions. Keep token validation separate from server-side authorization, including list, export and background workflows.

Categories Pentest for Founders Tags API security, Authorization, OAuth, SaaS security

Security Headers: CSP Enforcement, HSTS Readiness and Rollout Checks

October 24, 2026February 13, 2026 by Kioptrix Labs
security headers ROI

Review security headers through the effective policy, browser behavior and legitimate application flows. Use the rollout record to separate CSP reporting from enforcement and track HSTS readiness, compatibility and recovery.

Categories Pentest for Founders Tags content security policy, cybersecurity ROI, HSTS, SaaS security, security headers
Newer posts
← Previous Page1 Page2

Choose your next step

Browse guides by task

Hands-on labs

  • Set up Level 1
  • Fix a VM or network error
  • Choose the next check
  • Walkthrough & hints

Records & projects

  • Copy a lab session note
  • Create a review record
  • Present a learning project

Business security

  • Choose a compliance framework
  • CMMC preparation
  • FedRAMP budgeting

All articles · Author & evidence policy

E-mail:

dalo78@naver.com

  • About
  • All Articles
  • Find a Guide
  • Kioptrix Downloads
  • Kioptrix Level 1 Download & Setup Guide
  • Kioptrix Level 3 Download & Setup Guide
  • Privacy Policy
  • Start Here: Kioptrix Labs, Tools & Security Guides
  • Terms of Service & Disclaimer
© 2026 Kioptrix Labs • Built with GeneratePress