Vulnerability Retesting: 5 Essential Checks for Better Evidence
Use five practical checks to verify an authorized lab fix, preserve before-and-after evidence, and distinguish remediation from mitigation or an inconclusive scan.
Practical cybersecurity guides, labs & compliance
Use five practical checks to verify an authorized lab fix, preserve before-and-after evidence, and distinguish remediation from mitigation or an inconclusive scan.
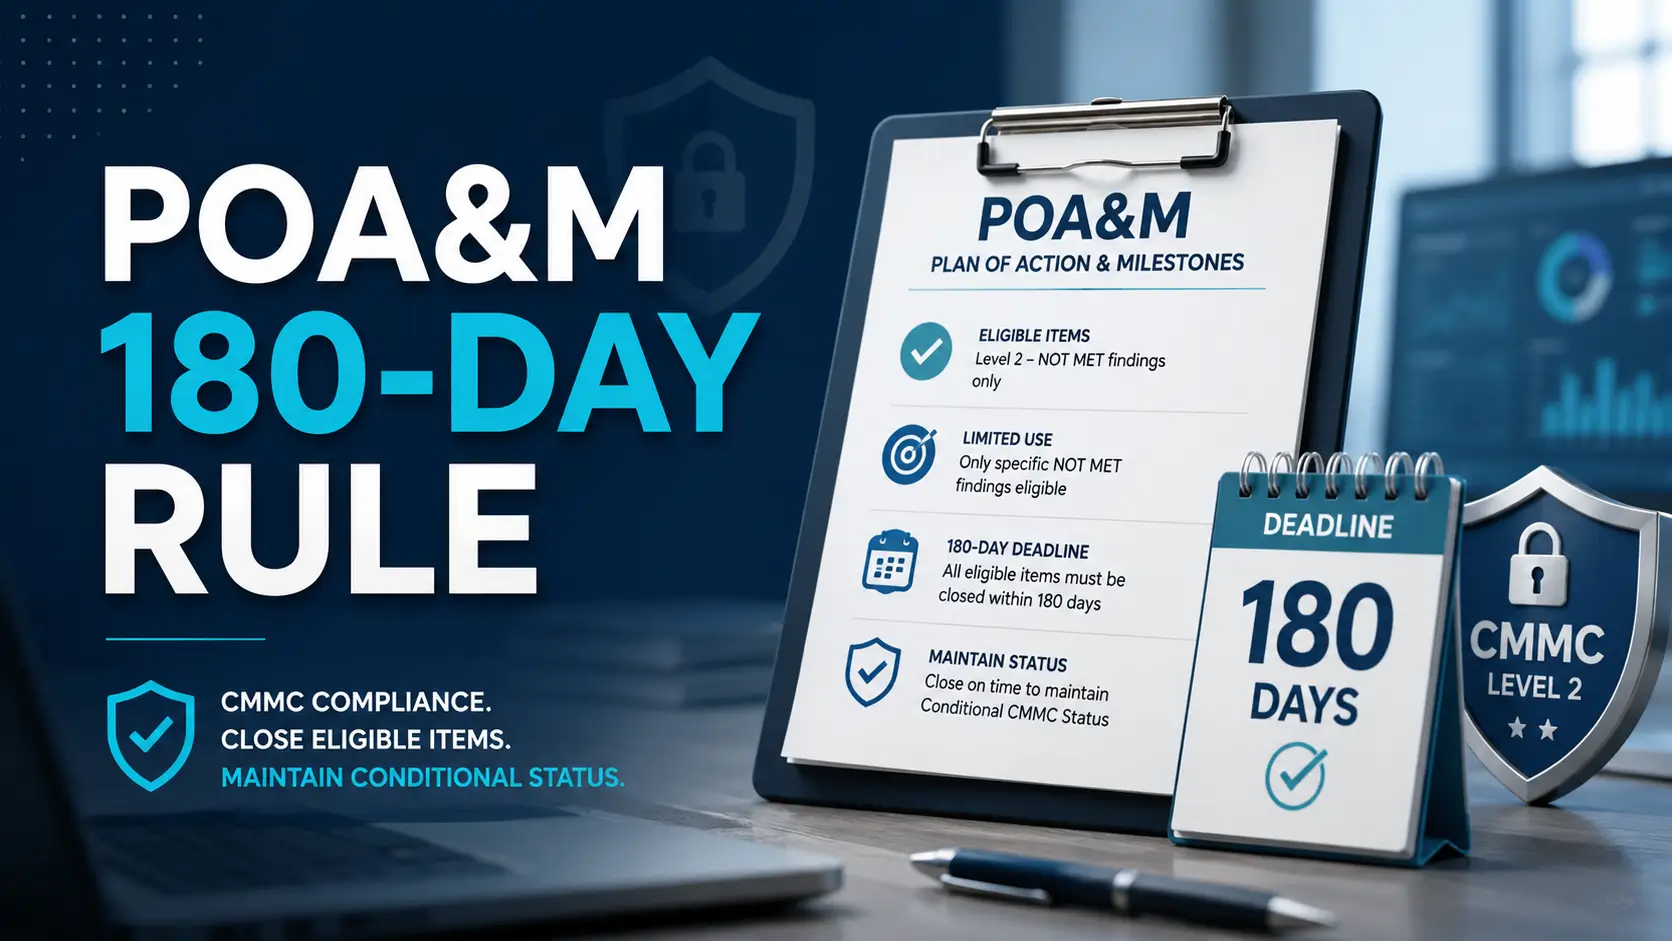
Understand which CMMC assessment gaps belong in a POA&M, how to track remediation, and what evidence to retain. Separate assessment requirements from your everyday security backlog.
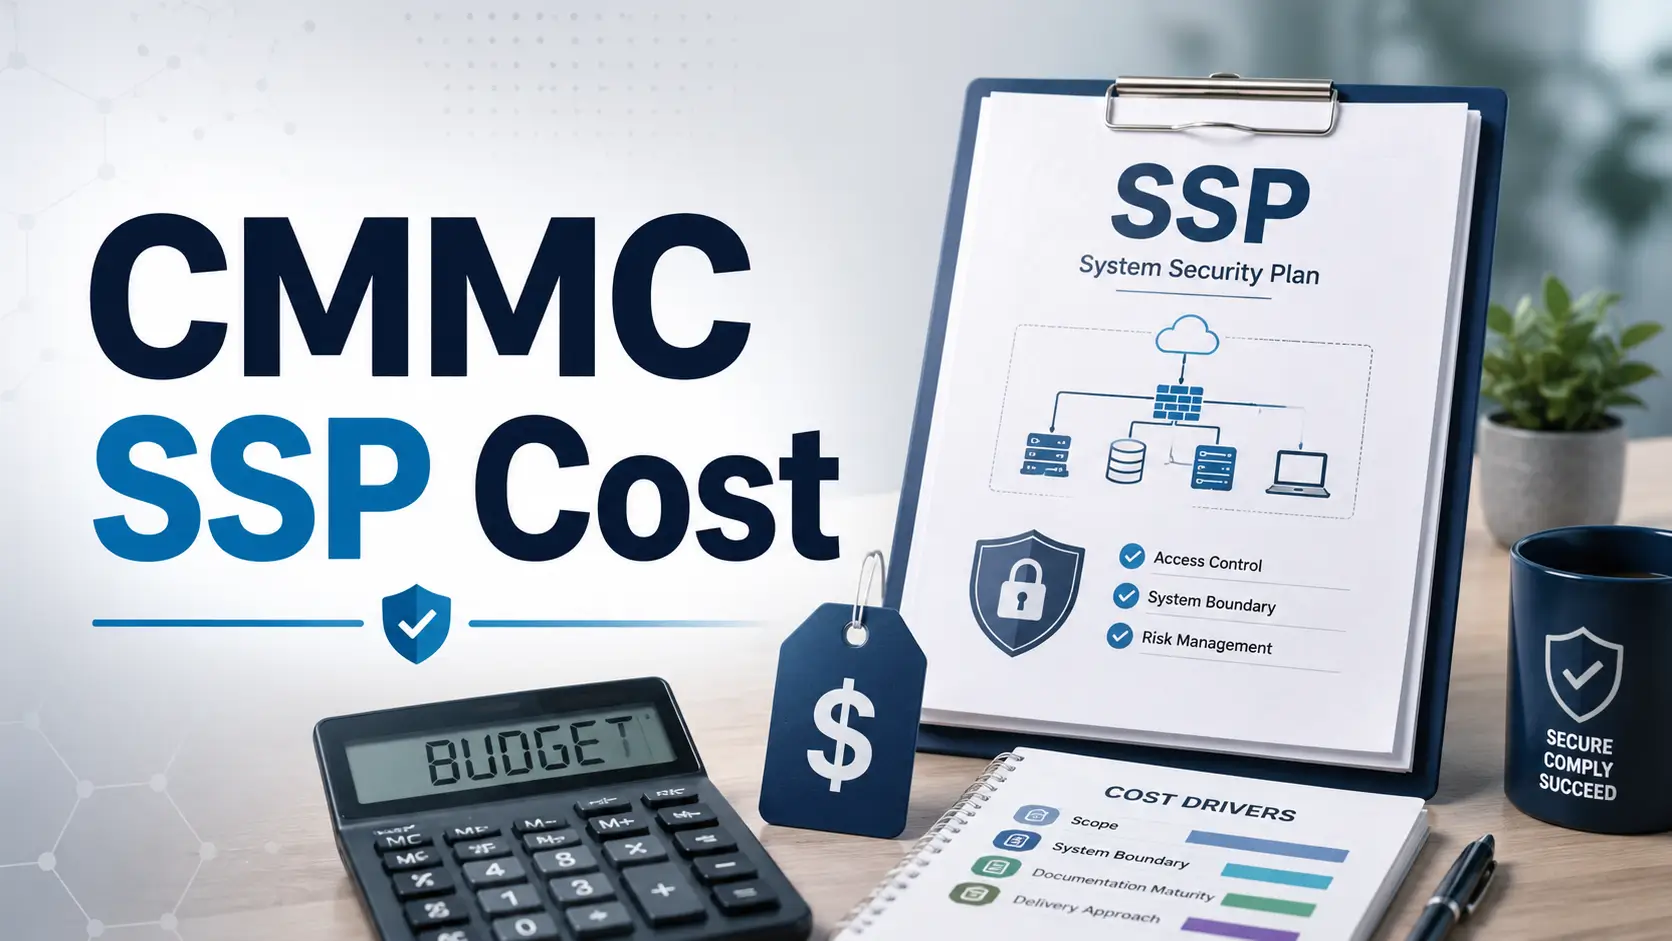
Compare software-assisted SSP documentation, standalone authoring, and broader readiness work. Learn which scope and evidence questions to ask before comparing CMMC System Security Plan quotes.
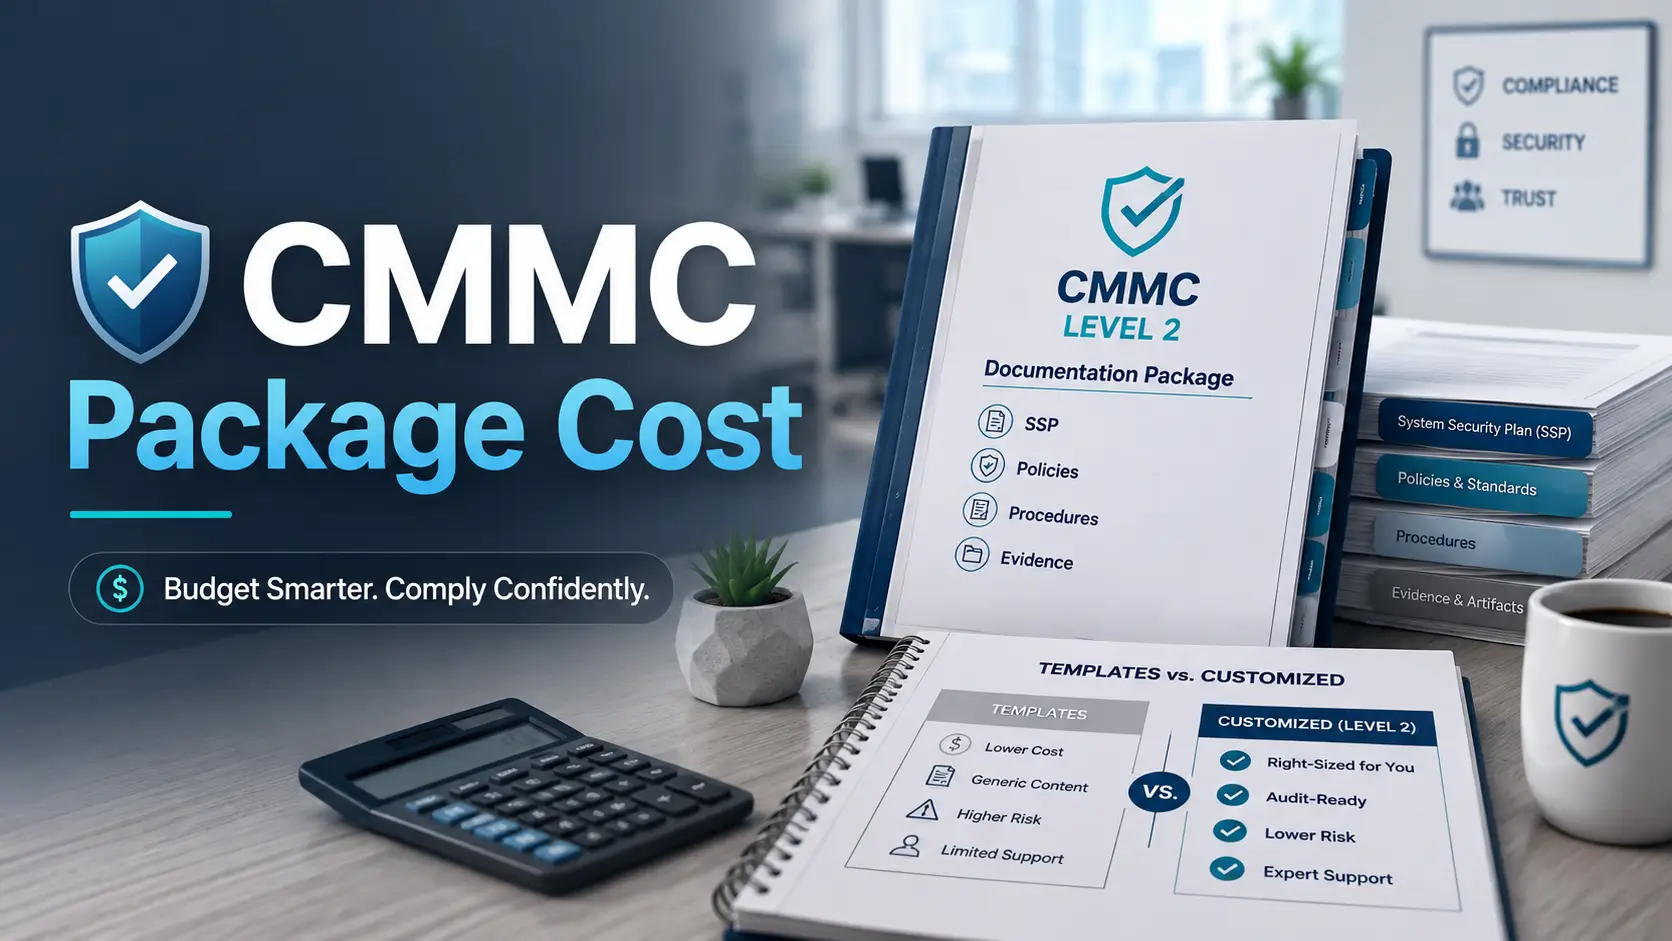
Compare CMMC templates, customized documentation, and full readiness packages. Check what each quote includes and how it maps to your actual environment, responsibilities, and evidence.
Plan a CUI enclave around the people, devices, and workflows that handle controlled information. Compare service scope and recurring costs before requesting quotes.
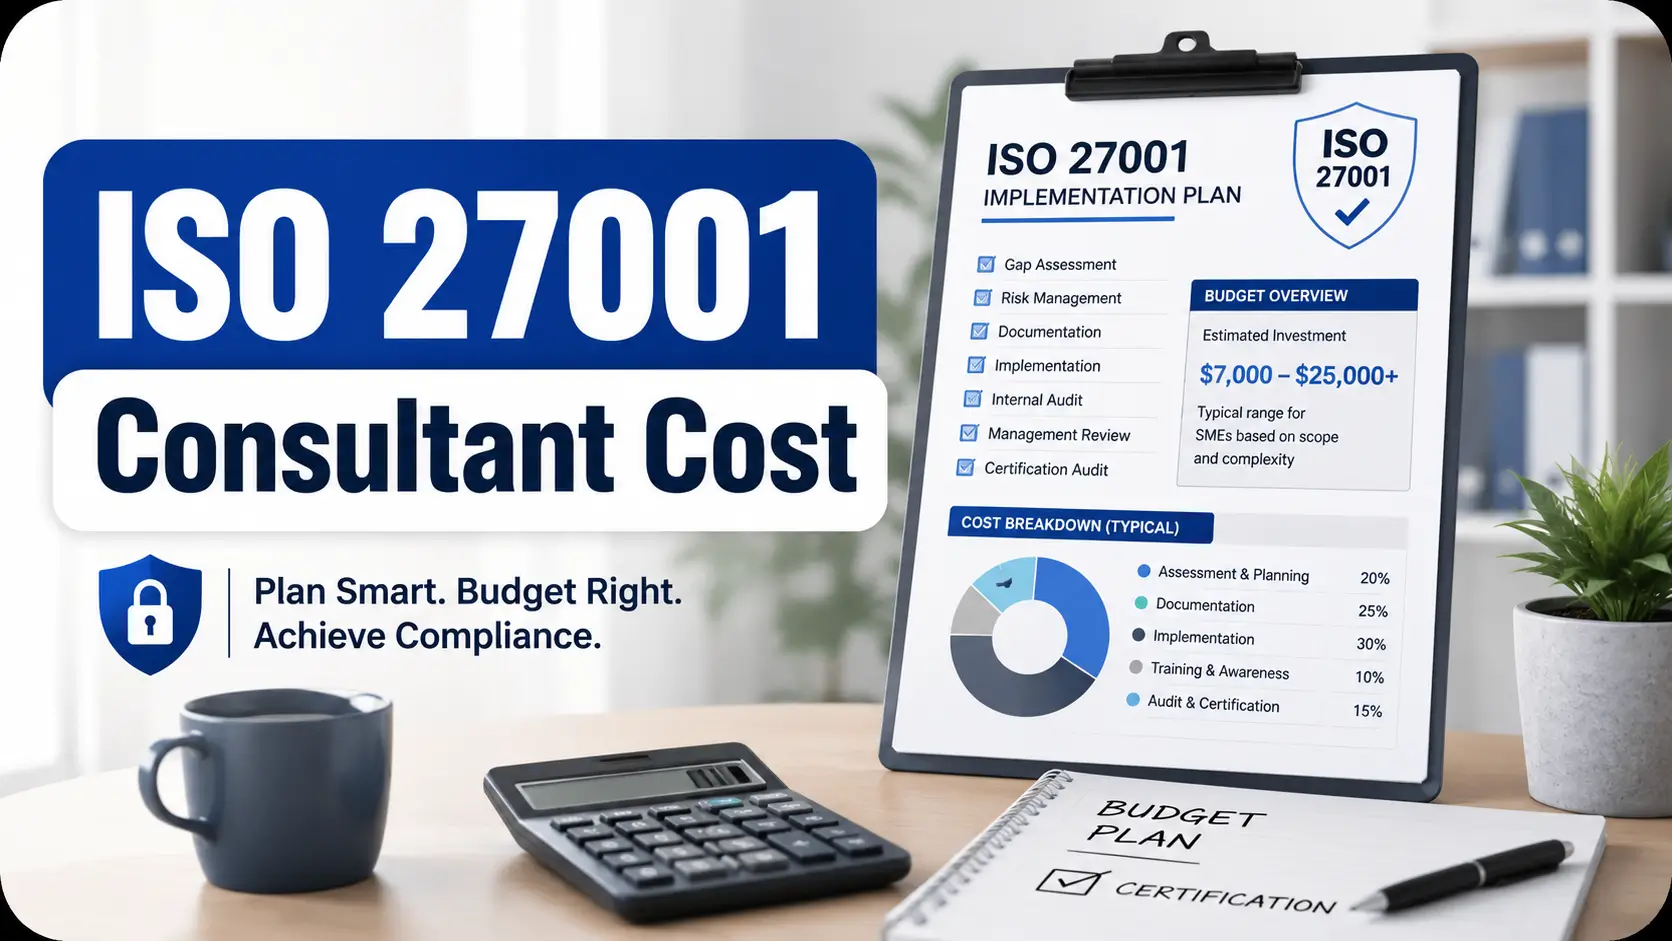
Understand what an ISO 27001 consultant quote covers. Separate implementation help, internal staff effort, remediation, and certification audit costs when planning your budget.
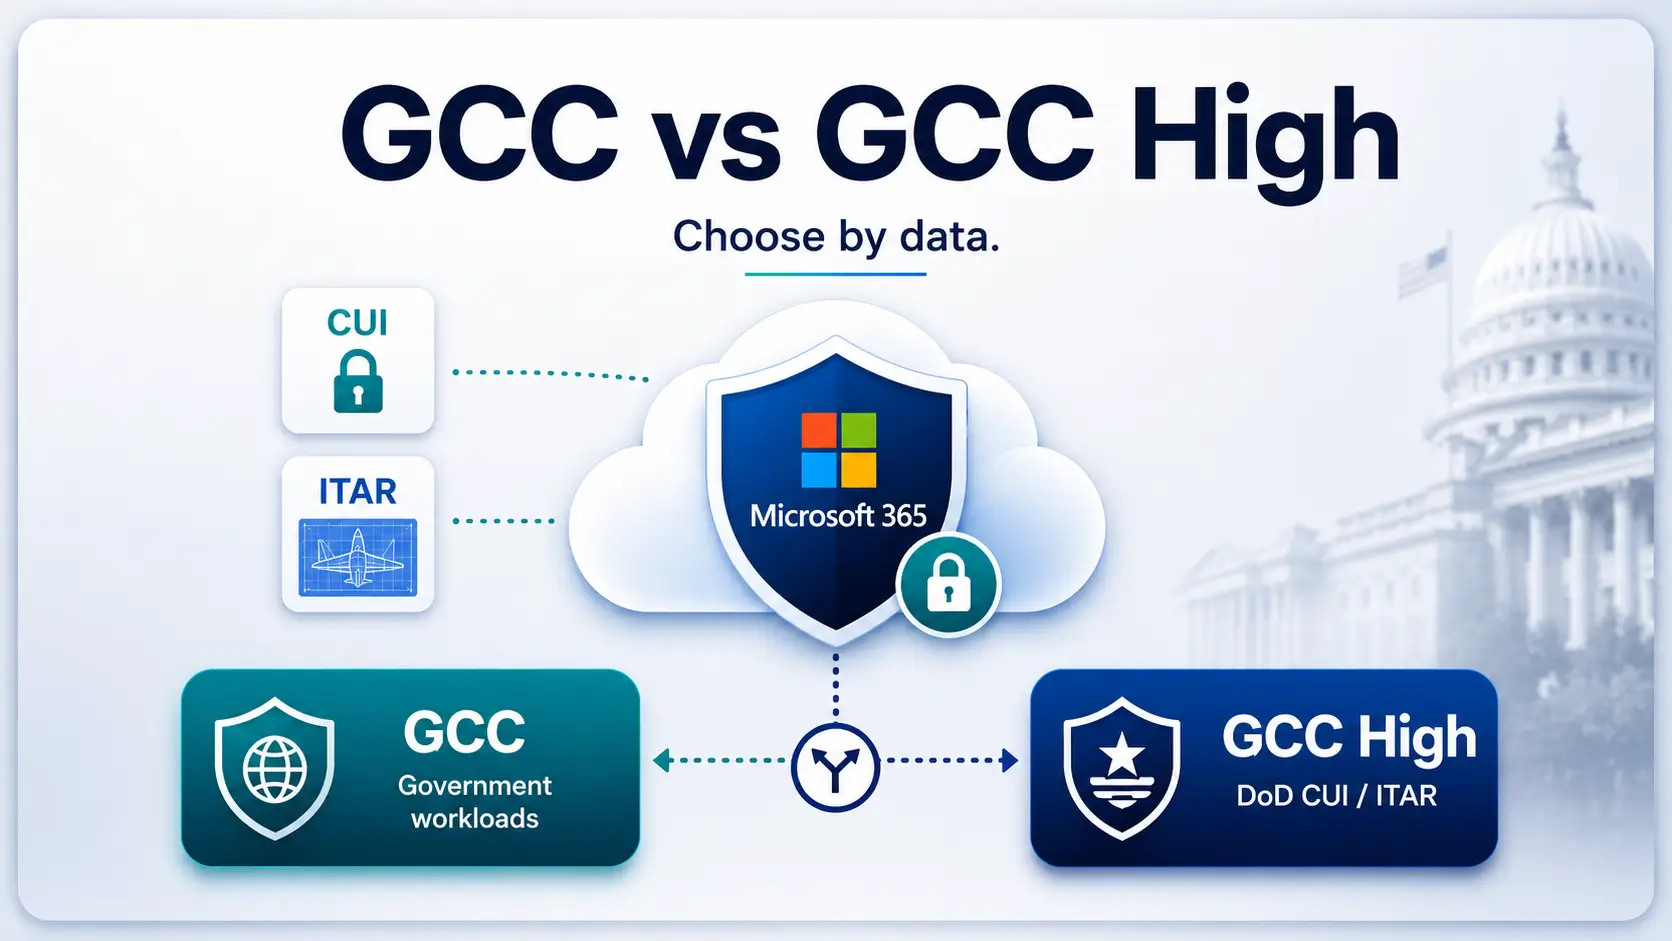
Compare Microsoft 365 GCC and GCC High for defense work. Start with your data types, contract requirements, migration needs, and operating responsibilities.
Compare the scope and cost drivers of SAQ and ROC assessments. Confirm the validation path your payment partners accept before requesting assessment quotes.
Build a GCC High budget that includes licensing, migration, configuration, and ongoing support. Map your CUI users and workflows before deciding what to purchase.
Compare building a CMMC enclave with buying a managed service. Weigh your CUI boundary, internal capacity, recurring costs, and the responsibilities your team retains.