Skip to content

Kioptrix Labs

Practical cybersecurity guides, labs & compliance

  • Home
  • Start Here
    • Beginner Roadmap
  • Downloads
    • Level 1 Setup
    • Level 3 Setup
  • About
    • Privacy Policy
    • Terms of Service & Disclaimer
    • Contact
  • Cybersecurity
  • Kali Linux
  • Compliance Guides
    • PCI DSS
  • All Articles

Cybersecurity

SaaS Security Addendum: Review Obligations Before Signing
October 24, 2026September 13, 2026 by Kioptrix Labs
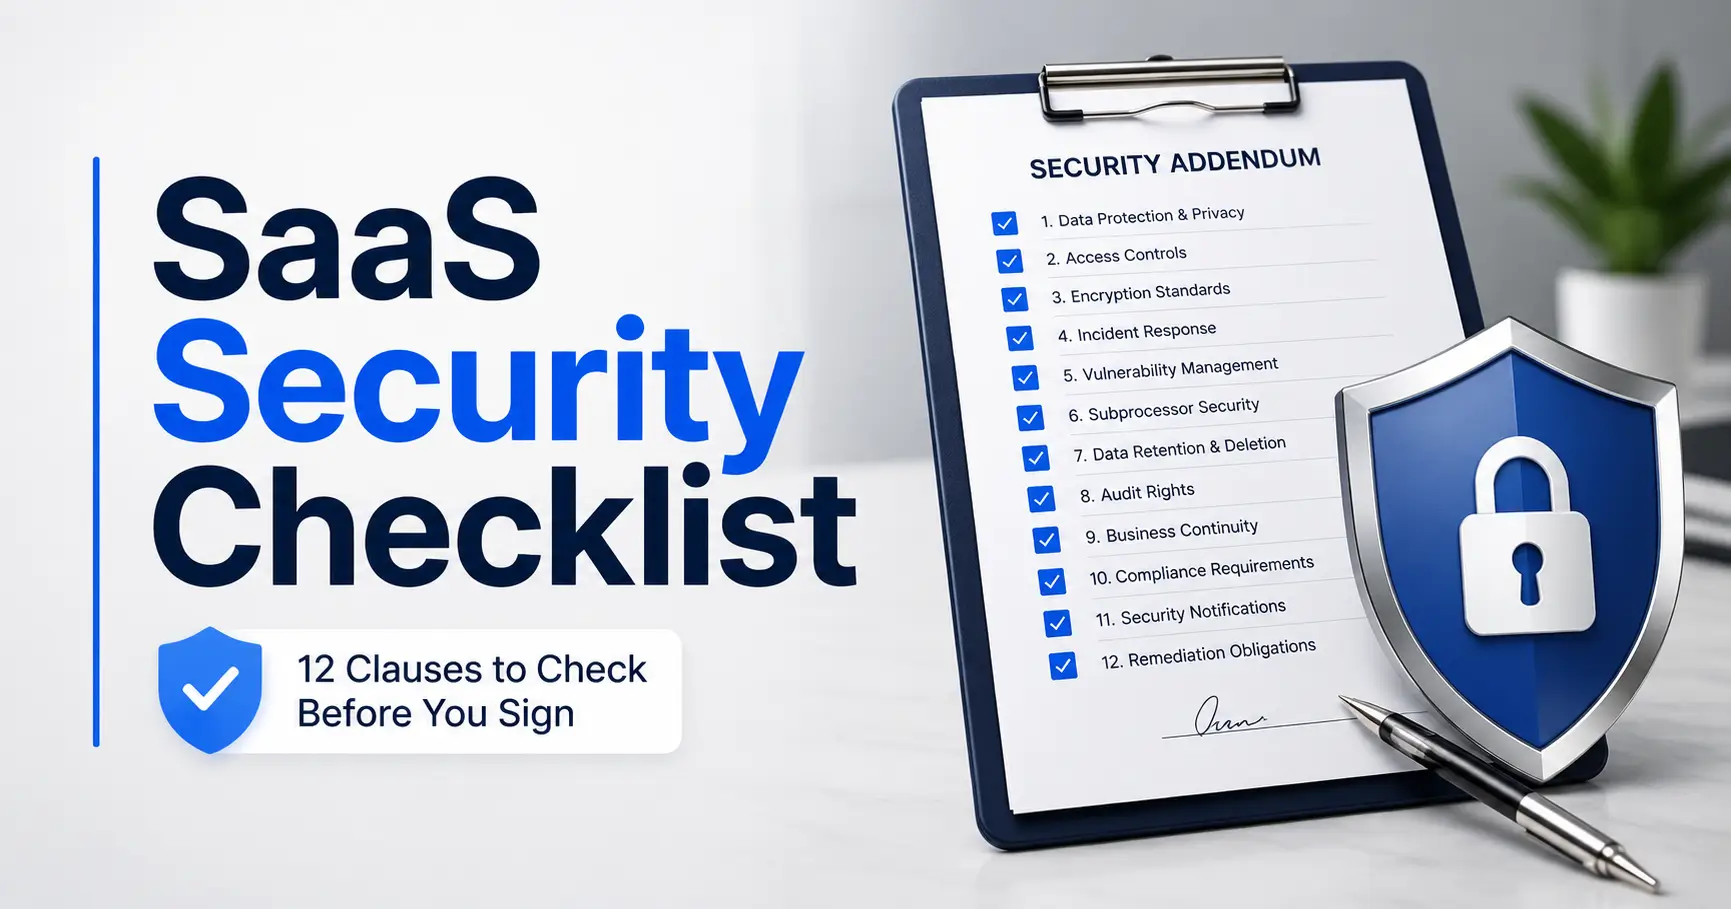
SaaS Security Addendum Checklist

Review a SaaS security addendum against the controls and processes your team can actually support. Check incident triggers, audit scope, subprocessors, deletion and backup exceptions, then record gaps and responsible reviewers before agreeing to commitments.

Categories Cybersecurity Tags Cybersecurity Compliance, SaaS Contracts, SaaS security, Vendor Risk Management

Active Directory Review Without BloodHound: Scope and Coverage

October 24, 2026September 12, 2026 by Kioptrix Labs
Active Directory security audit

Review Active Directory identities, nested privilege, delegated control, GPOs and trusts using authorized evidence. Use the coverage map to record collection limits and relationships that still need investigation.

Categories Pentest for Founders, Cybersecurity Tags Active Directory Security, Cybersecurity Audits, Identity Security, Privileged Access Management

Security Questionnaire Automation: Review Before Reuse

October 24, 2026September 9, 2026 by Kioptrix Labs

Evaluate questionnaire automation using your own review workflow. Compare answer reuse, evidence mapping, access controls and reviewer effort, then use the assertion review record to keep scope, dates and exceptions attached to each answer.

Categories Cybersecurity Tags cybersecurity, GRC Software, SaaS Compliance, Security Questionnaires

Answer Encryption Questions With Scoped Evidence

October 24, 2026September 6, 2026 by Kioptrix Labs
Encryption questionnaire

Answer customer encryption questions by mapping transport, storage, backups and key responsibility. Use the coverage register to connect each statement to dated configuration evidence and disclose exceptions or unreviewed systems.

Categories Cybersecurity Tags Compliance, Encryption, SaaS security, Vendor Risk Management

Cyber Insurance for Freelancers: Check Scope and Terms

October 24, 2026September 5, 2026 by Kioptrix Labs
Cyber insurance for freelancers

Compare proposed cyber insurance with the freelance services, client obligations and data you actually handle. Review definitions, limits, exclusions, consent and reporting terms, and record questions for the insurer or qualified adviser before choosing coverage.

Categories Cybersecurity Tags cyber insurance, Data Breach Protection, Freelancer Insurance, Technology E&O

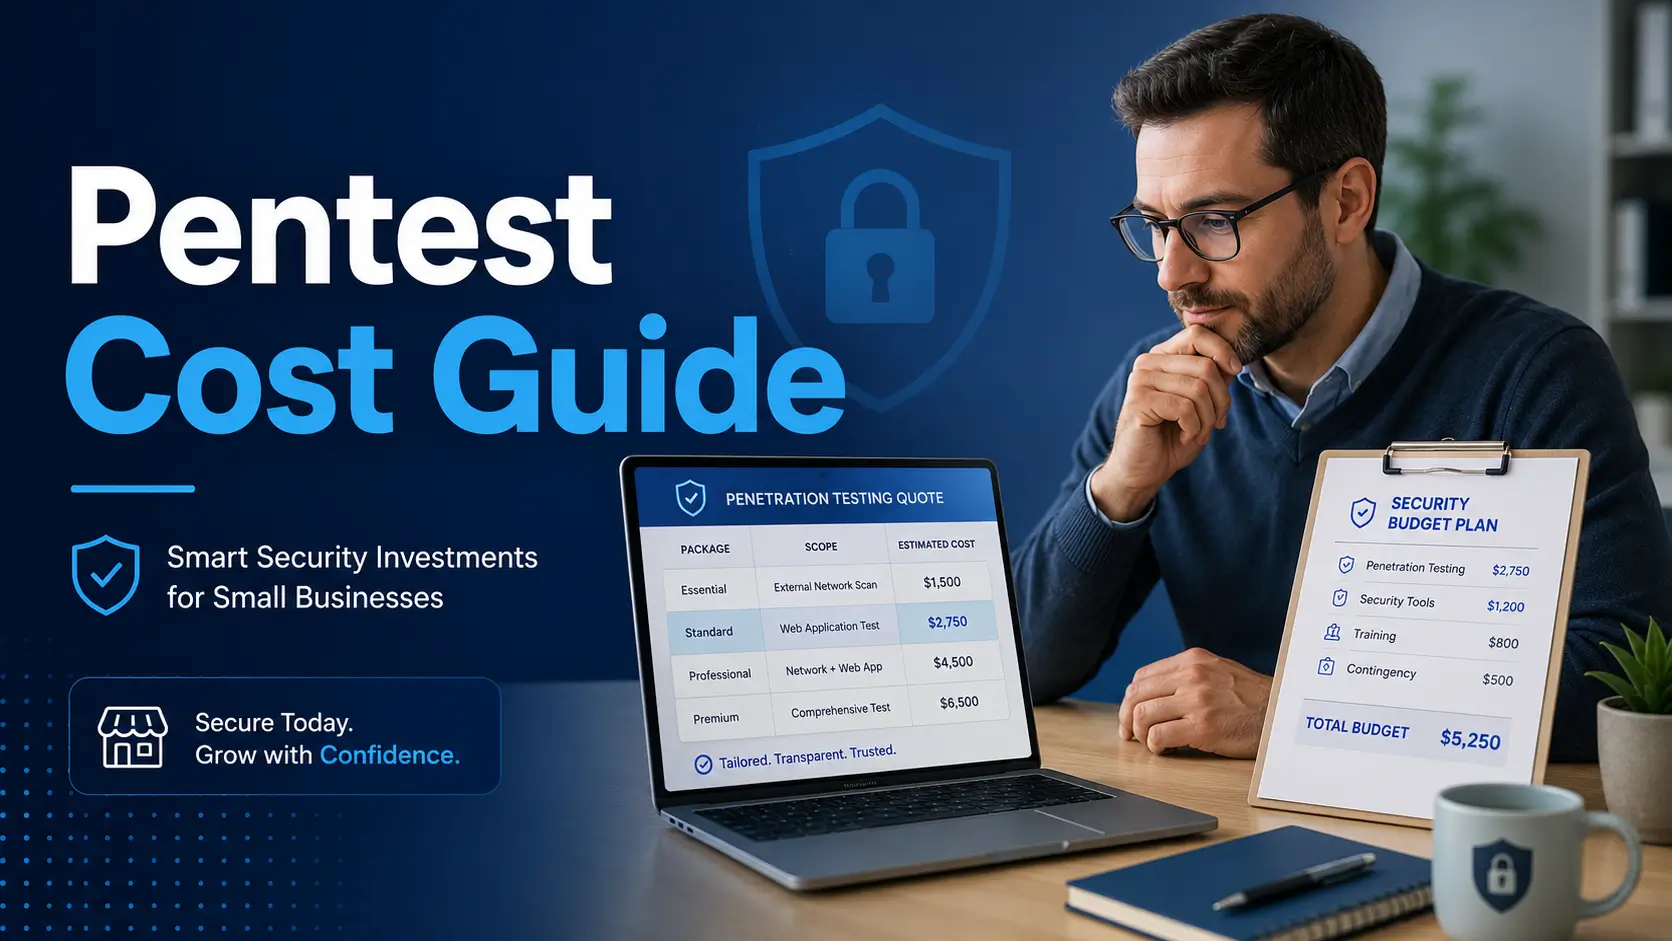
Small-Business Penetration Testing Cost: Scope, Quotes and Retesting

October 24, 2026September 4, 2026 by Kioptrix Labs
Small Business Penetration Testing Cost

Compare small-business pentest proposals using the same assets, roles and workflows. Build a scope brief, check exclusions and retest terms, and keep hypothetical budget examples separate from actual supplier quotes.

Categories Cybersecurity Tags cybersecurity, IT Budgeting, penetration testing, Security Compliance, Small Business Security

SOC 2 Cost for SaaS Startups: Fees, Labor and Budget Examples

October 24, 2026September 3, 2026 by Kioptrix Labs
SOC 2 cost for SaaS startups

Build a SaaS startup SOC 2 budget from examination scope, readiness, software, remediation and staff work. Keep external cash and internal labor separate, compare equivalent CPA proposals, and avoid double-counting bundled services.

Categories Cybersecurity Tags cybersecurity, SaaS Compliance, SOC 2, Startup Costs

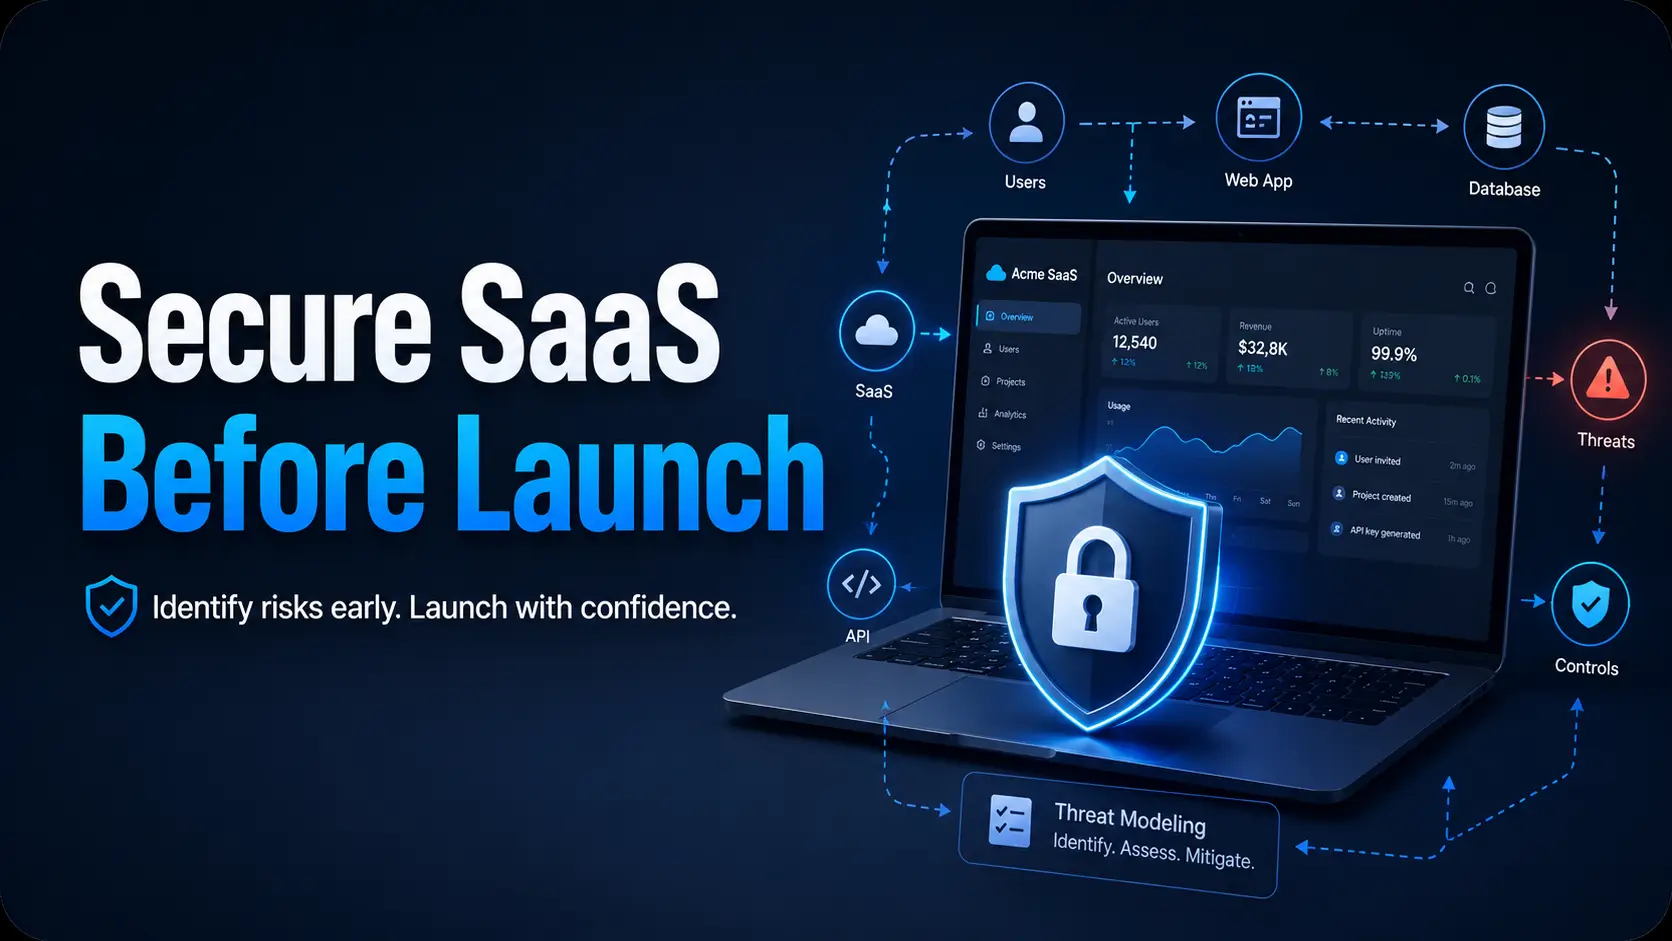
MVP Threat Modeling: Data Flows and Decisions

October 24, 2026September 1, 2026 by Kioptrix Labs
MVP threat modeling for startups

Trace one MVP data flow and its trust boundaries. Use the threat-to-test sheet to turn plausible misuse into mitigation owners, engineering tasks and acceptance checks, while recording assumptions outside the model.

Categories Cybersecurity Tags application security, SaaS security, Startup Cybersecurity, Threat Modeling

rpcclient Access Denied: Separate Connection and Calls

October 24, 2026August 31, 2026 by Kioptrix Labs
rpcclient NT_STATUS_ACCESS_DENIED

Troubleshoot rpcclient access denied by separating connection, authentication and the rejected RPC call. Capture the identity, interface, exact operation and status in a denial-stage record before choosing the next permitted check.

Categories Cybersecurity Tags Active Directory, Linux Administration, rpcclient, Samba, SMB troubleshooting

API Security Checklist: Test Authorization Boundaries

October 24, 2026August 30, 2026 by Kioptrix Labs
API security checklist for SaaS founders

Test scoped API authorization across roles, object ownership and tenant boundaries. Use the expectation matrix and two-tenant drill to record allowed and denied operations, supporting evidence and endpoints still unreviewed.

Categories Cybersecurity Tags API security, cybersecurity, penetration testing, SaaS security, Startup Compliance
Older posts
Newer posts
← Previous Page1 … Page5 Page6 Page7 … Page9 Next →

Choose your next step

Browse guides by task

Hands-on labs

  • Set up Level 1
  • Fix a VM or network error
  • Choose the next check
  • Walkthrough & hints

Records & projects

  • Copy a lab session note
  • Create a review record
  • Present a learning project

Business security

  • Choose a compliance framework
  • CMMC preparation
  • FedRAMP budgeting

All articles · Author & evidence policy

E-mail:

dalo78@naver.com

  • About
  • All Articles
  • Find a Guide
  • Kioptrix Downloads
  • Kioptrix Level 1 Download & Setup Guide
  • Kioptrix Level 3 Download & Setup Guide
  • Privacy Policy
  • Start Here: Kioptrix Labs, Tools & Security Guides
  • Terms of Service & Disclaimer
© 2026 Kioptrix Labs • Built with GeneratePress