NoSQL Injection Labs: Check Query Construction
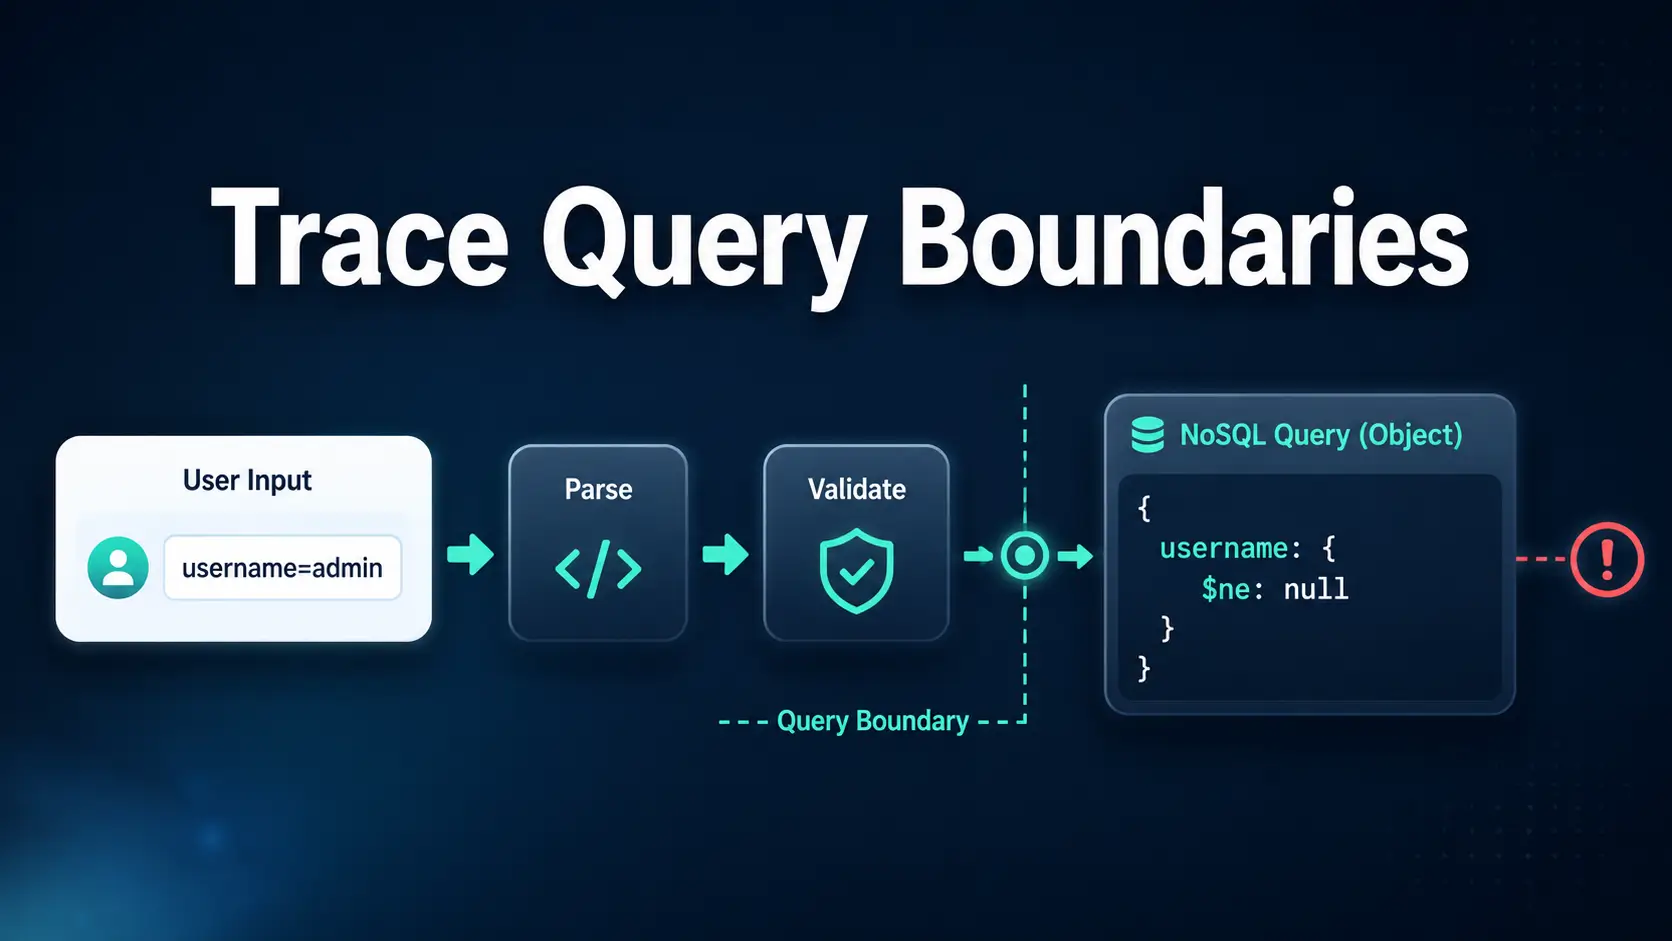
Trace one NoSQL input from its parser and expected type to the database query. Use the query-boundary review and worked example to document observed behavior, remaining uncertainty and repair checks.
Practical cybersecurity guides, labs & compliance
Trace one NoSQL input from its parser and expected type to the database query. Use the query-boundary review and worked example to document observed behavior, remaining uncertainty and repair checks.
Start Kali web testing with one security expectation and a bounded request. Use the question record and worked comparison to connect tool output with application state, evidence and the limits of your conclusion.
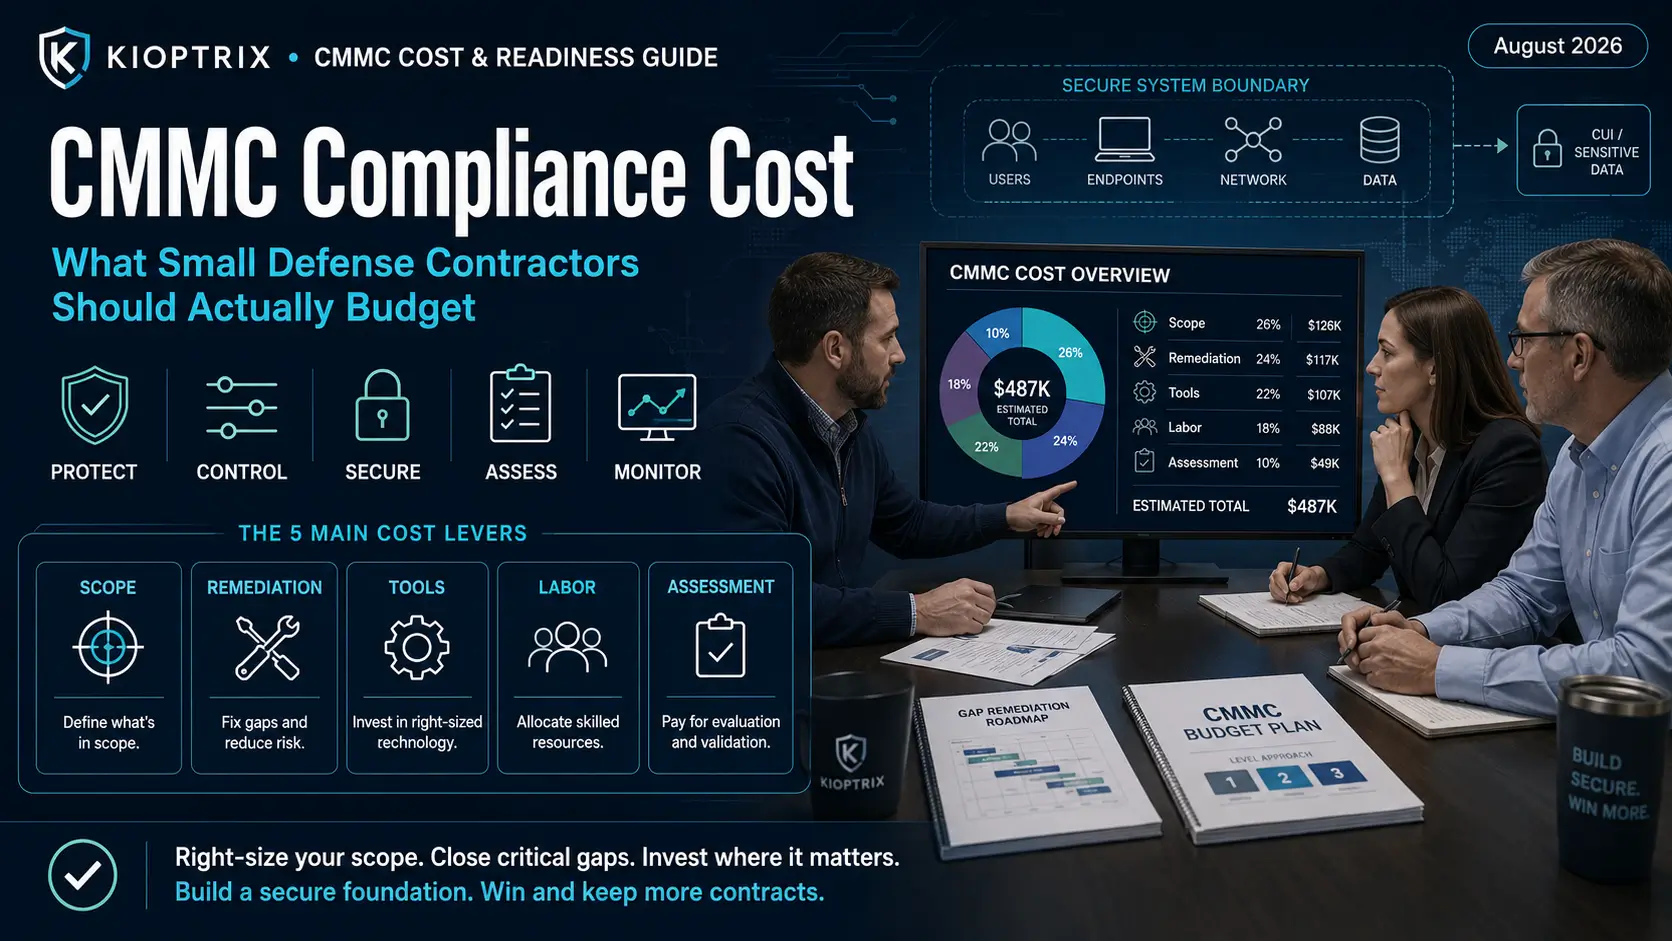
Build a CMMC budget from the actual contract, scope and assessment path. Separate historical government models, supplier quotes, remediation, internal capacity and recurring costs.
Create a pentest report with a blank summary and evidence-linked findings. Record assessment scope, observed behavior, conditional impact and remediation, then distinguish planned retests from verified closure using the review checklist.
Review Kali packages kept back before accepting an APT transaction. Check repositories, dependencies and proposed removals, then use the transaction record to capture the plan, recovery point and actual outcome.
Plan and verify an MFA rollout across real accounts, access paths and recovery routes. Use the enforcement coverage record to track representative tests, exceptions and accountable owners beyond enrollment counts.
Compare the exact OSCP, CEH and PNPT credential packages, assessment formats and role requirements. Separate provider prices and occupation-wide salary data from hiring or pay guarantees.
Define a permitted web-lab exercise and the security boundary you expect. Use the boundary record and worked example to preserve controlled observations, compare explanations and avoid unsupported vulnerability claims.
Map an ecommerce incident to policy wording, retentions, exclusions and third-party dependencies. Use the incident-to-policy record to prepare questions for comparable insurance quotes.
Review a proposed privilege-escalation path against the identity, permissions and prerequisites actually observed. Use the hypothesis filter to choose the next authorized check and document absent evidence or an unchanged boundary.